
Clear Path Security
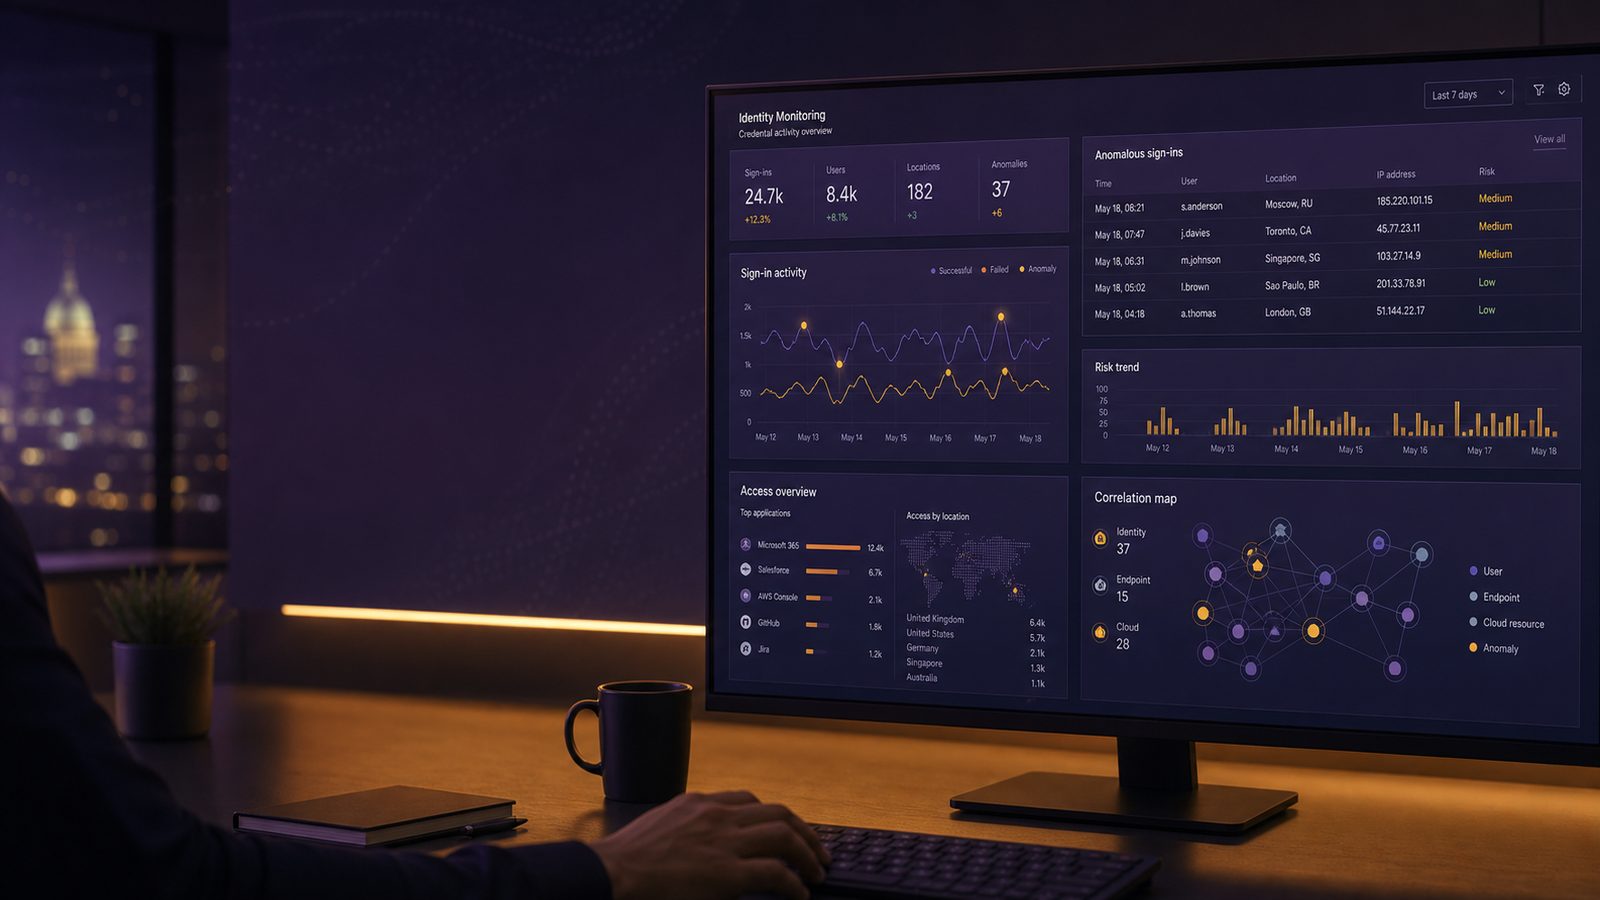
Detecting credential theft and misuse patterns for UK SMEs
Detecting credential theft and misuse patterns for UK SMEs Credential theft is often less about a dramatic[…]
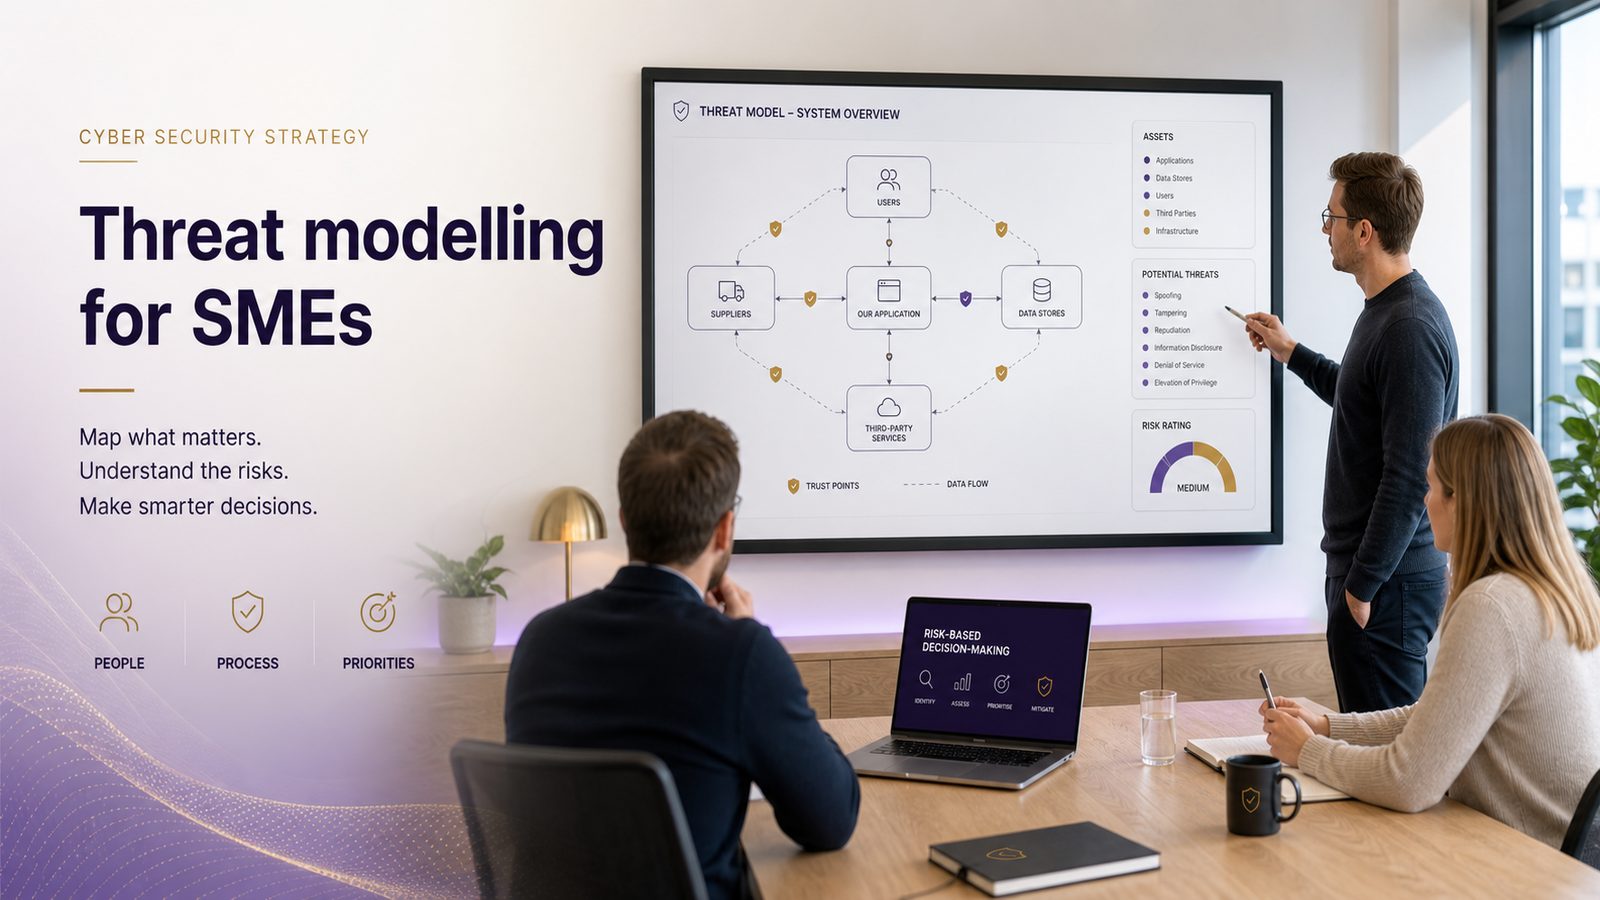
Threat modelling concepts explained for SMEs
Threat modelling concepts explained for SMEs For many small and medium-sized businesses, cyber security can feel like[…]
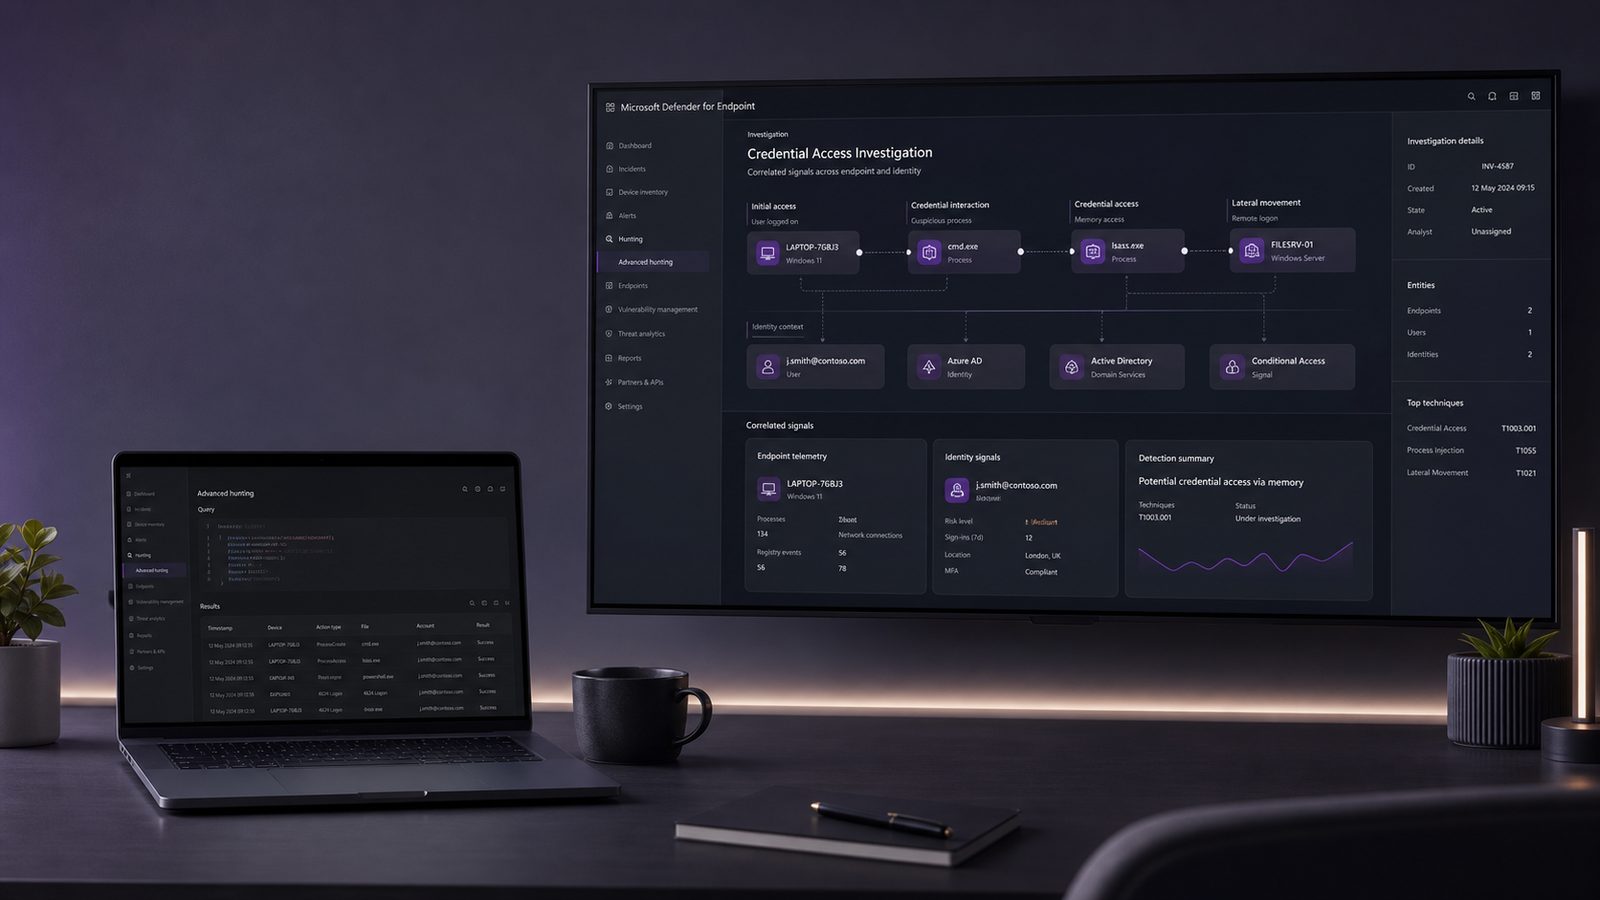
Memory and credential attack detection with Defender for Endpoint
Memory-resident attacks and credential abuse are two of the more important detection areas for modern endpoint defence.[…]
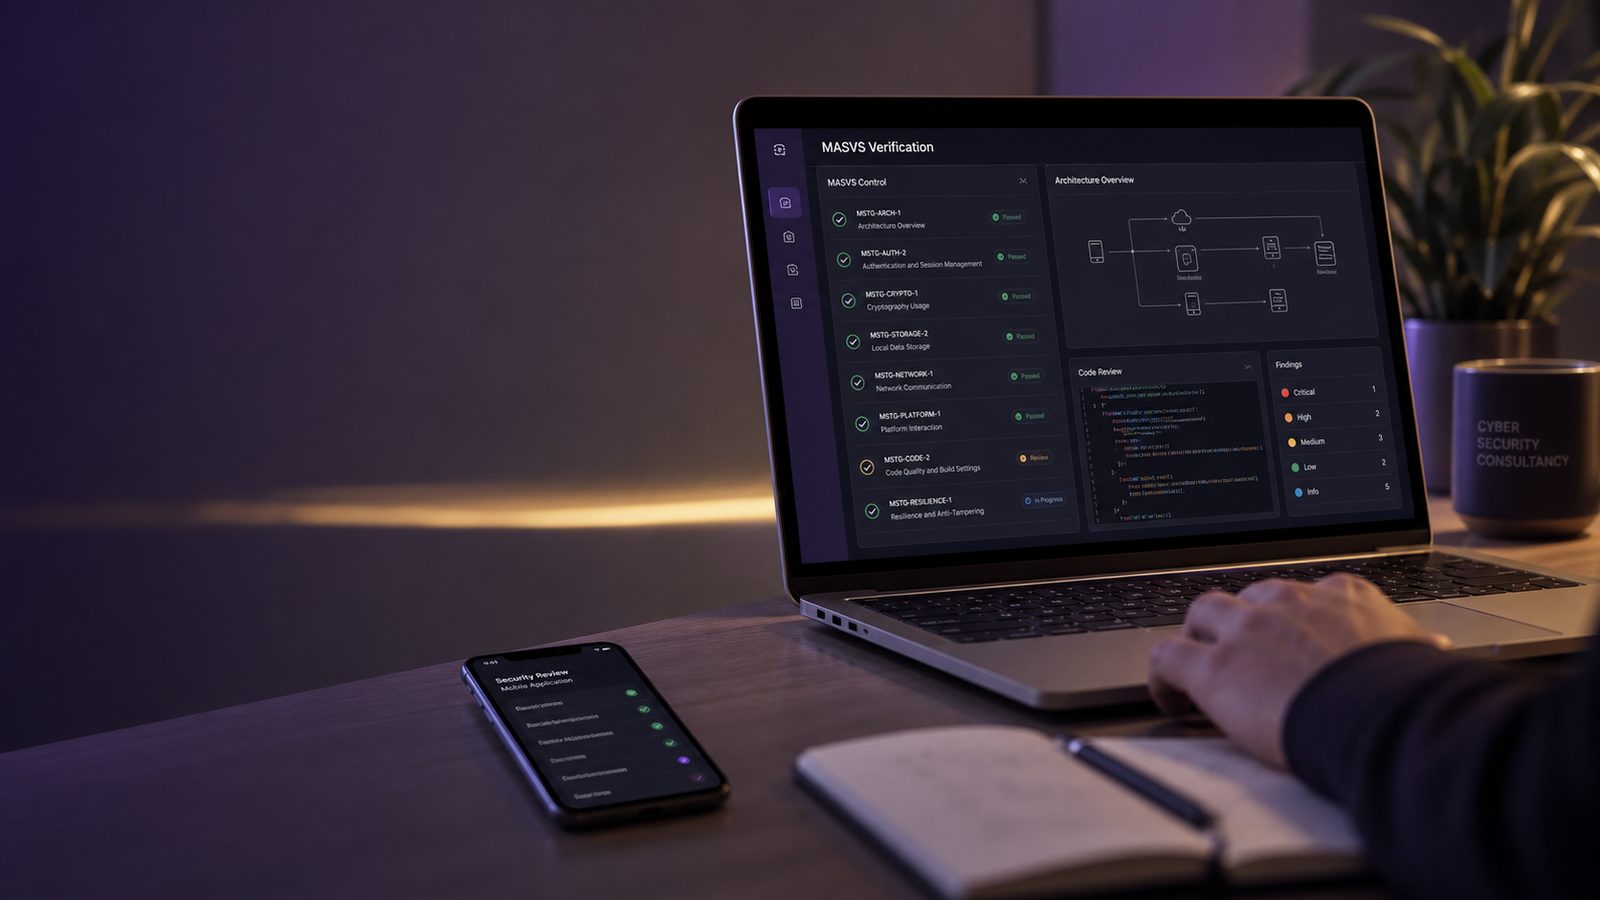
Applying OWASP MASVS for mobile application security
Applying OWASP MASVS for mobile application security OWASP MASVS (Mobile Application Security Verification Standard) is the baseline[…]
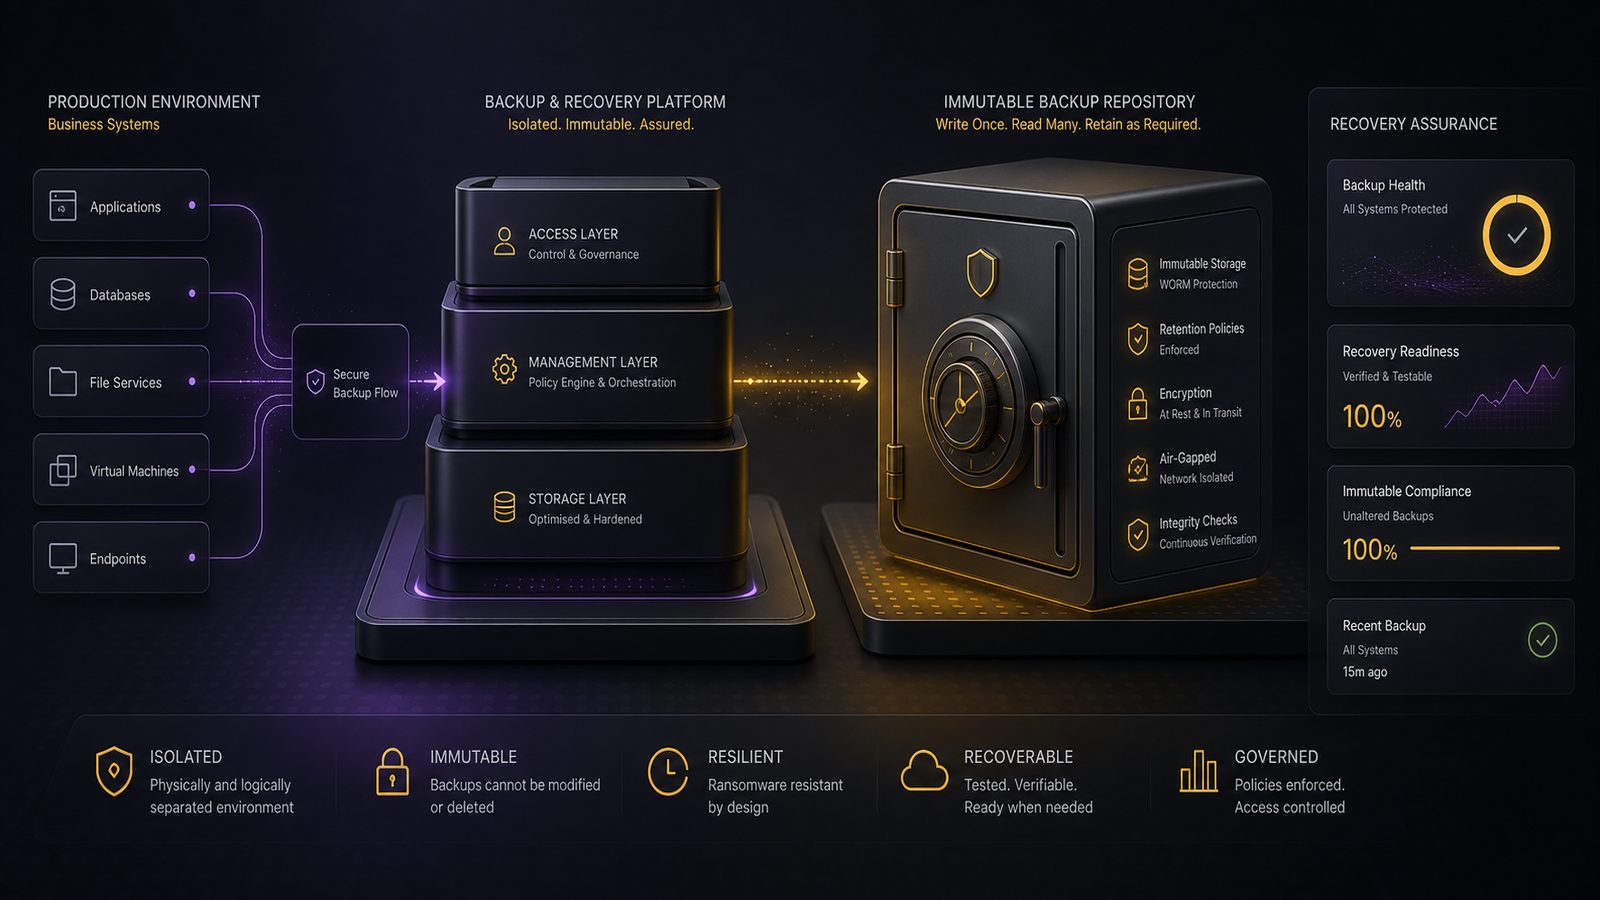
Designing immutable backup solutions to resist ransomware
Designing immutable backup solutions to resist ransomware Ransomware planning is often framed as a prevention problem, but[…]
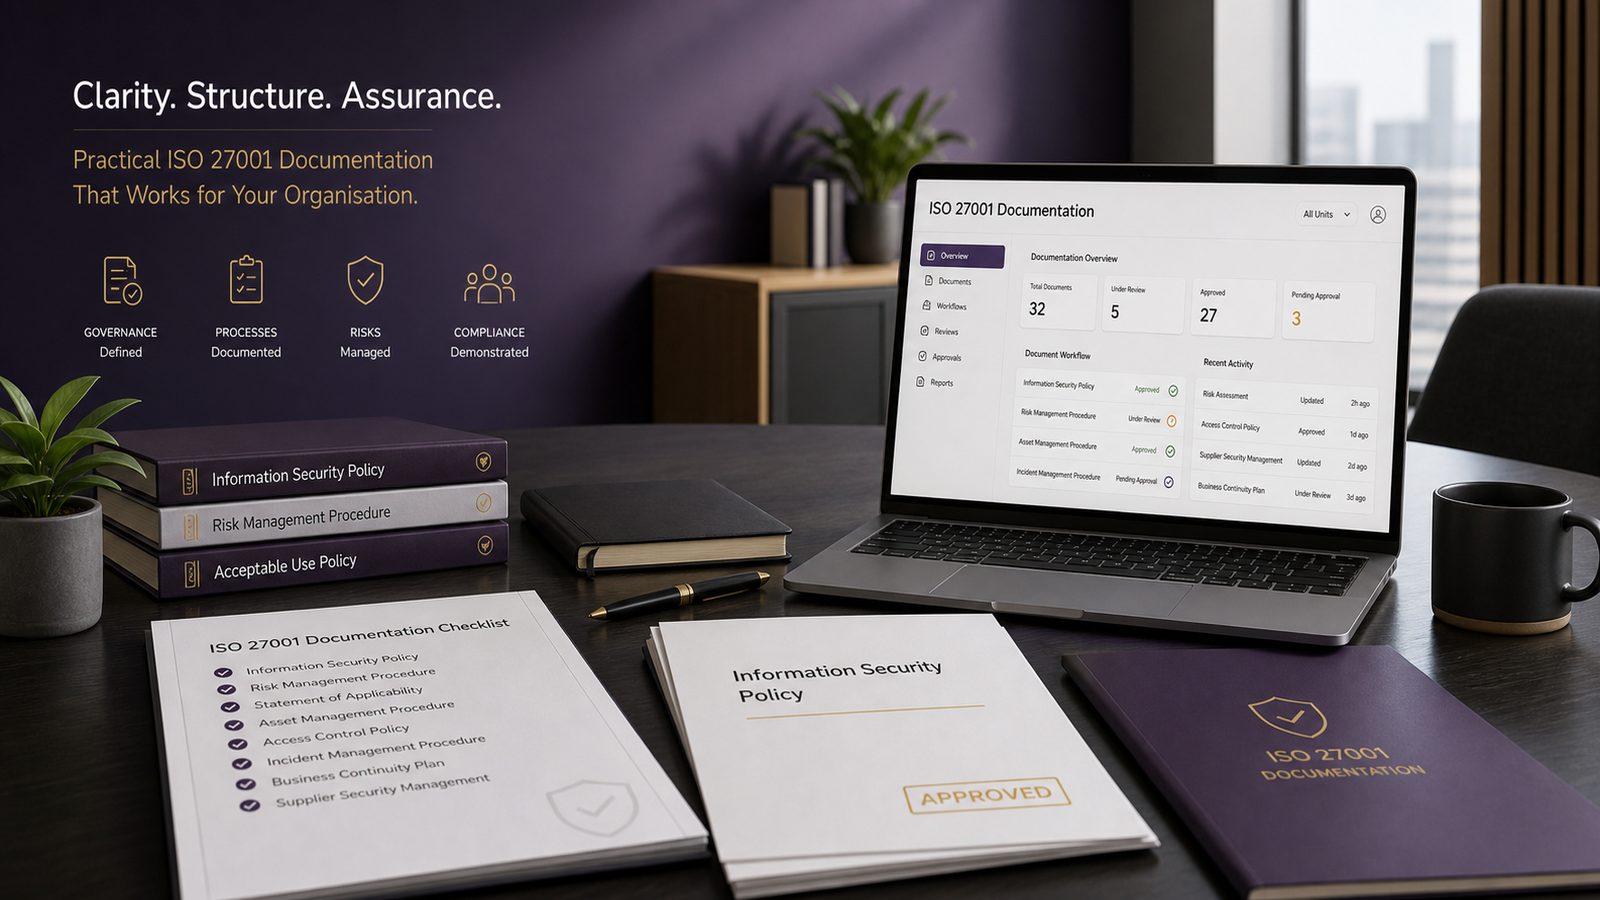
Policies and procedures required by ISO 27001: a practical guide for UK SMEs
Policies and procedures required by ISO 27001: a practical guide for UK SMEs If you are trying[…]
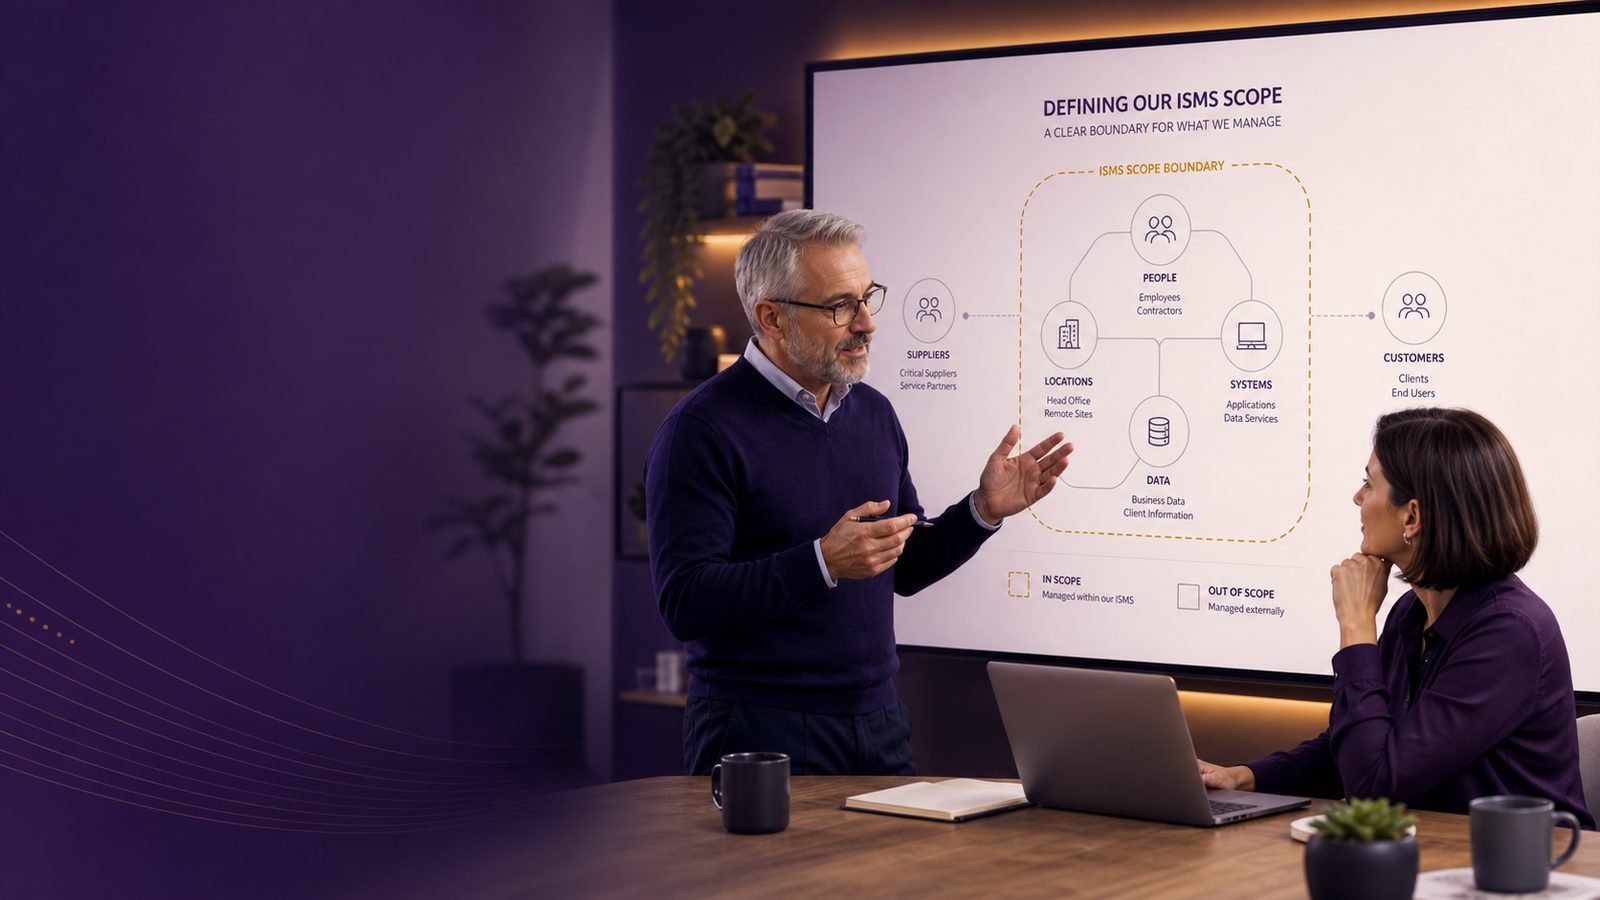
ISMS scope definition for small organisations
ISMS scope definition for small organisations ISMS scope is the written boundary of your information security management[…]
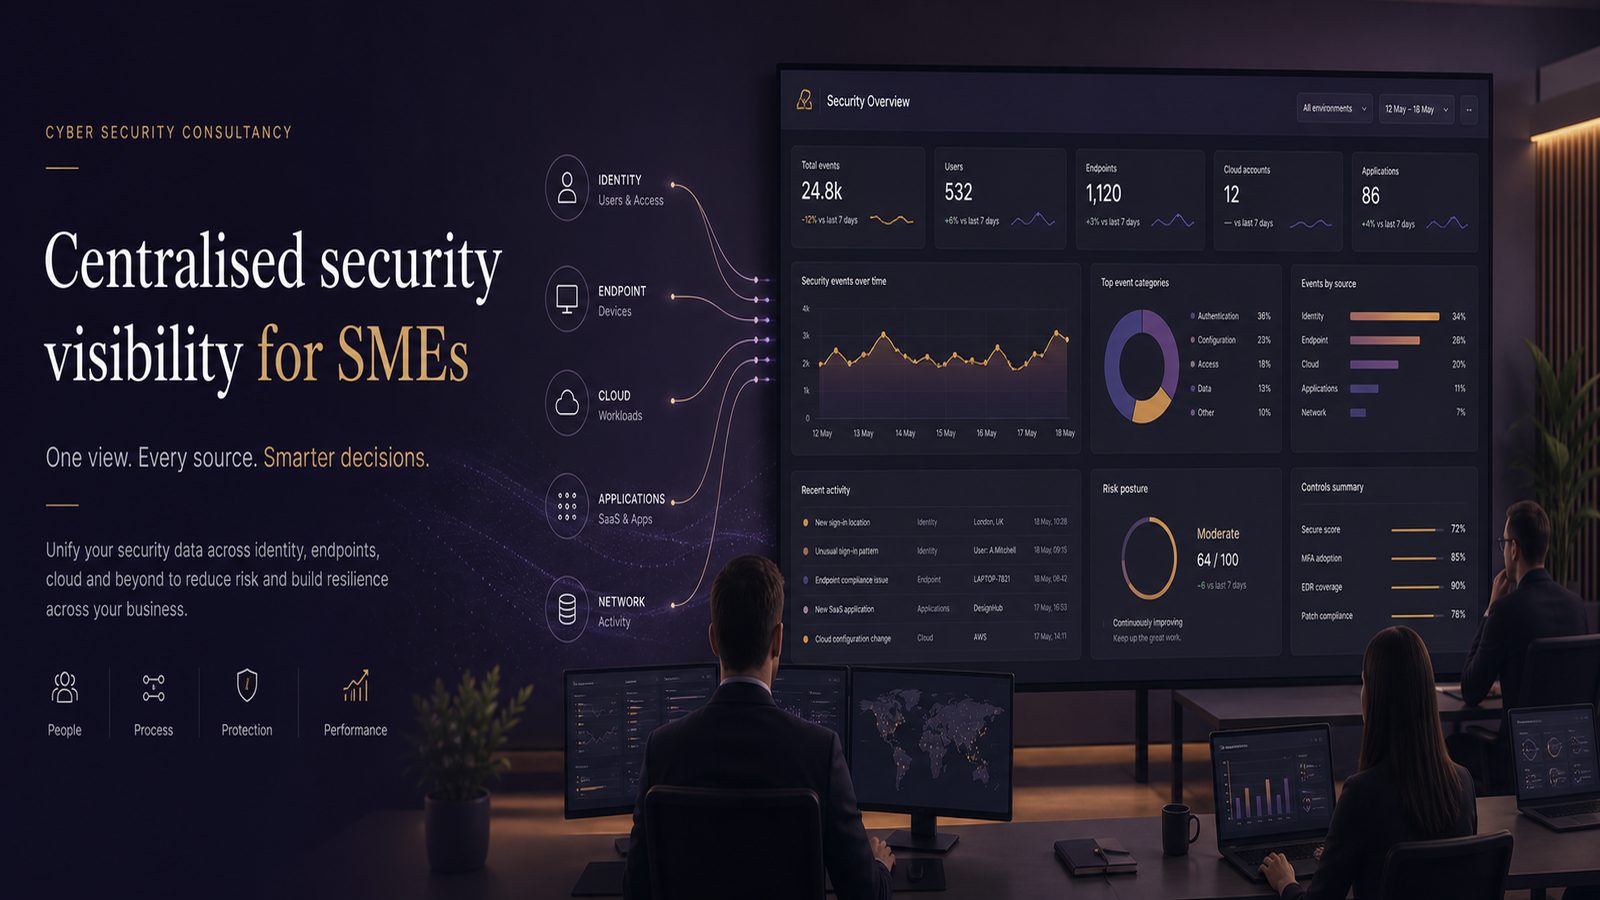
Centralised security visibility explained for SMEs
Centralised security visibility explained for SMEs For many SMEs, the real problem is not a complete lack[…]
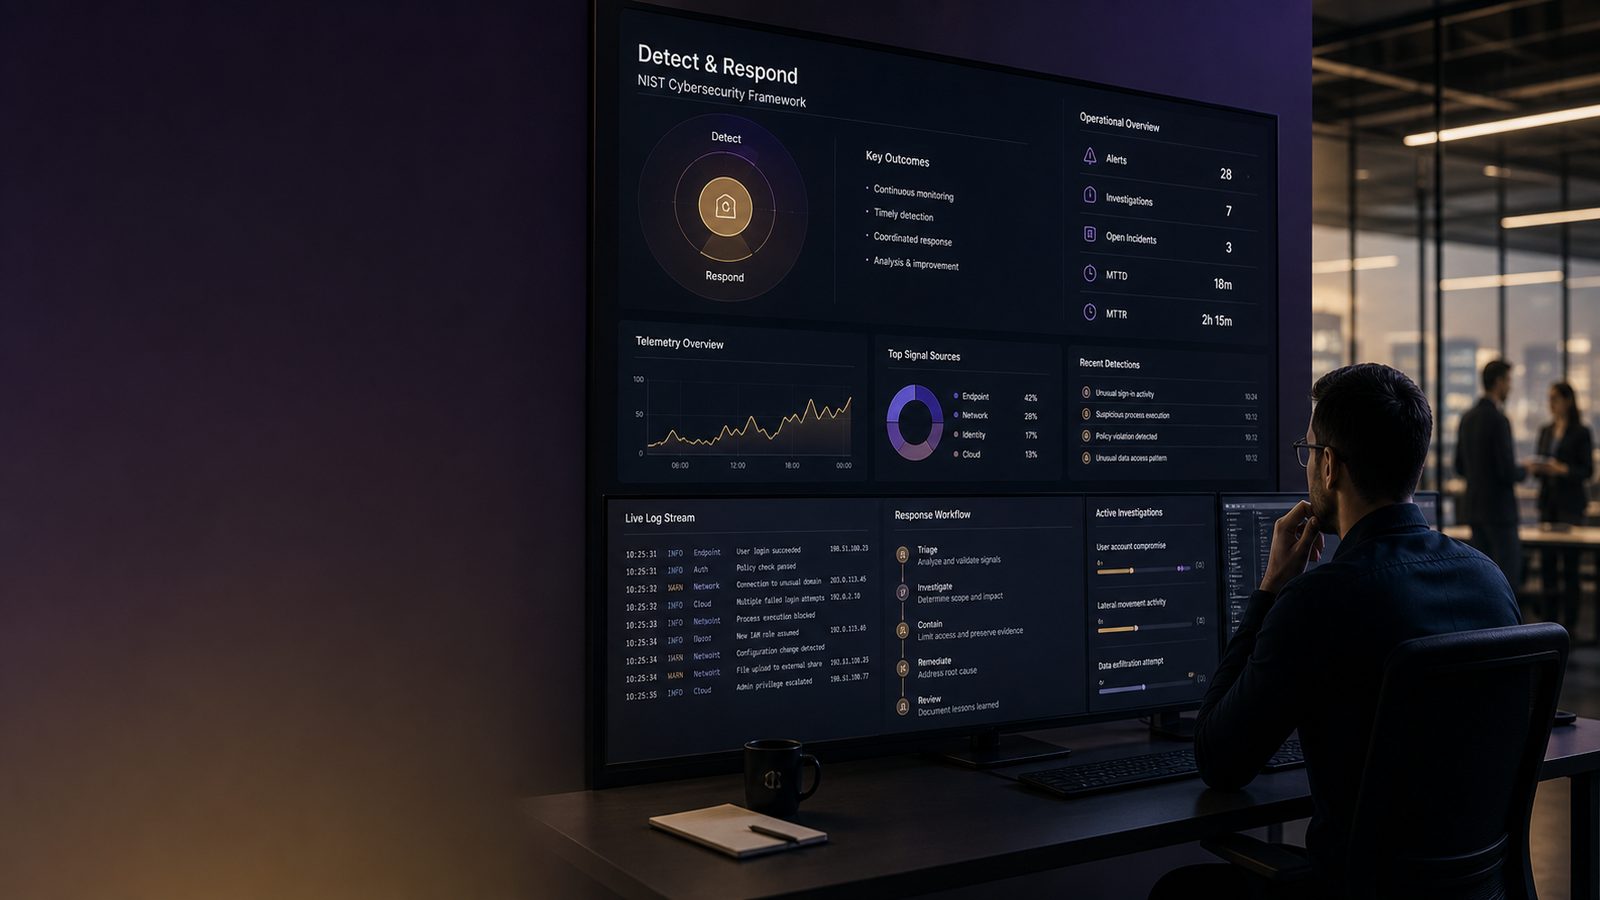
Implementing Detect and Respond functions in NIST CSF
Implementing Detect and Respond functions in NIST CSF In NIST CSF 2.0 the Detect function covers continuous[…]
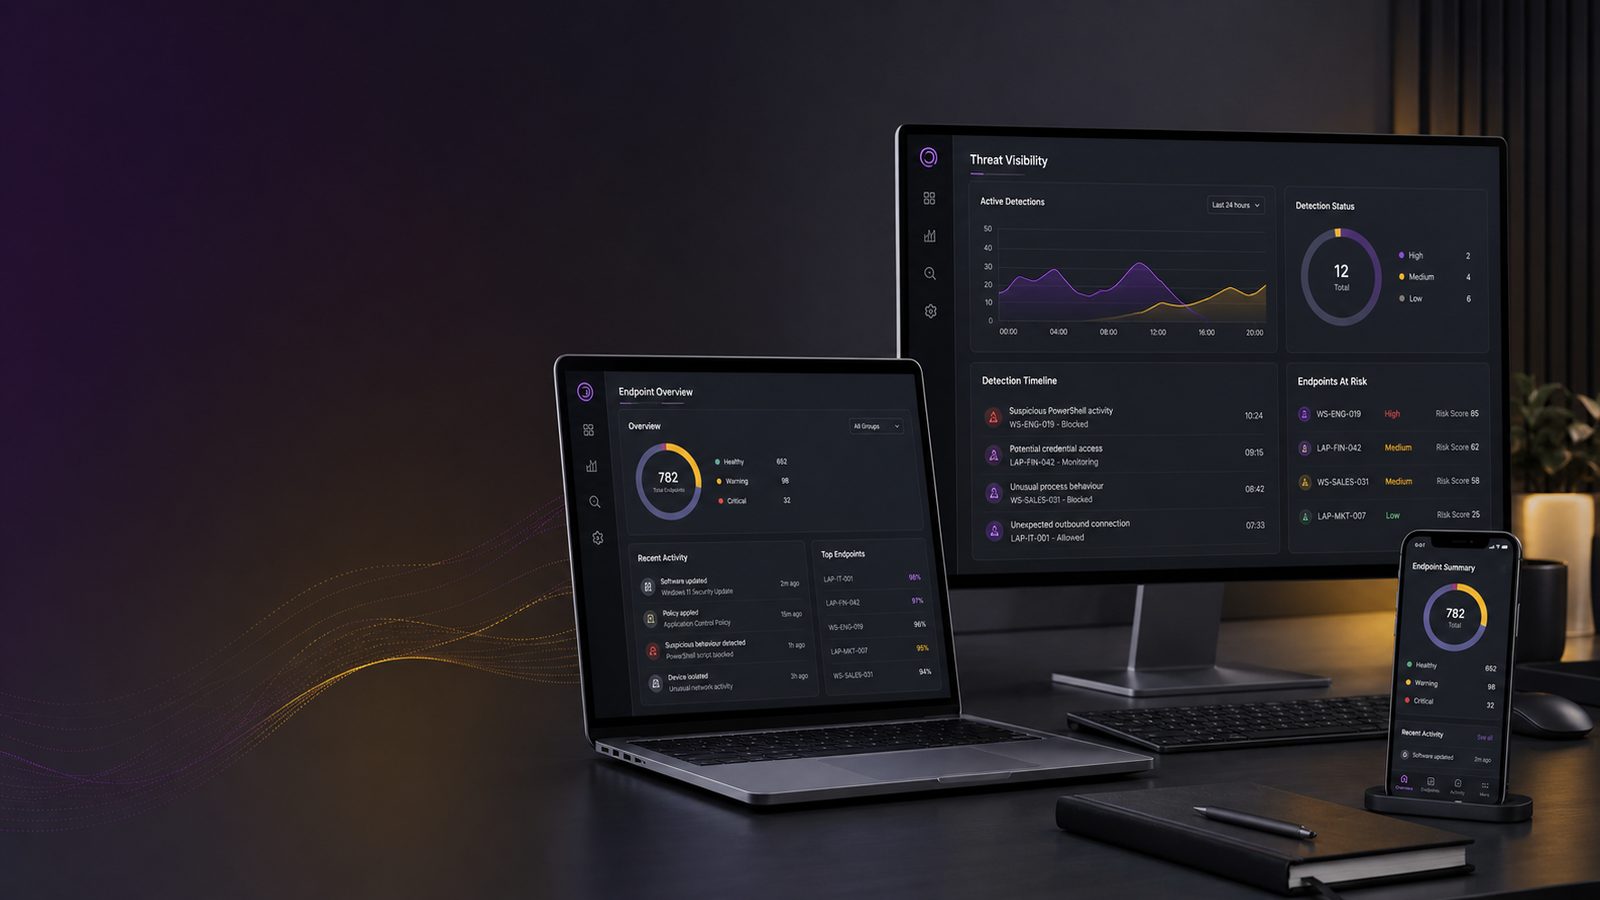
Why endpoint detection matters for organisations
Why endpoint detection matters for organisations For many UK SMEs, the biggest cyber risk is not a[…]