
Clear Path Security
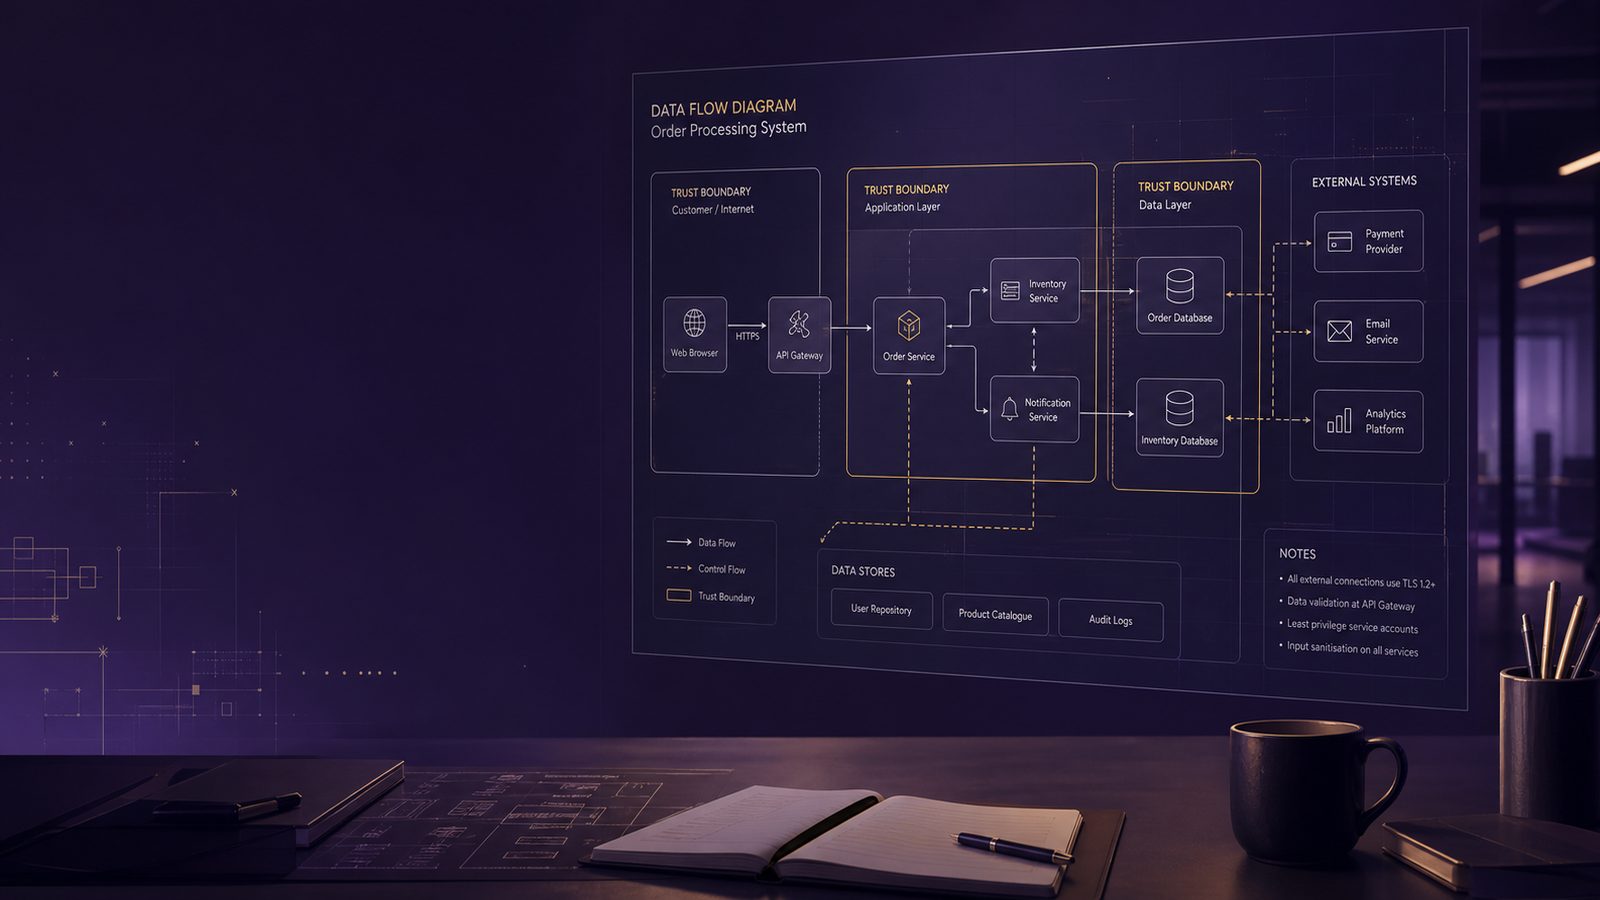
Applying data-flow diagrams to security threat modelling
Applying data-flow diagrams to security threat modelling Data-flow diagrams, often shortened to DFDs, are one of the[…]
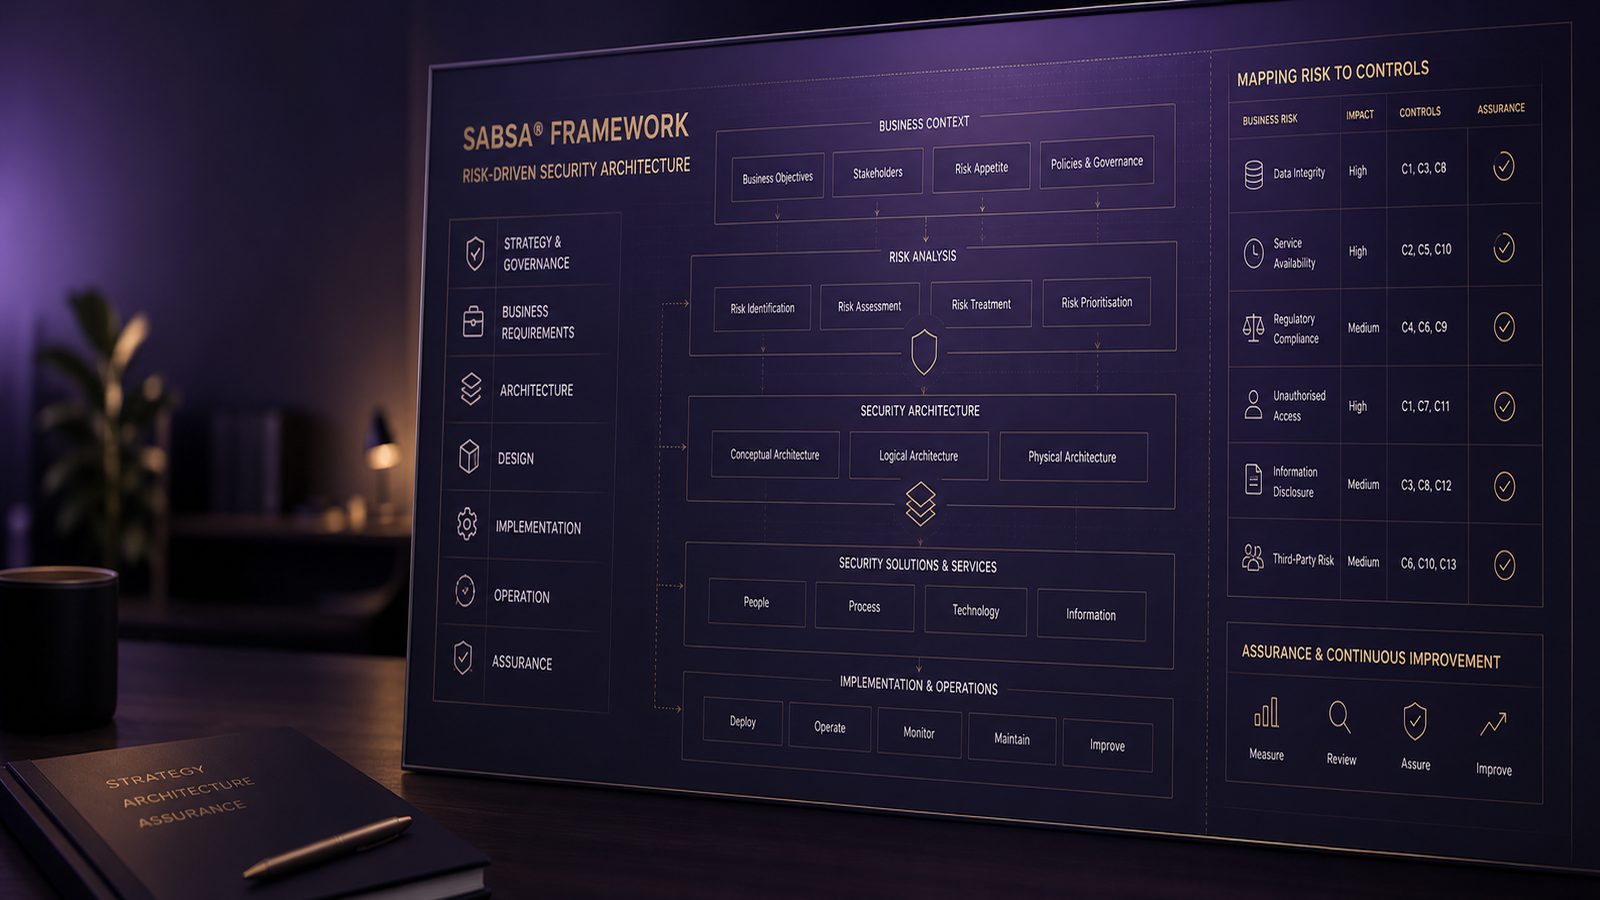
SABSA framework for risk-driven security architecture: a practical guide for UK SMEs
What SABSA is and where it fits in security architecture SABSA is a framework for building security[…]
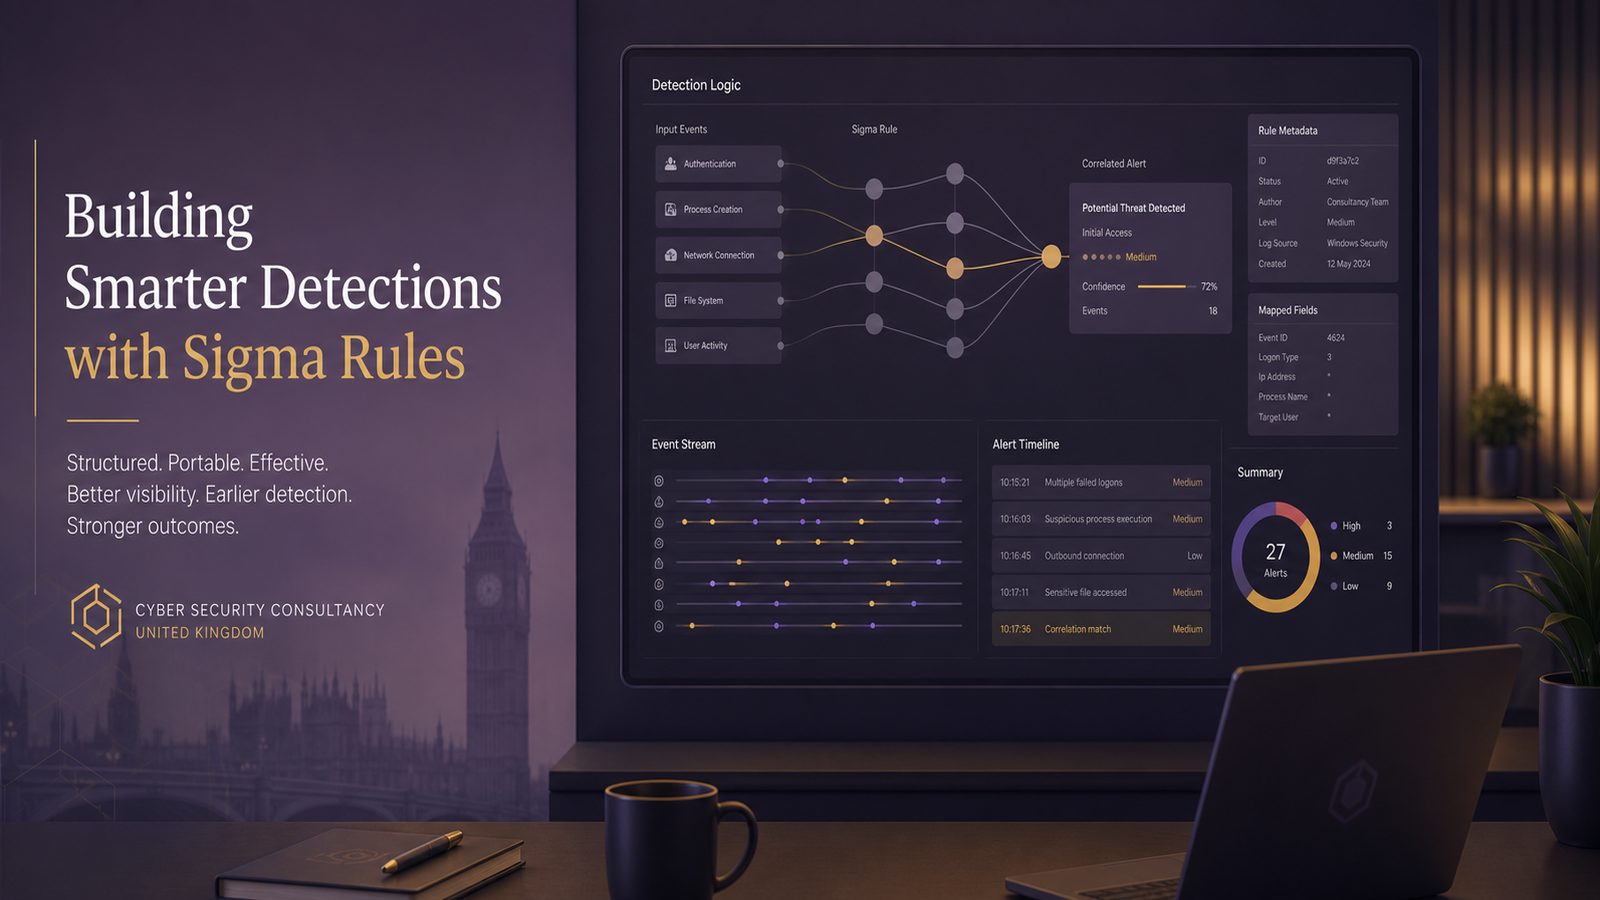
Building SIEM detections using Sigma rules
Building SIEM detections using Sigma rules For many UK SMEs, the challenge is not collecting logs. It[…]
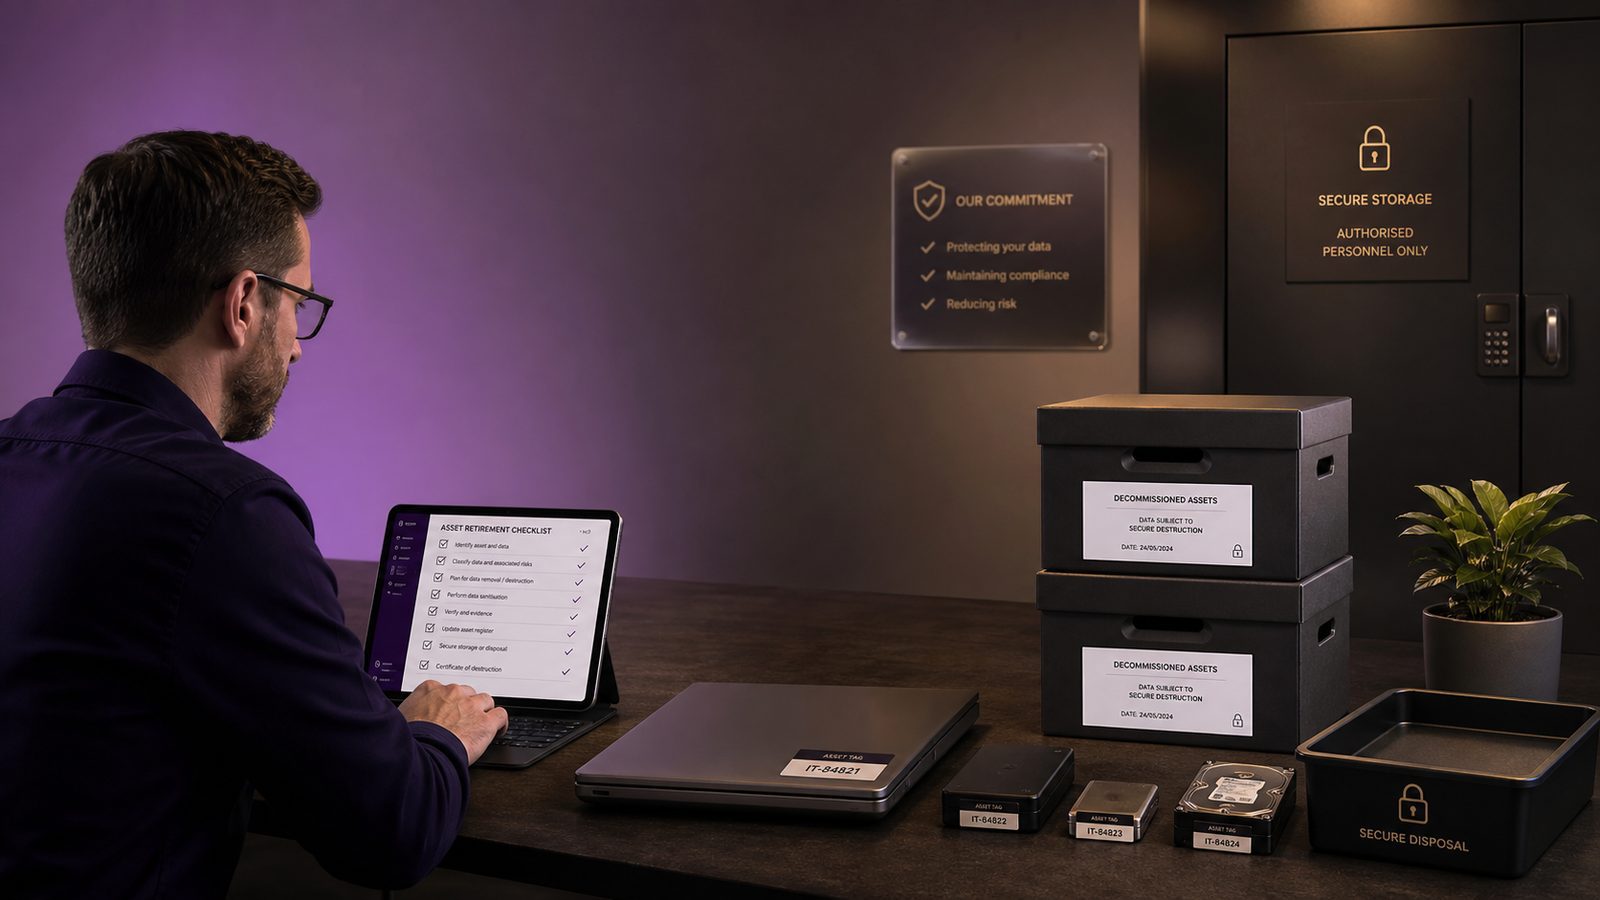
Secure decommissioning and data destruction practices for UK SMEs
Secure decommissioning and data destruction practices for UK SMEs Decommissioning is often treated as an IT tidy-up[…]
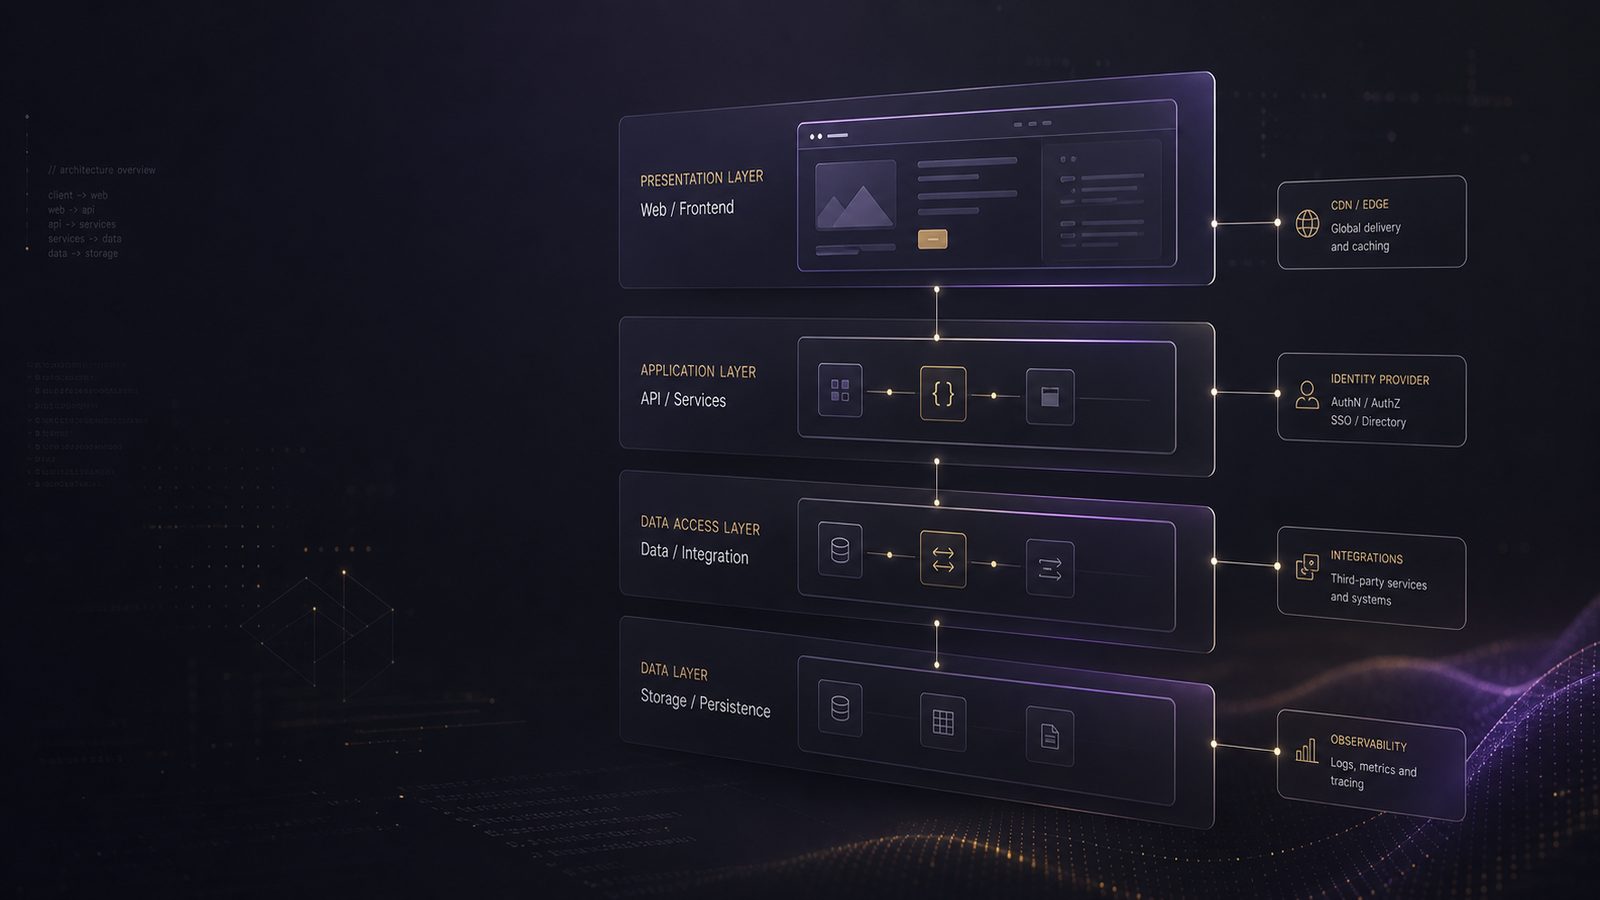
Implementing OWASP ASVS controls across application tiers
Implementing OWASP ASVS controls across application tiers OWASP ASVS (Application Security Verification Standard) is a list of[…]
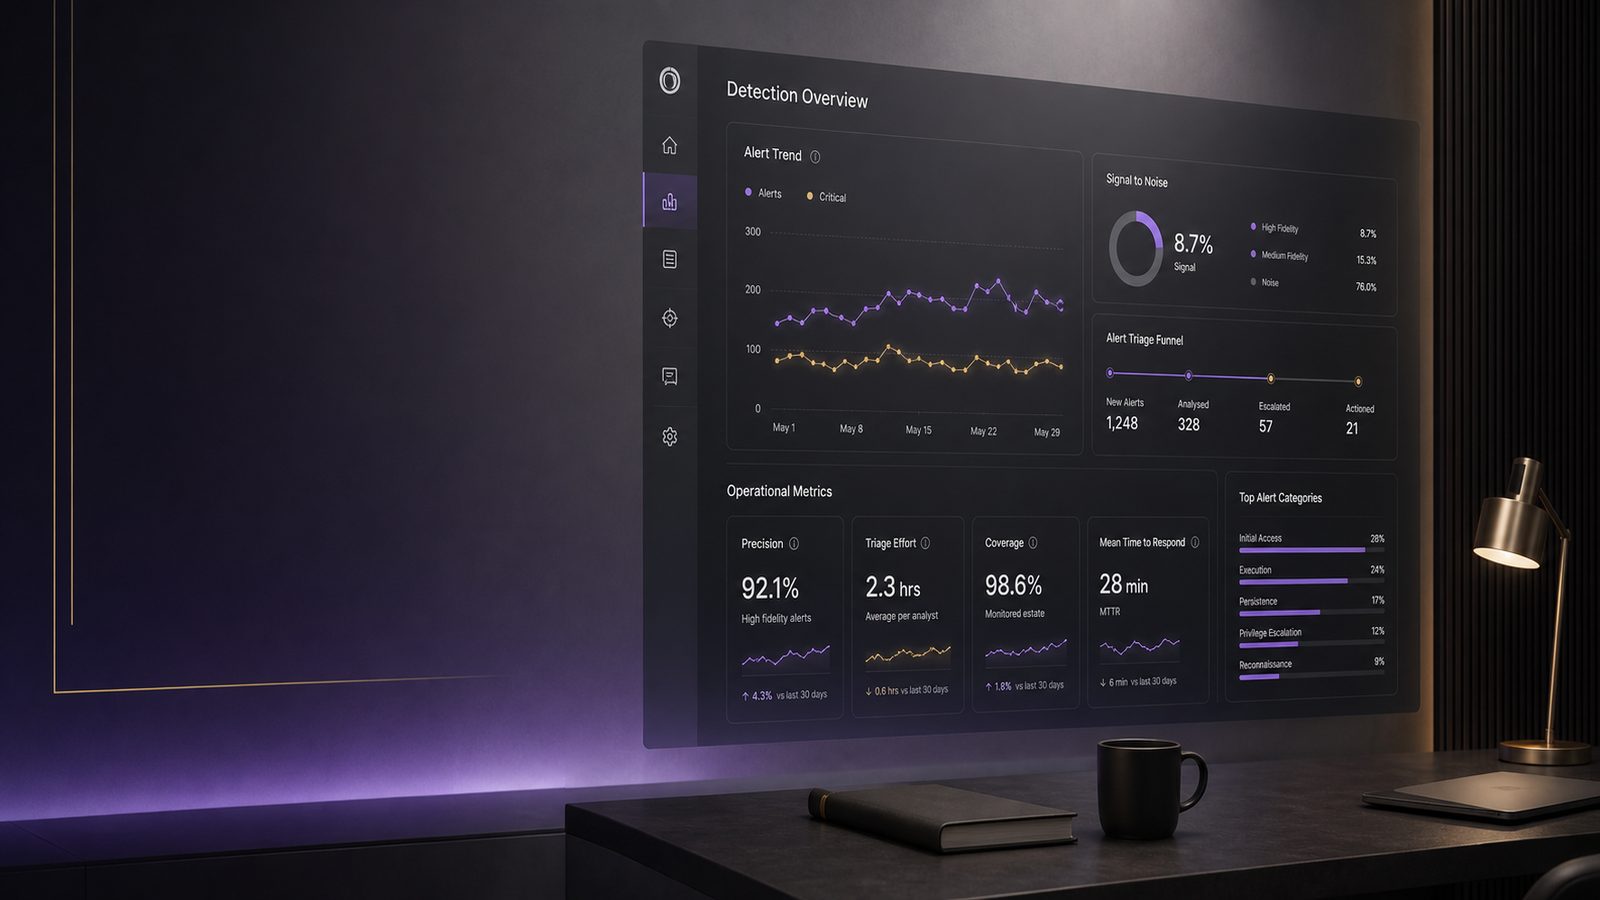
Measuring detection quality and false positives for technical teams
Measuring detection quality and false positives for technical teams Security teams often talk about alert volume, but[…]
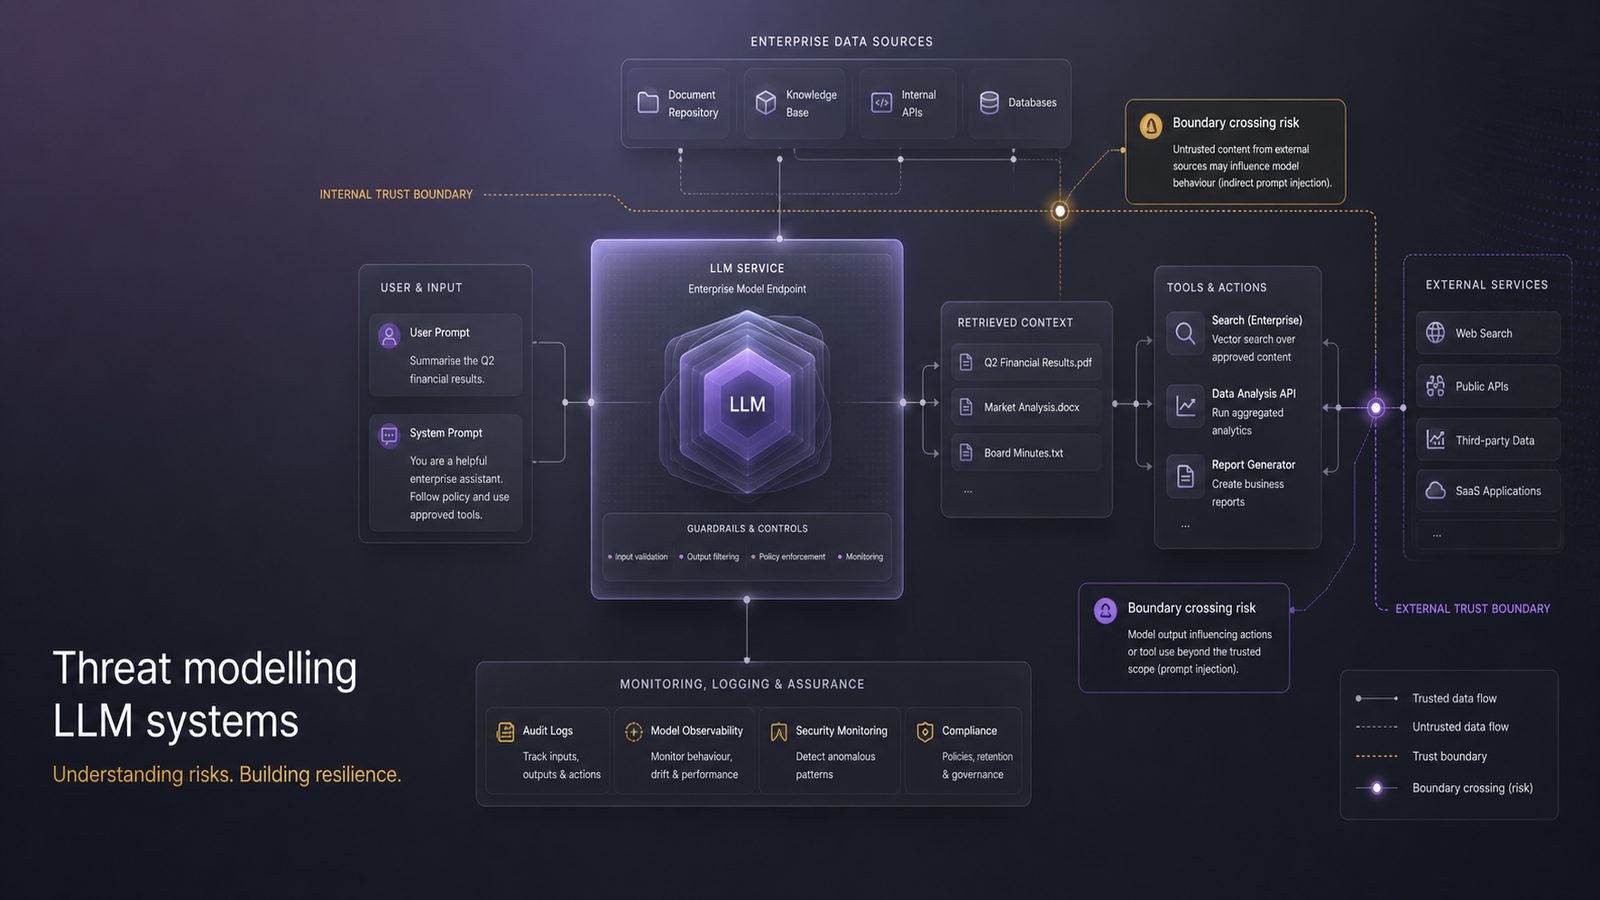
Threat modelling LLM systems for prompt injection
Threat modelling LLM systems for prompt injection Large language models have moved quickly from experimentation into real[…]
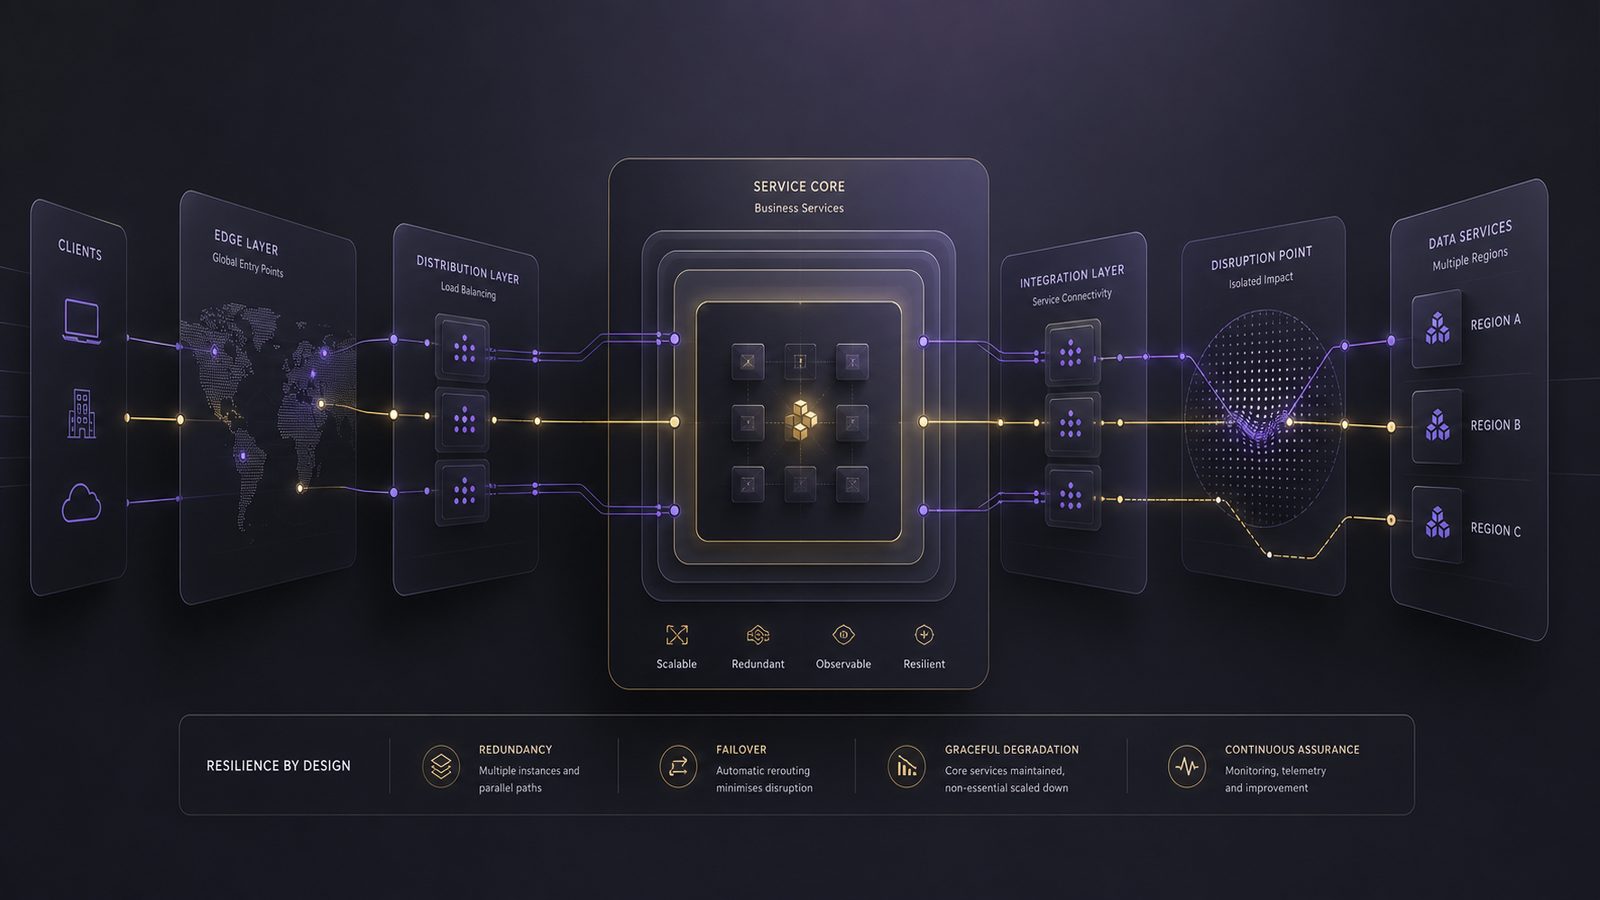
Ensuring systems are resilient to both attack and failure
Ensuring systems are resilient to both attack and failure For many UK SMEs, resilience is still treated[…]
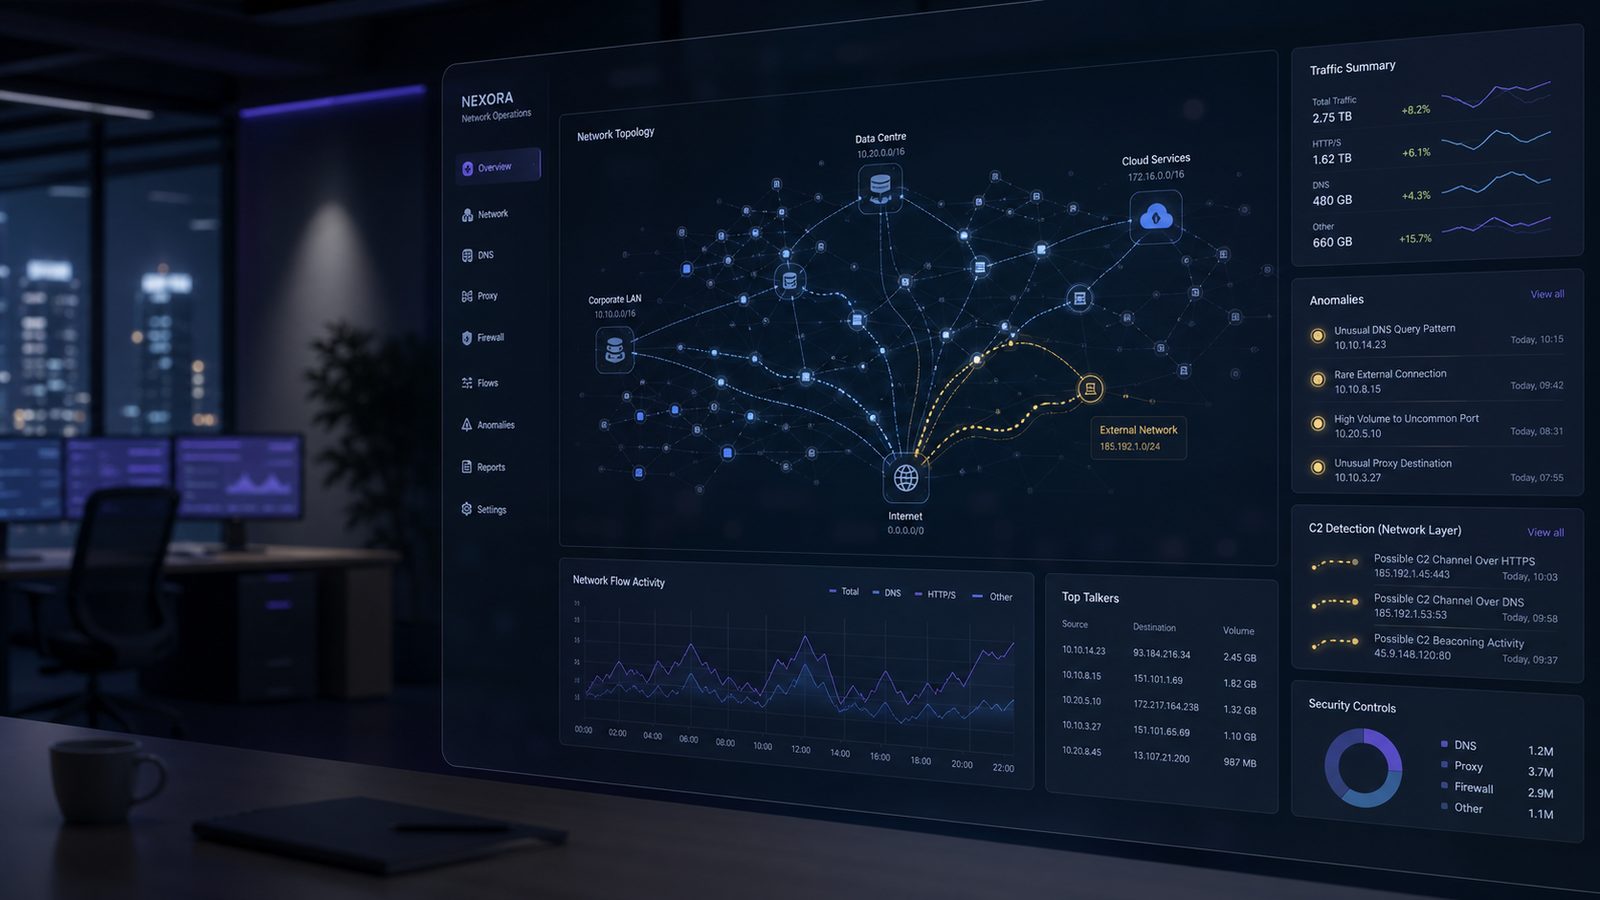
Detecting command-and-control traffic at the network layer: a practical guide for UK SMEs
Detecting command-and-control traffic at the network layer: a practical guide for UK SMEs Command-and-control traffic, often shortened[…]
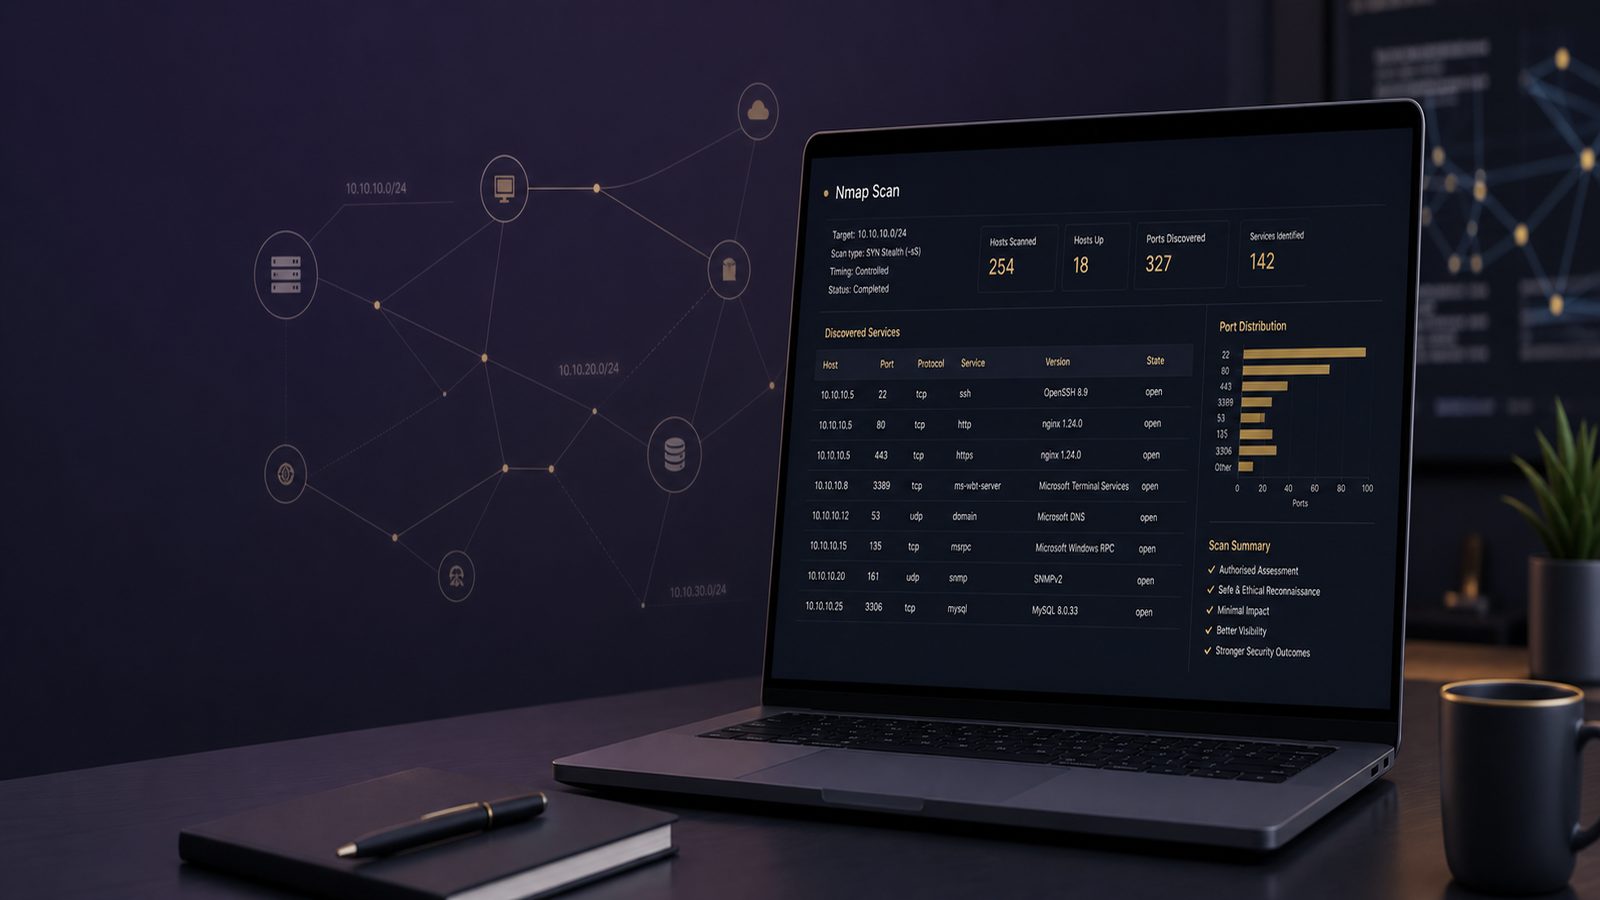
Network reconnaissance using Nmap safely and ethically
Network reconnaissance using Nmap safely and ethically Network reconnaissance is one of the most useful parts of[…]