
Clear Path Security
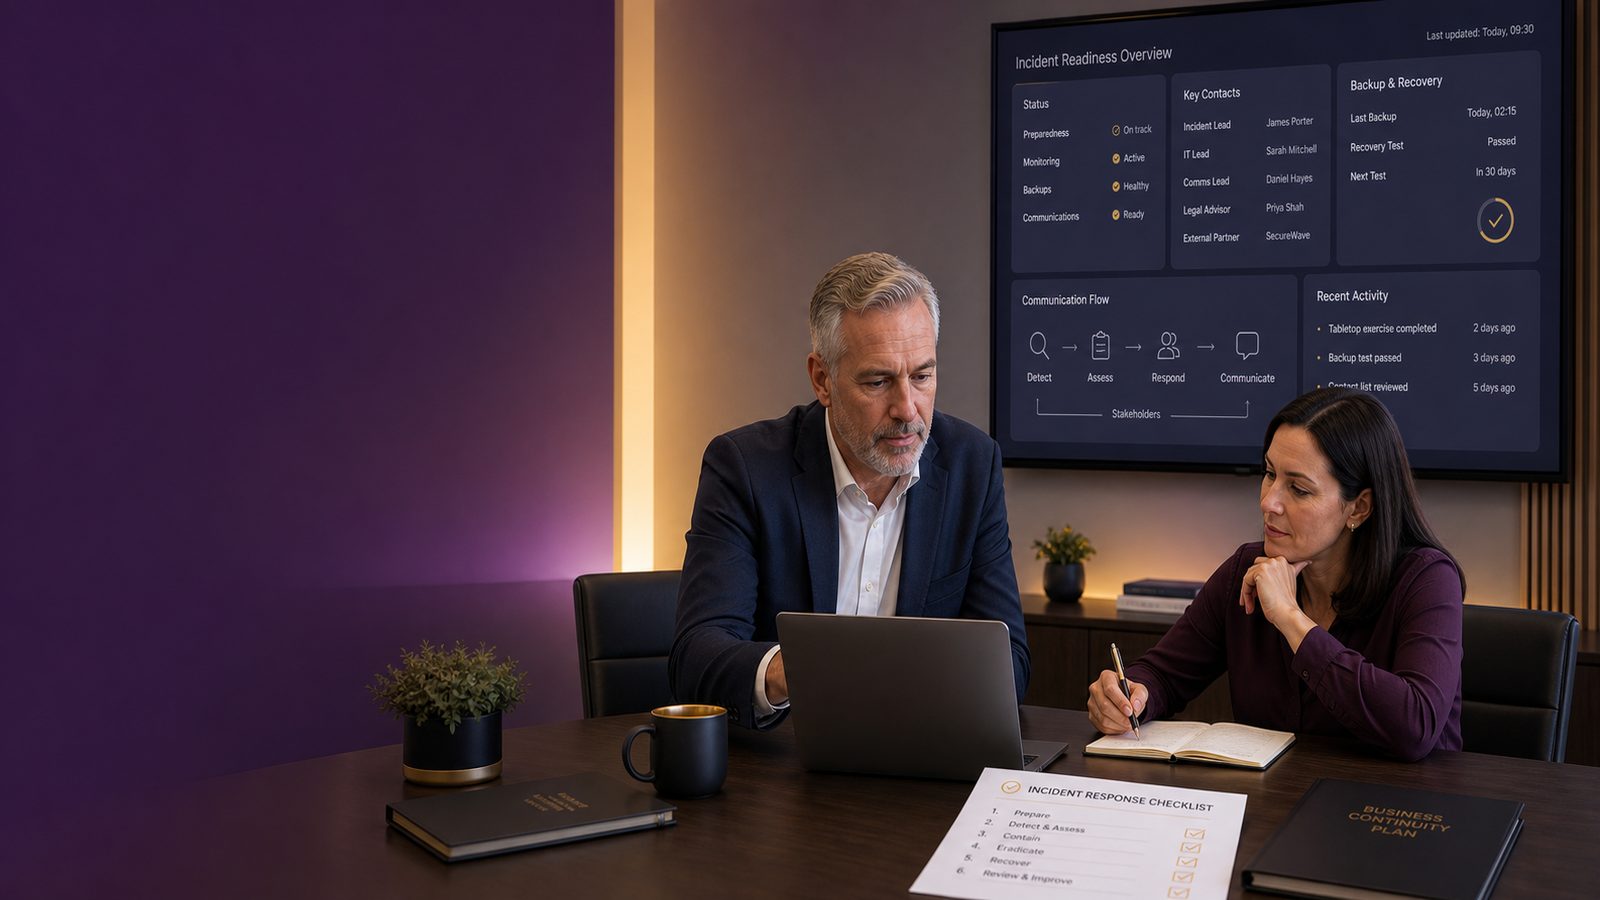
Preparing your organisation for security incidents
Preparing your organisation for security incidents When a security incident happens, the biggest cost is often not[…]
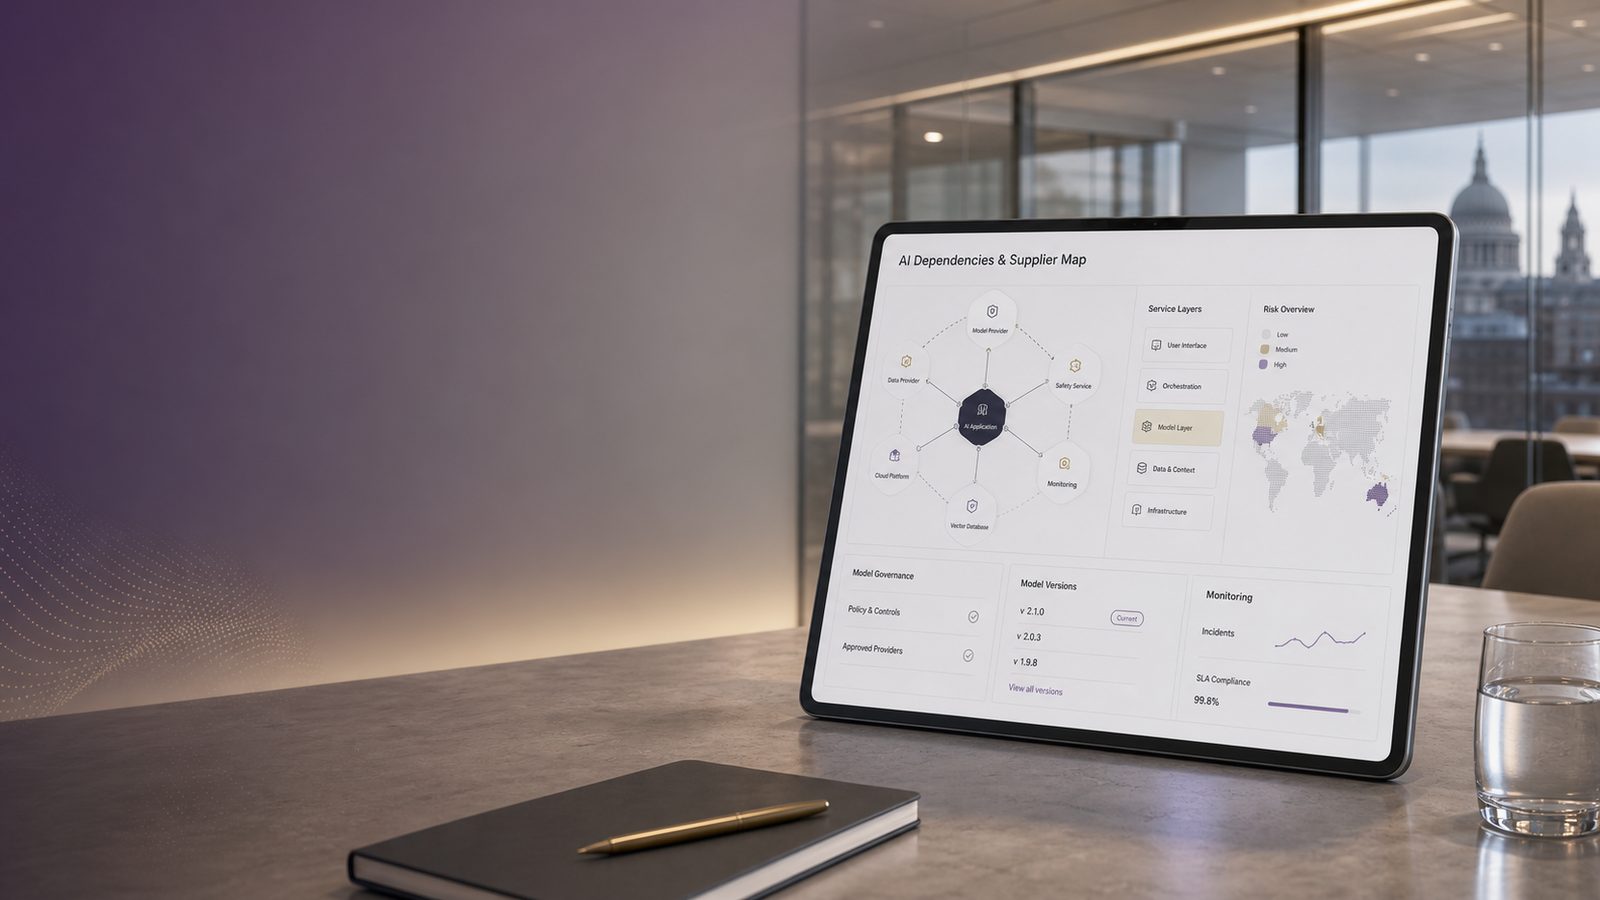
Managing third-party model risk and AI dependencies
Managing third-party model risk and AI dependencies For many UK SMEs, the fastest route to using AI[…]
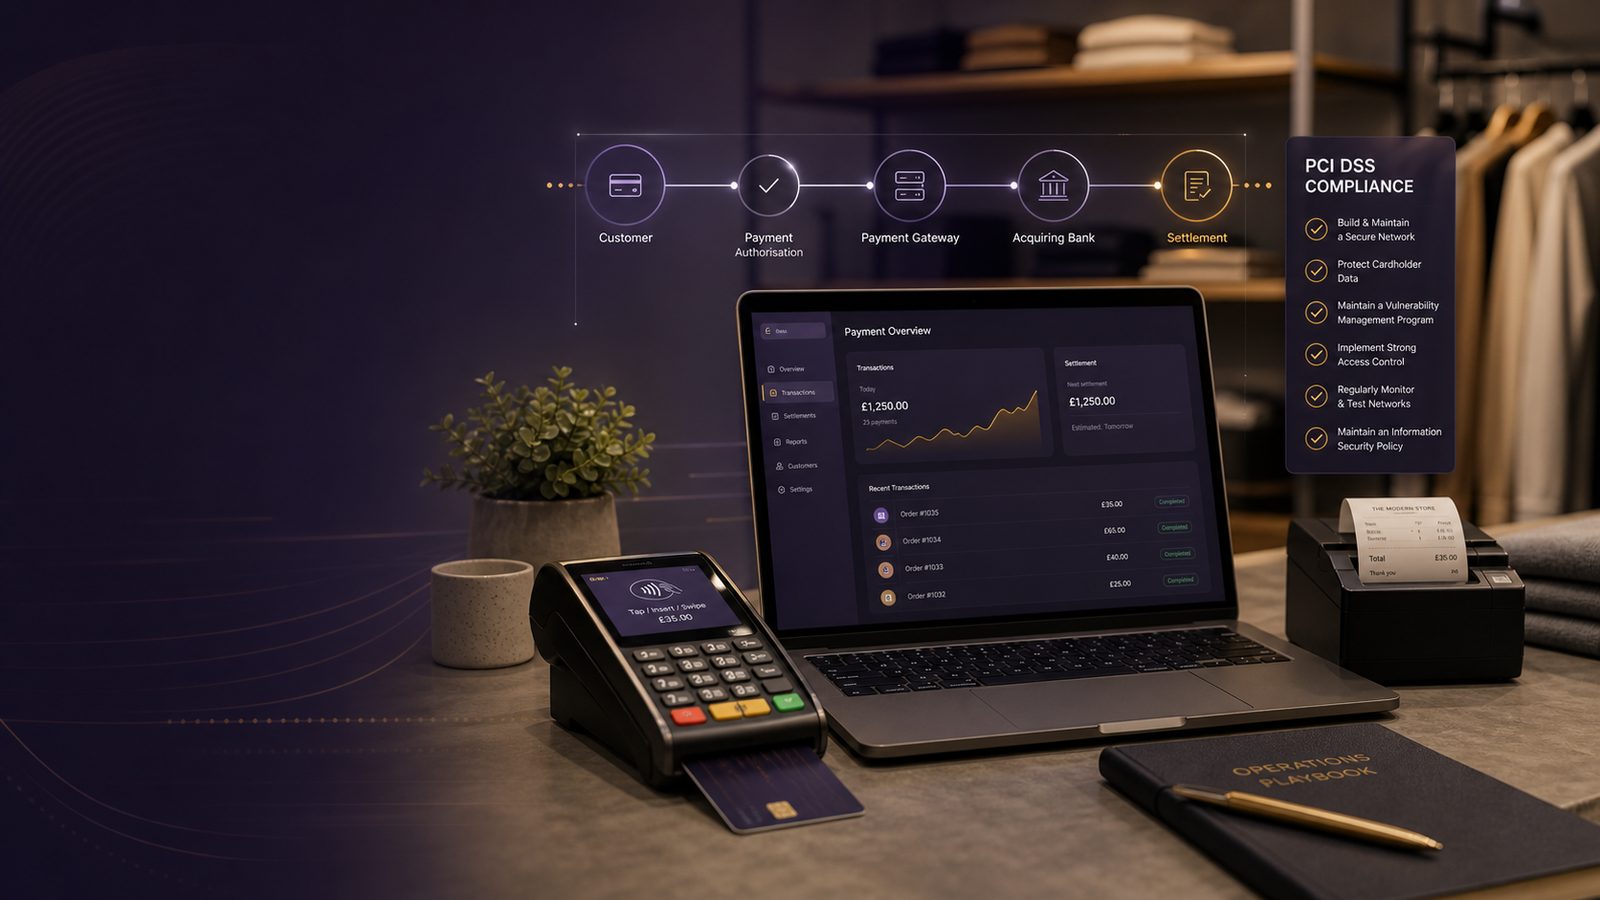
PCI DSS explained for small merchants: a practical guide for UK SMEs
PCI DSS explained for small merchants: a practical guide for UK SMEs If your business takes card[…]
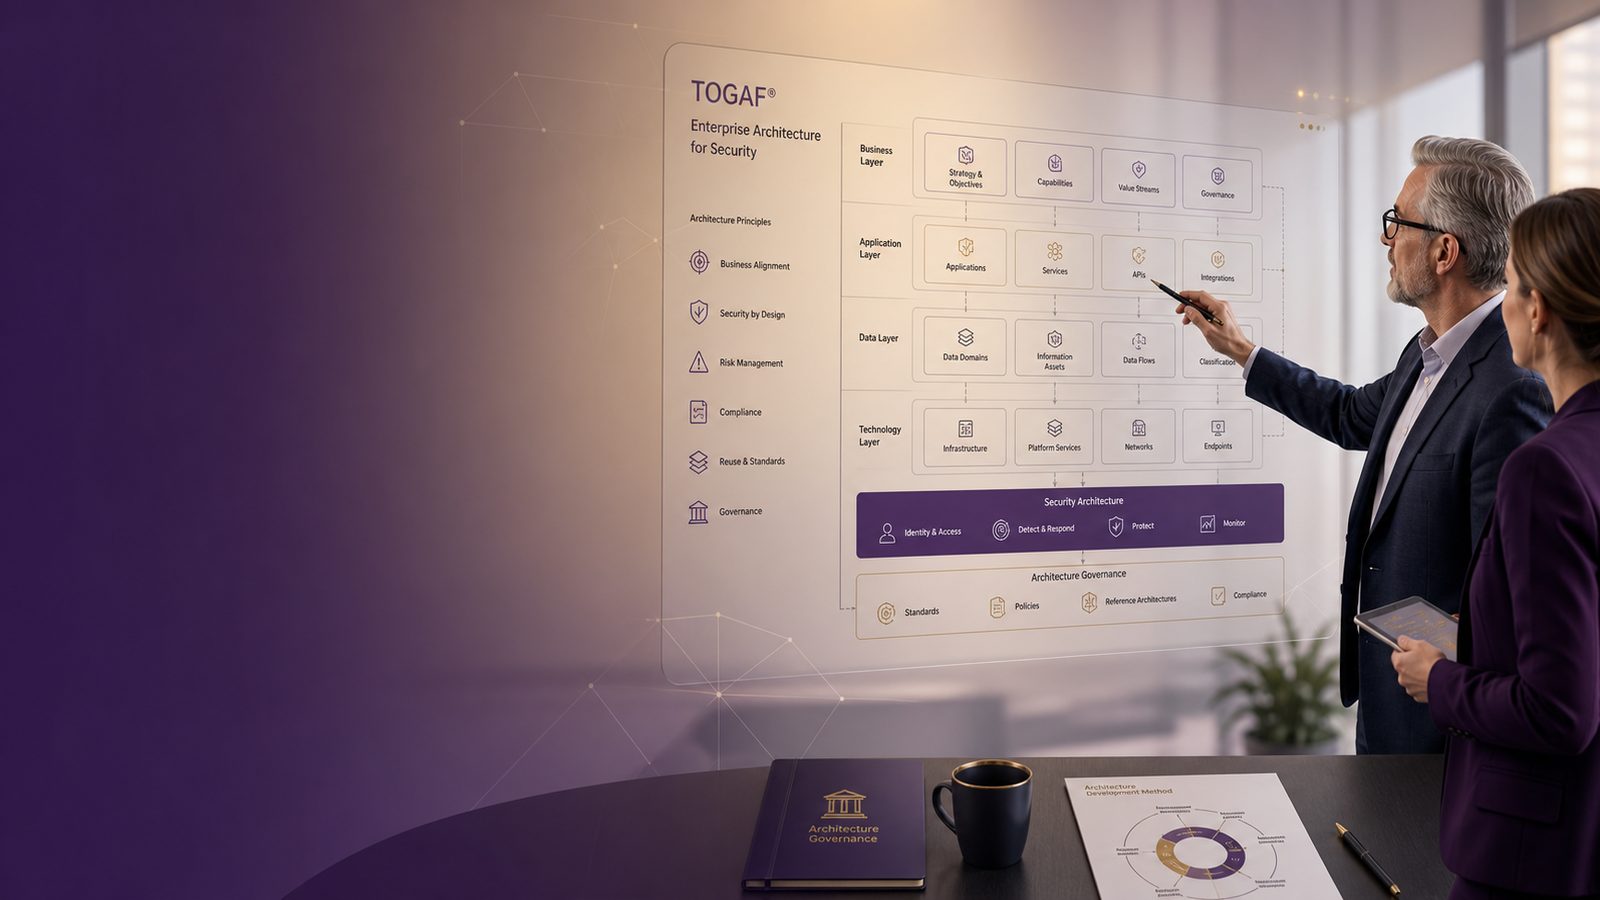
Applying TOGAF for security architecture design
Why TOGAF is useful for security architecture TOGAF’s Architecture Development Method (ADM) is a cycle of phases[…]
Designing Zero Trust architectures with Entra ID for UK SMEs
Designing Zero Trust architectures with Entra ID for UK SMEs Zero Trust is often described as a[…]
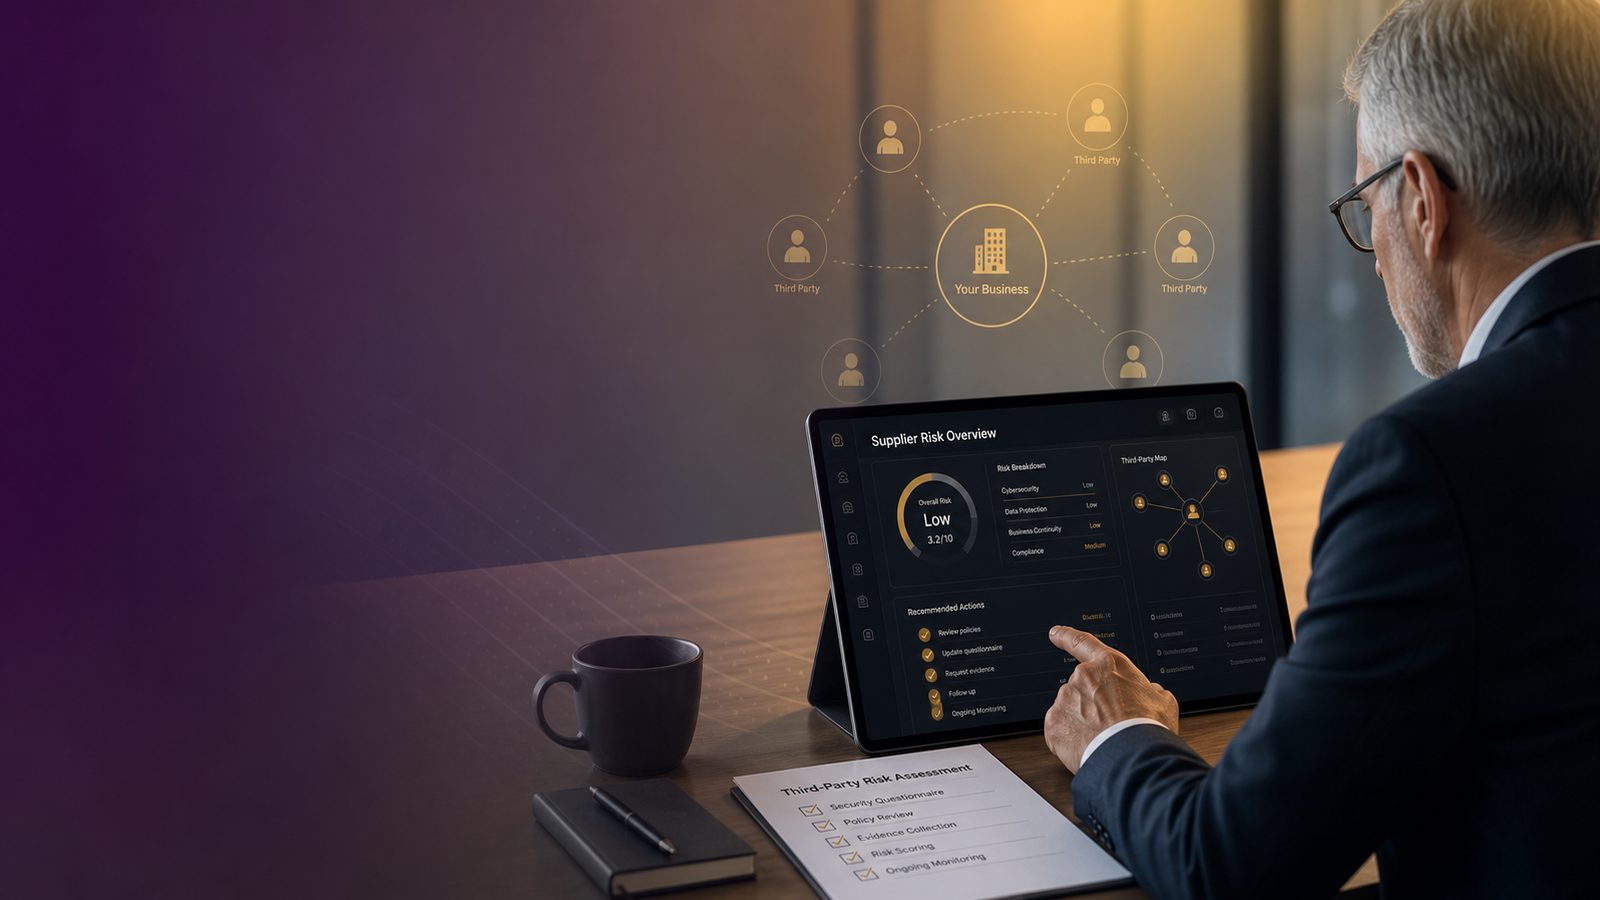
Third-party cyber risk assessments for SMEs: a practical guide for UK businesses
Third-party cyber risk assessments for SMEs: a practical guide for UK businesses For many small and medium-sized[…]
Microsegmentation strategies to prevent lateral movement in modern environments
Microsegmentation strategies to prevent lateral movement in modern environments Microsegmentation is one of the most effective ways[…]
GDPR principles explained for SMEs
GDPR principles explained for SMEs If you run a small business, the GDPR can feel like a[…]
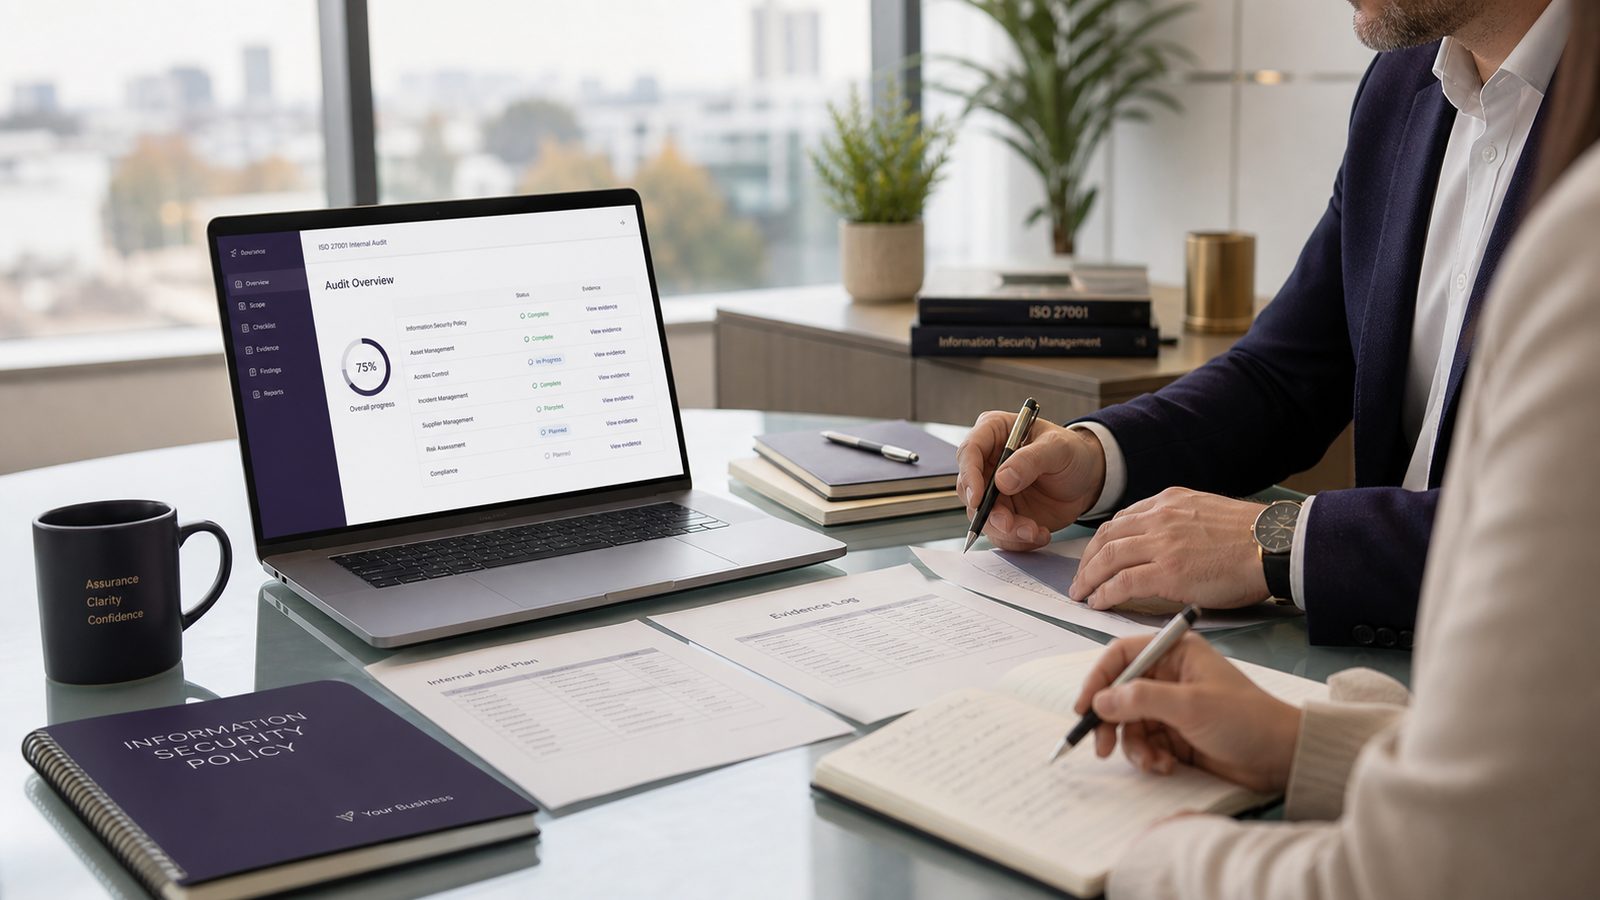
Internal audits under ISO 27001: what SMEs should test
Internal audits under ISO 27001: what SMEs should test For many small businesses, an internal audit can[…]
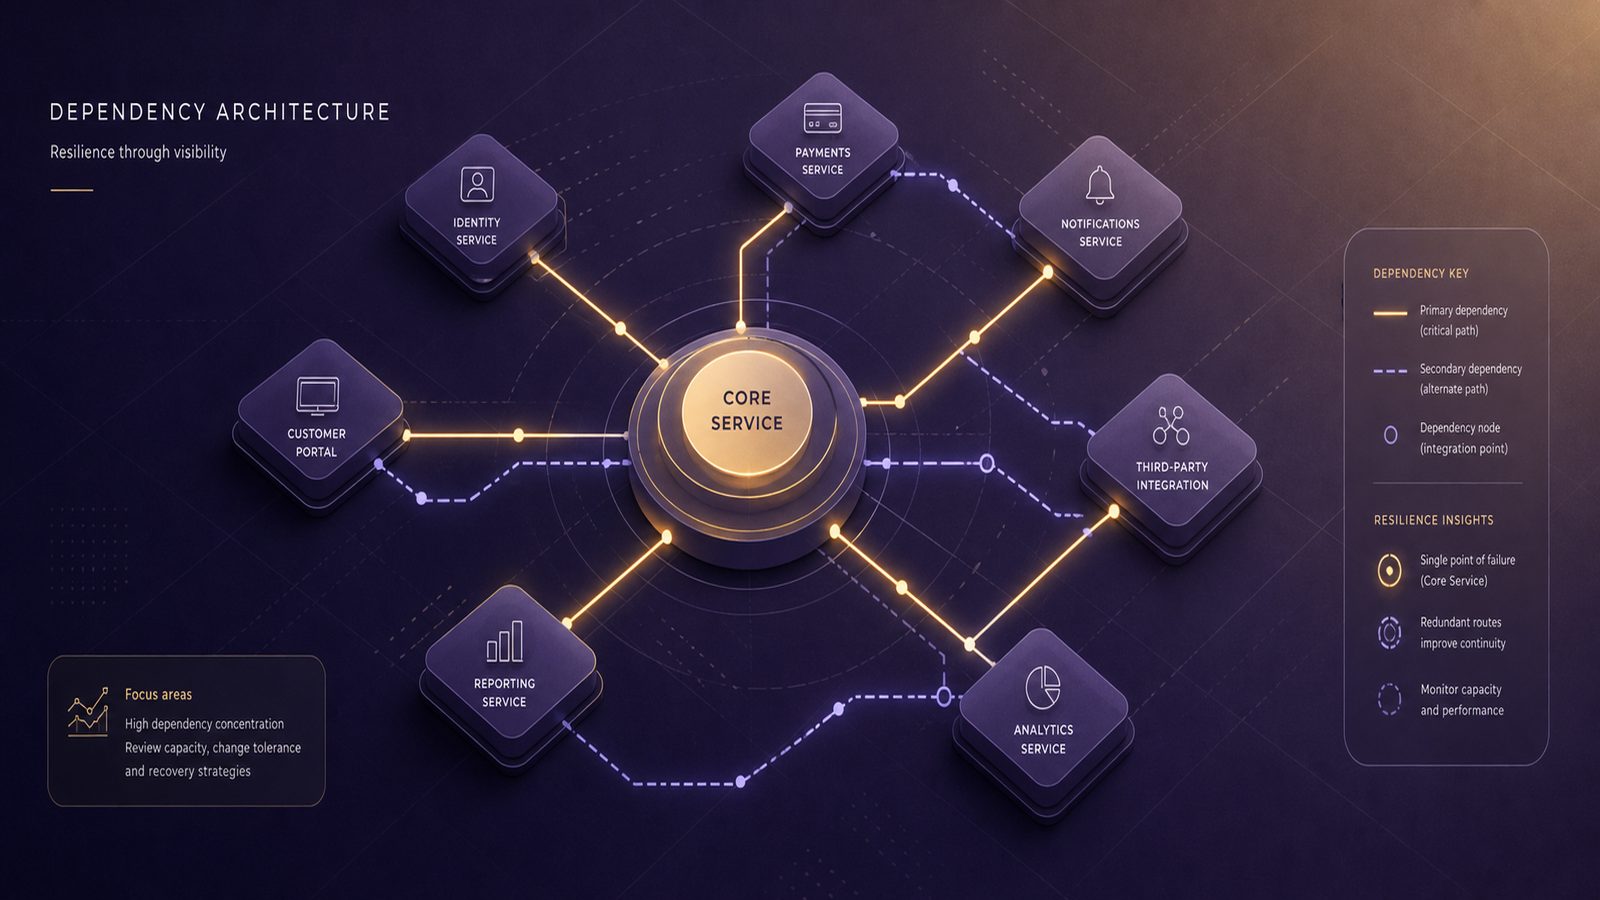
Identifying bottlenecks and single points of failure in security architecture
Identifying bottlenecks and single points of failure in security architecture When teams talk about security architecture, the[…]