
Clear Path Security
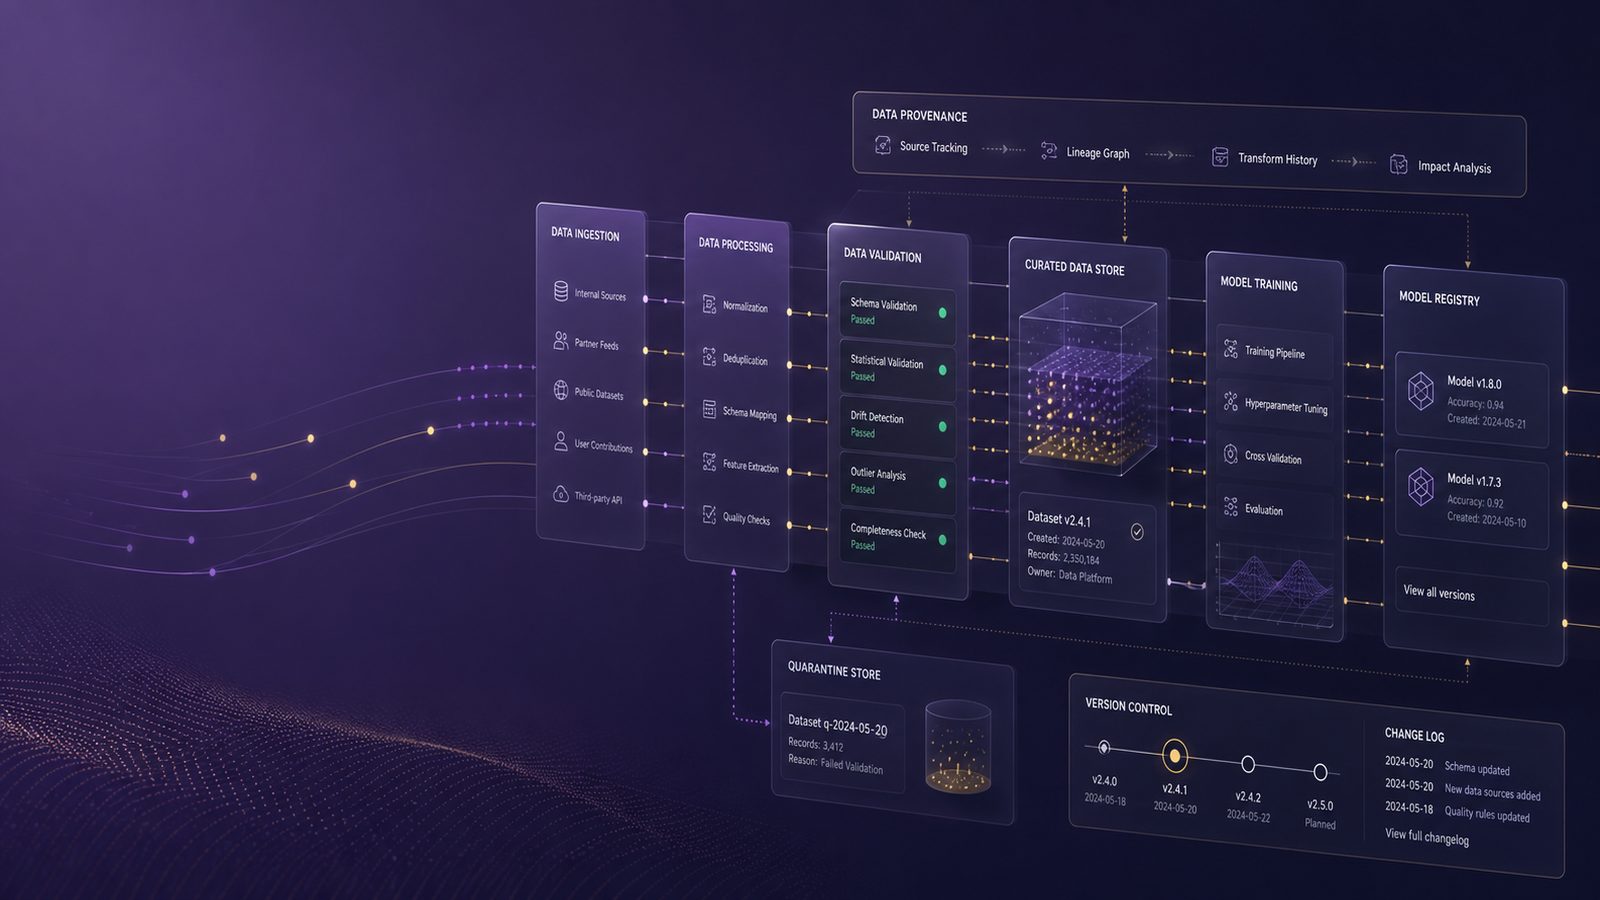
Securing AI pipelines against data poisoning: a practical guide for technical teams
Securing AI pipelines against data poisoning: a practical guide for technical teams Data poisoning is one of[…]
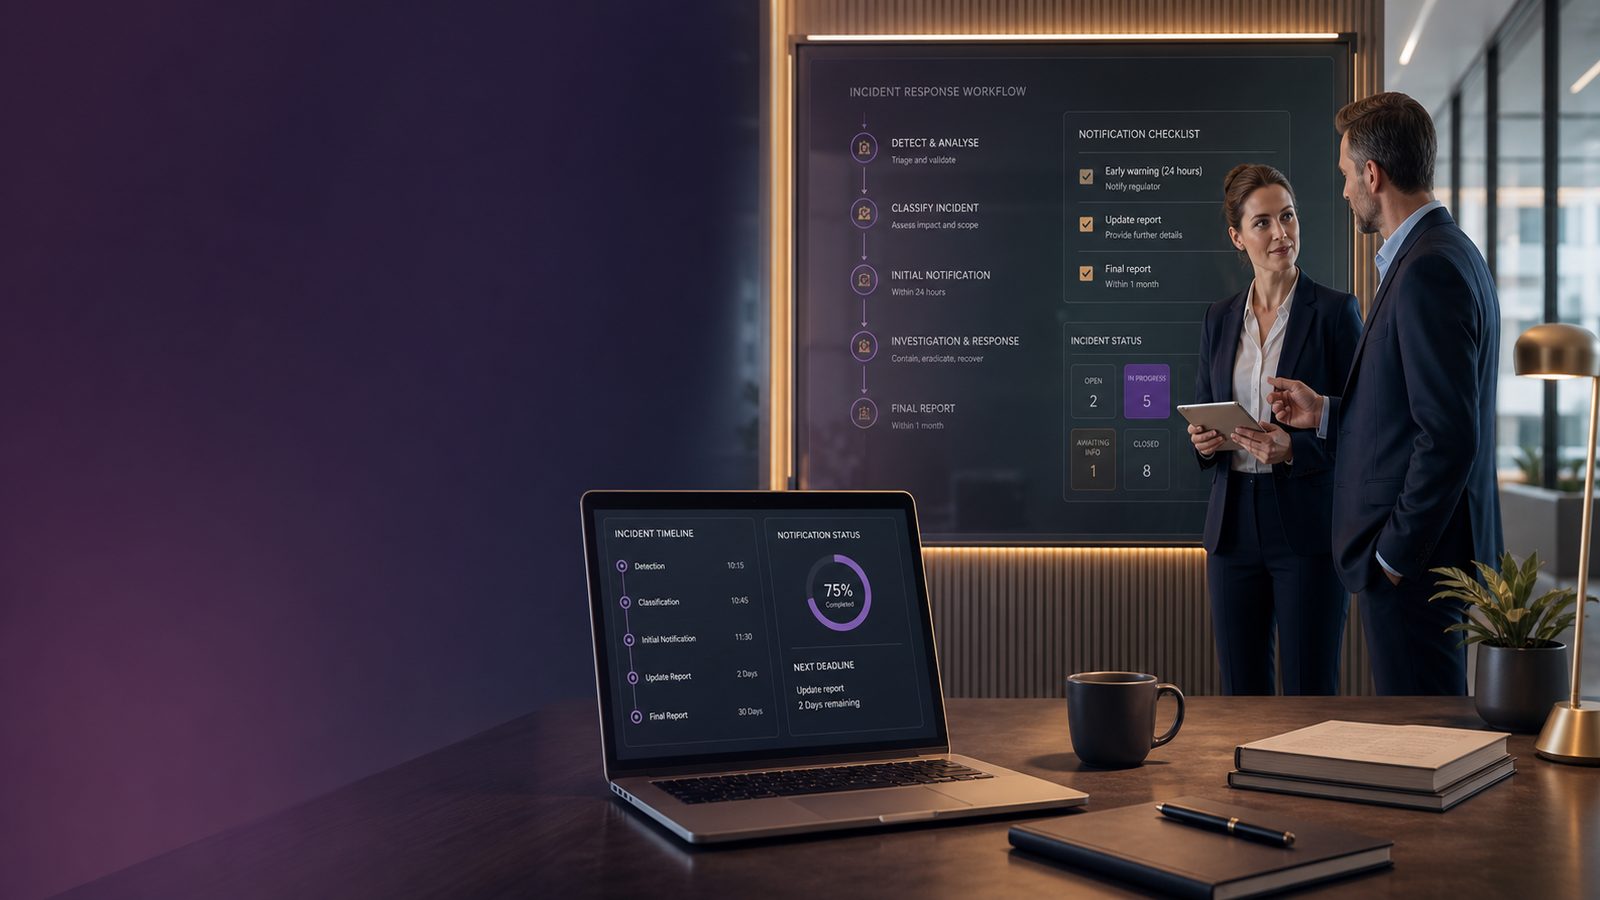
Incident reporting requirements under NIS2: a practical guide for UK SMEs
Incident reporting requirements under NIS2: a practical guide for UK SMEs If your business is in scope[…]
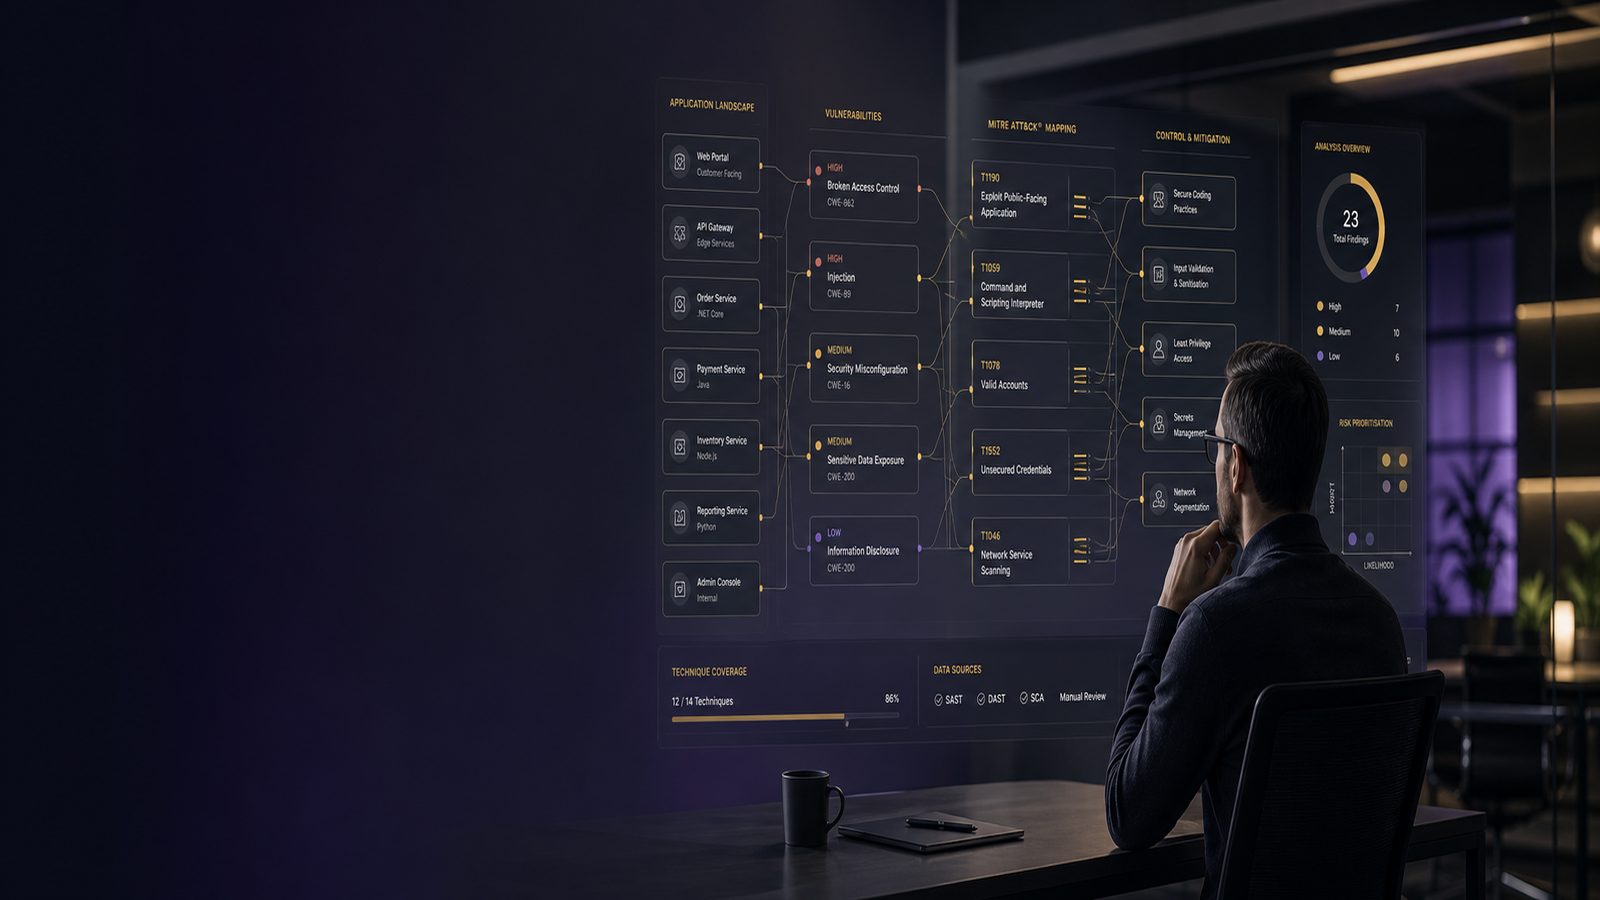
Mapping application vulnerabilities to MITRE ATT&CK
Mapping application vulnerabilities to MITRE ATT&CK For many UK SMEs, vulnerability management still starts and ends with[…]
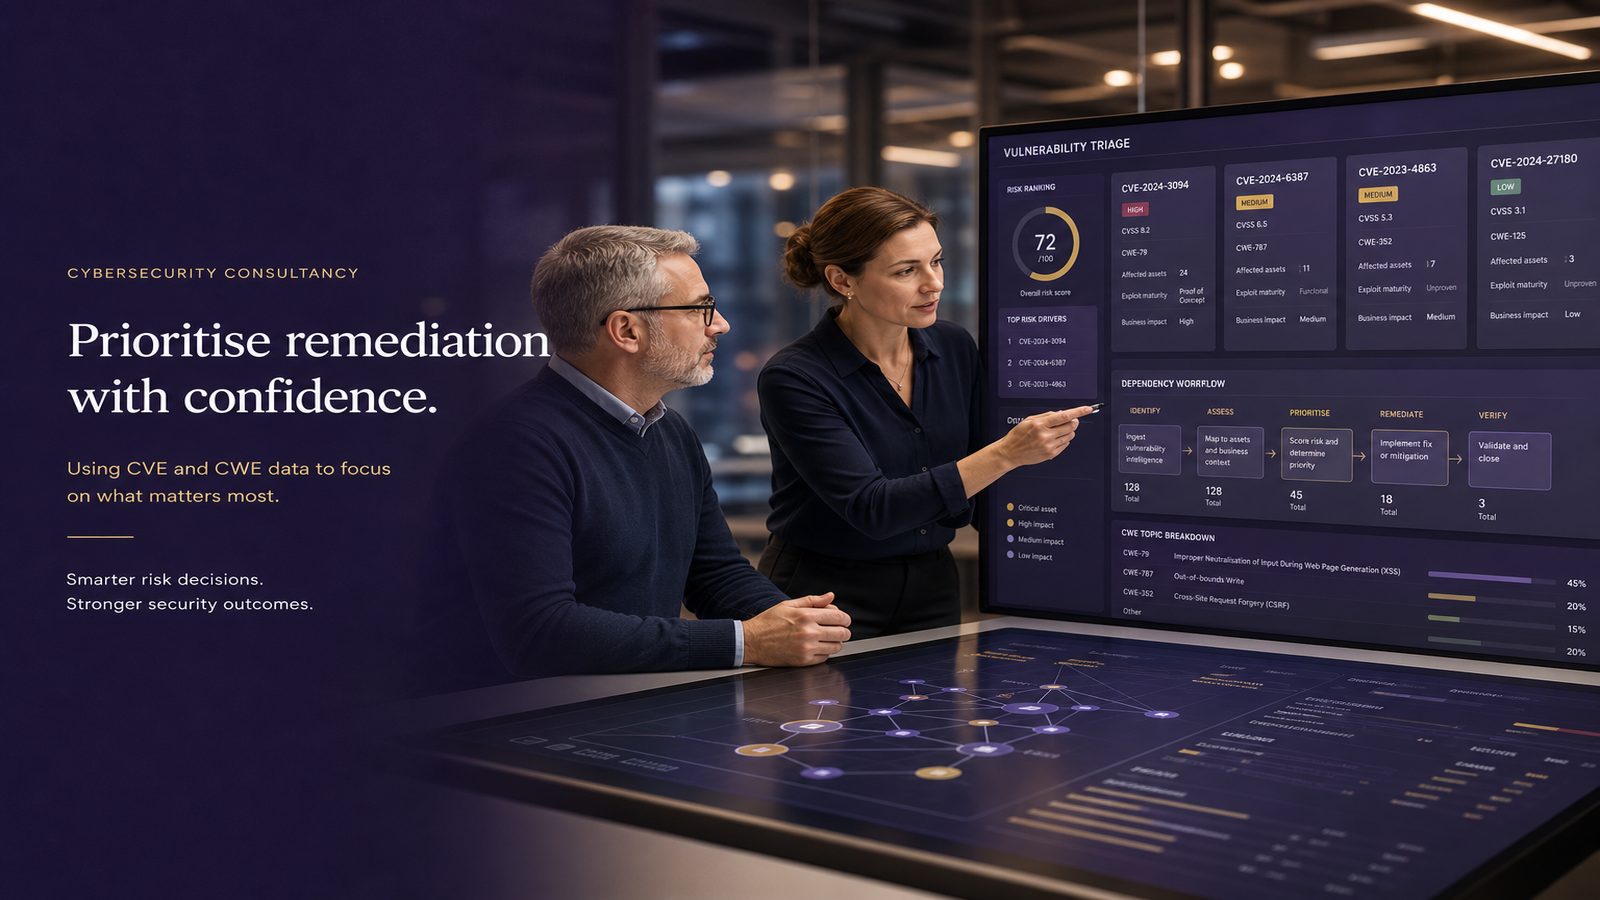
Using CVE and CWE data to prioritise remediation
Using CVE and CWE data to prioritise remediation For many UK SMEs, vulnerability management can become a[…]
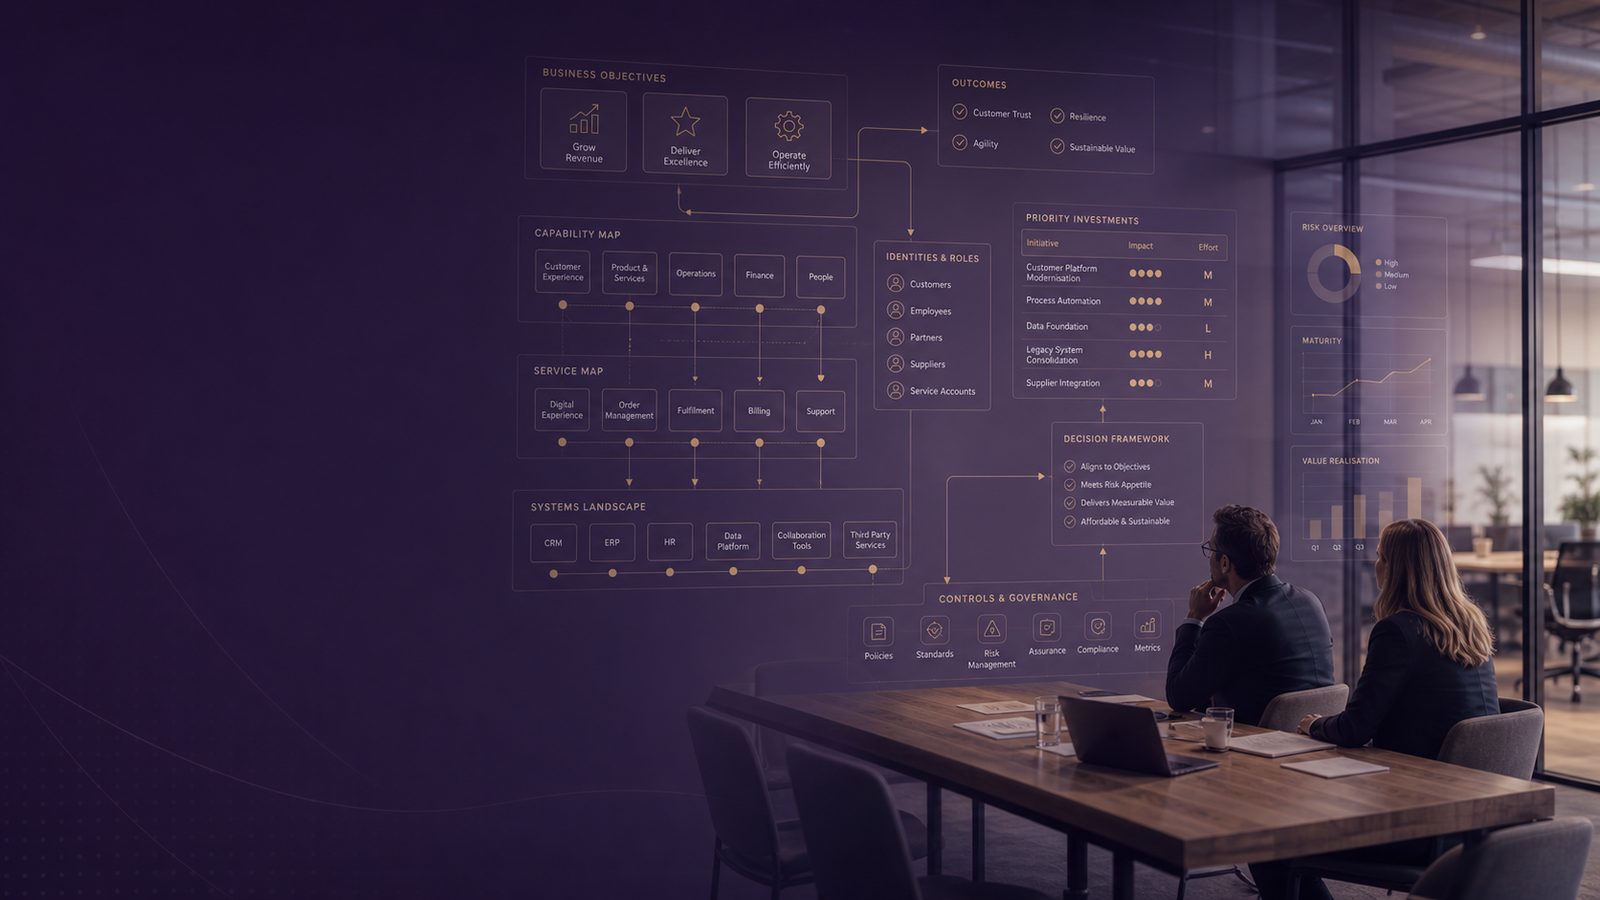
Aligning security architecture to business objectives for UK SMEs
Aligning security architecture to business objectives for UK SMEs For many UK SMEs, security architecture starts as[…]
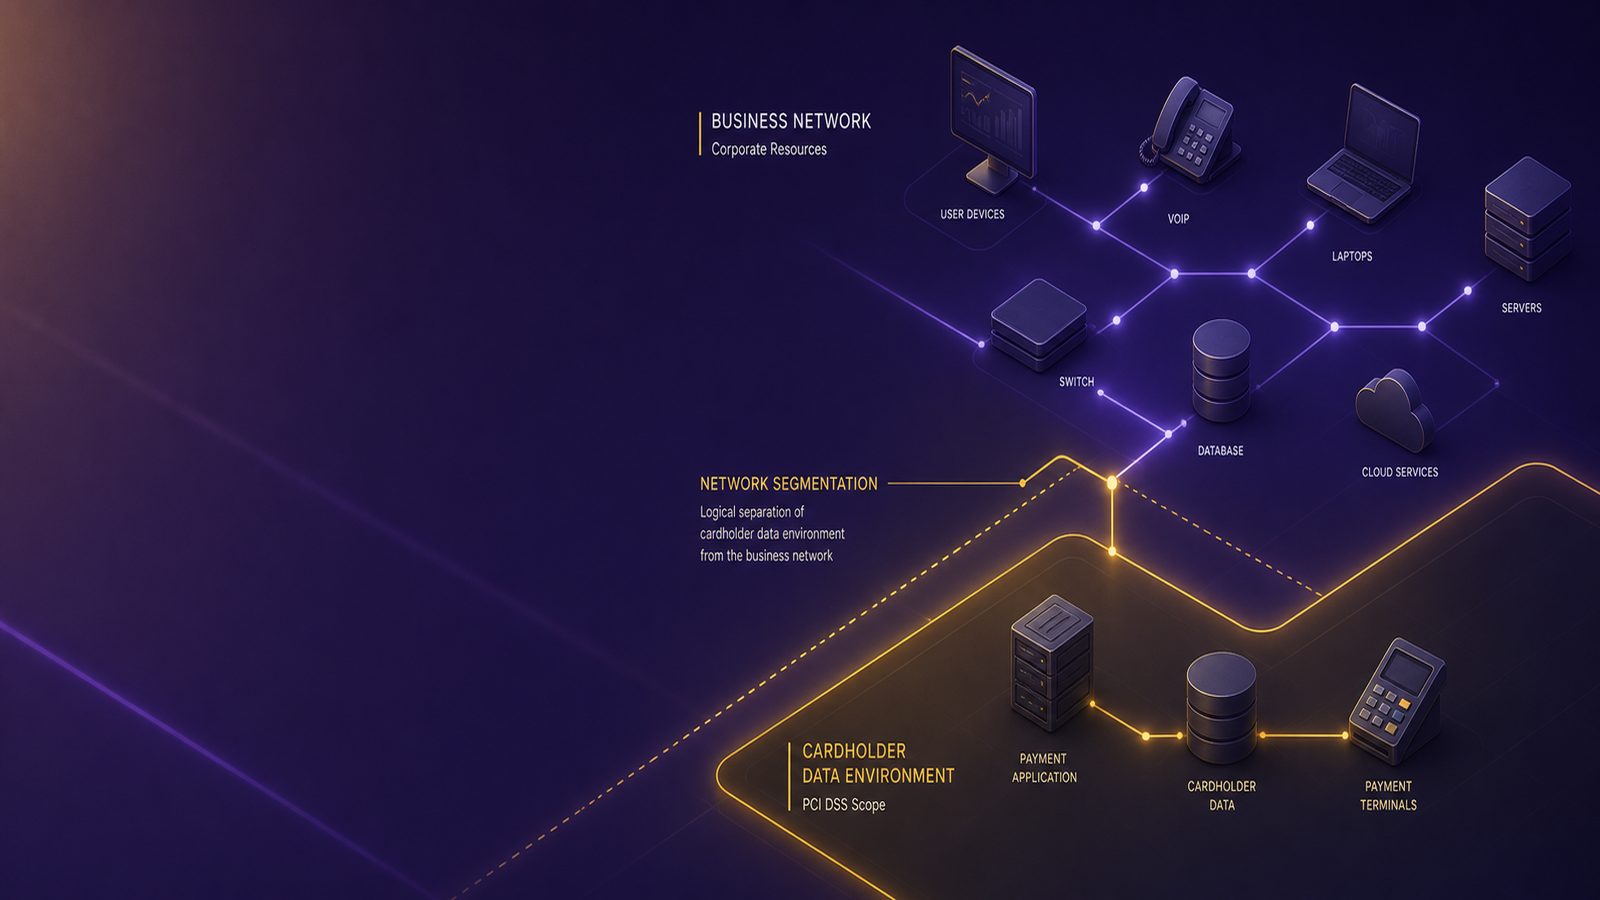
Implementing network segmentation for PCI DSS: a practical guide for UK SMEs
Implementing network segmentation for PCI DSS: a practical guide for UK SMEs For many UK SMEs, PCI[…]

Cyber Essentials explained for small businesses
Cyber Essentials explained for small businesses For many UK SMEs, Cyber Essentials is the first cyber security[…]
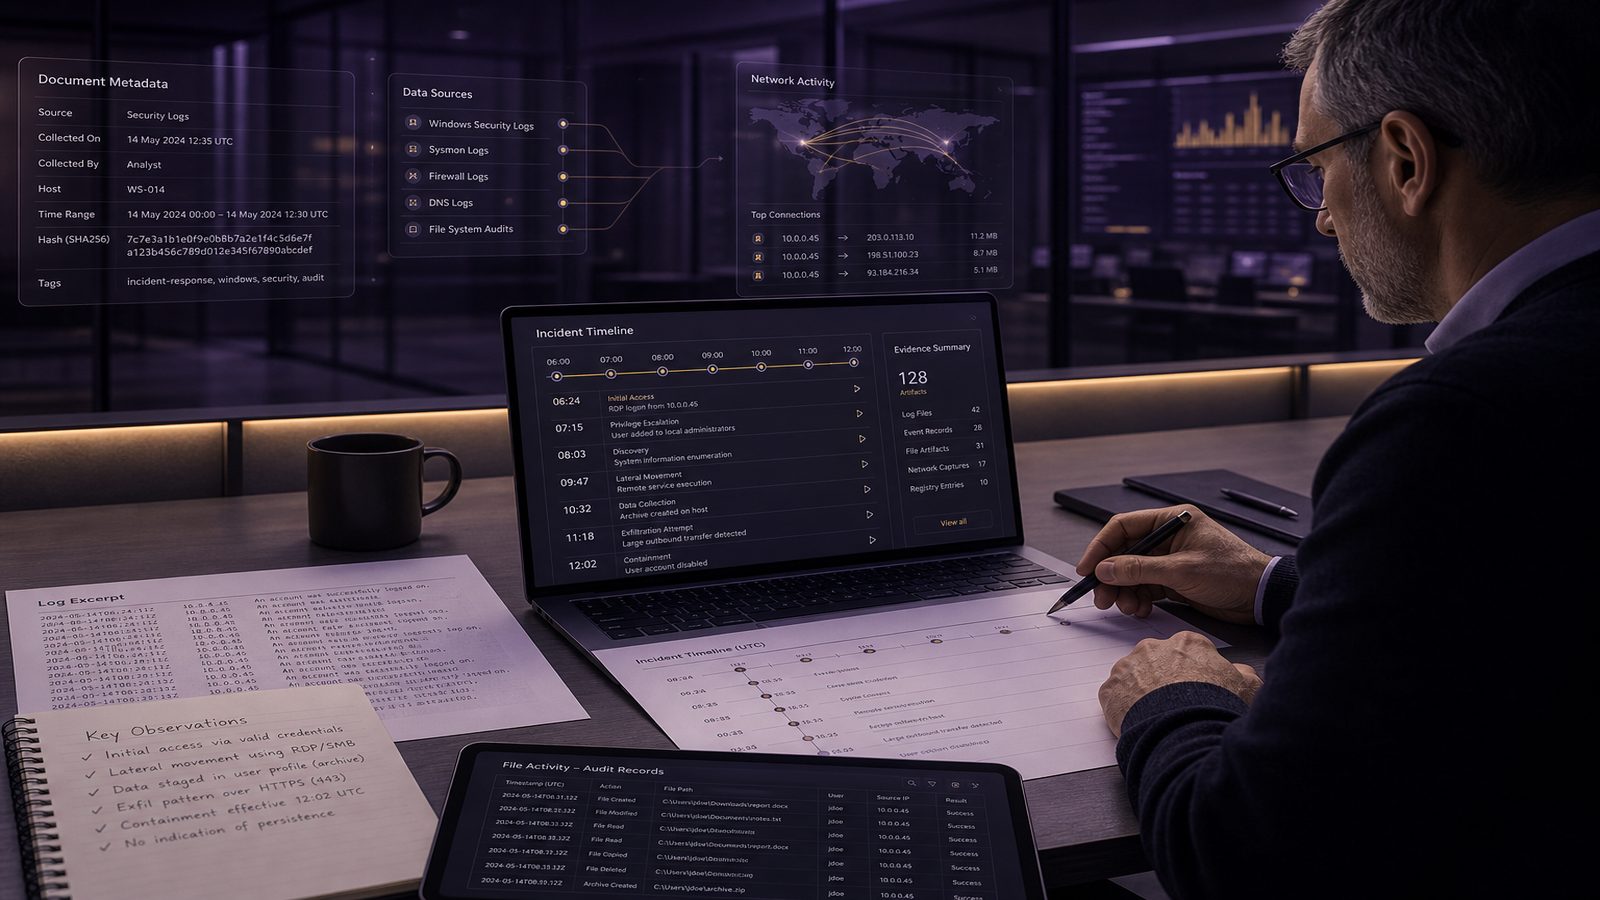
Why digital forensics matters after an incident
When a security incident happens, the immediate focus is usually on stopping the damage. That is sensible.[…]

How third-party software introduces cyber risk for UK SMEs
How third-party software introduces cyber risk for UK SMEs Most UK SMEs rely on software they did[…]

Automating security testing as part of release pipelines
Automating security testing as part of release pipelines For many UK SMEs, software delivery has to balance[…]