
Clear Path Security
IEC 62443 explained for manufacturing organisations
IEC 62443 explained for manufacturing organisations If you run or manage a manufacturing business, cyber security is[…]
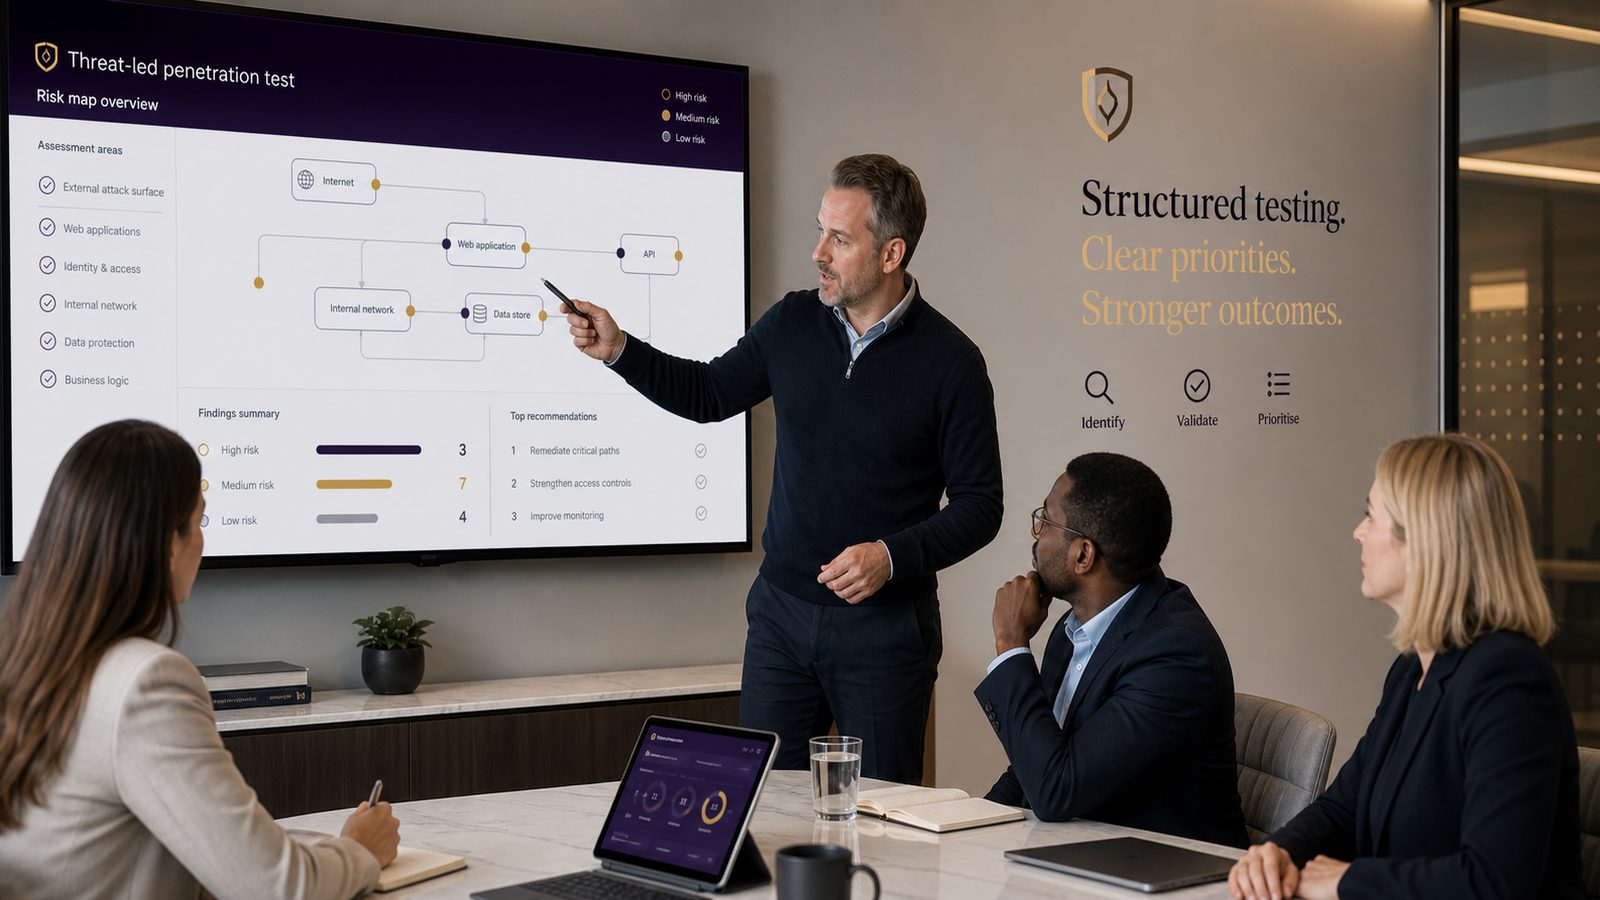
Threat-led penetration testing explained for SMEs
For many UK SMEs, the real question is not whether to test security, but how to test[…]
Mapping ISO 27001 Annex A controls to NIST 800-53
Mapping ISO 27001 Annex A controls to NIST 800-53 For many UK SMEs, ISO/IEC 27001 and NIST[…]
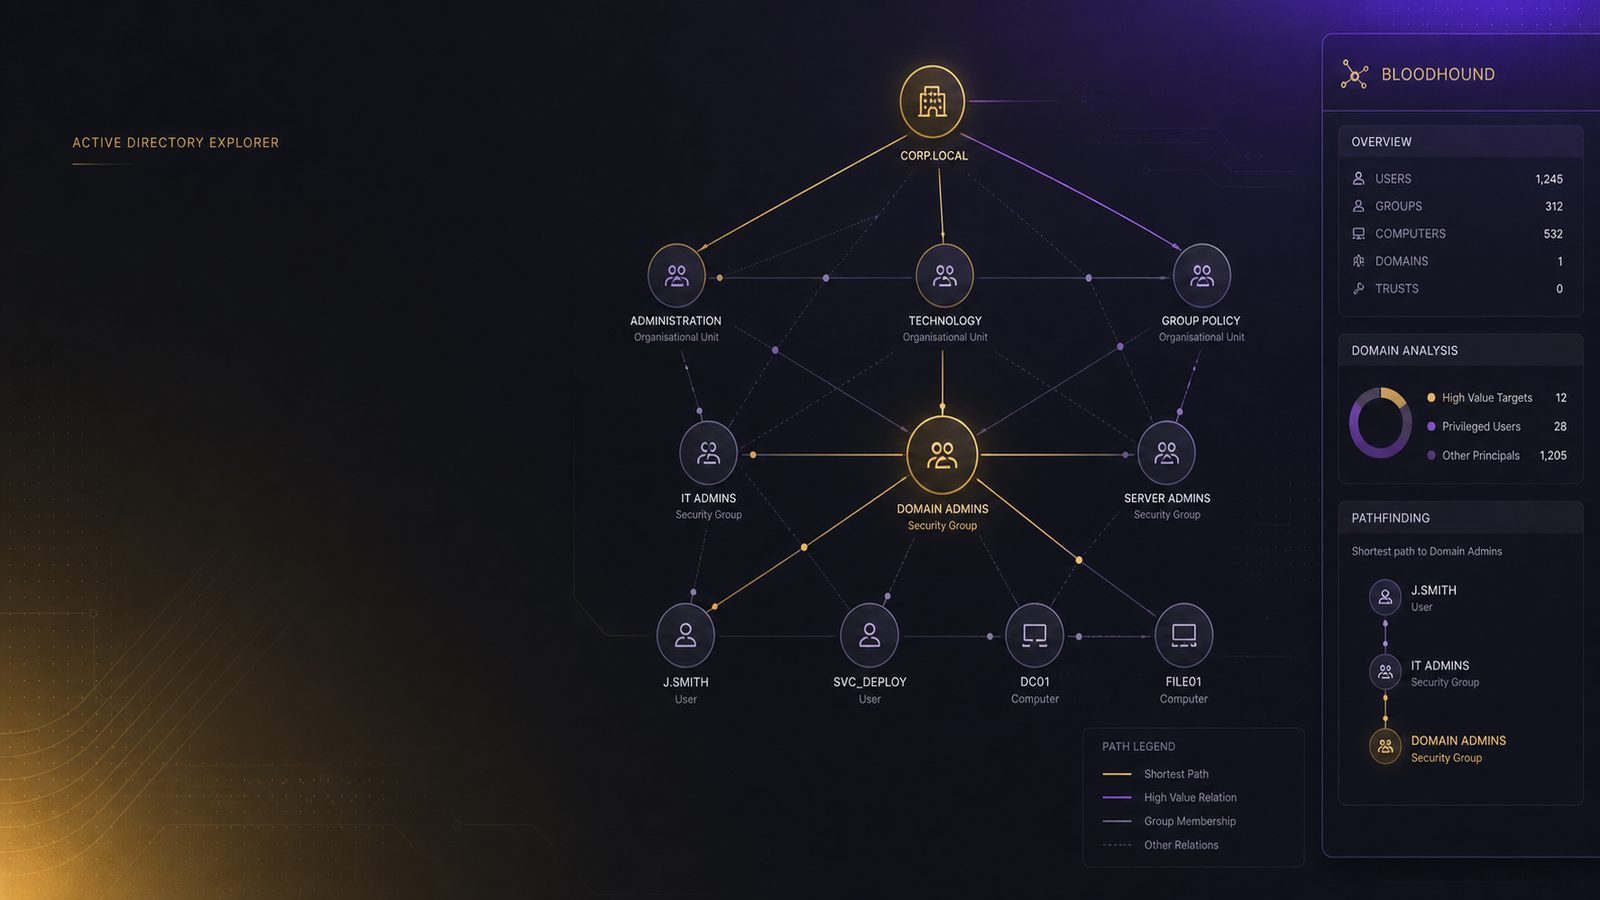
Credential attack simulation using BloodHound: a practical guide for technical practitioners
Credential attack simulation using BloodHound: a practical guide for technical practitioners Credential attack simulation using BloodHound is[…]
Common identity-based attacks explained for SMEs
Common identity-based attacks explained for SMEs For many small and medium-sized businesses, the biggest cyber risk is[…]
Secure baseline configurations for Microsoft 365
Secure baseline configurations for Microsoft 365 Microsoft 365 is often the centre of identity, email, collaboration, and[…]
Continuous improvement loops in security operations: a practical guide for technical teams
Continuous improvement loops in security operations: a practical guide for technical teams Security operations improve fastest when[…]
UK Secure Software Code of Connection explained for suppliers
UK Secure Software Code of Connection explained for suppliers A Code of Connection (CoCo) is the set[…]
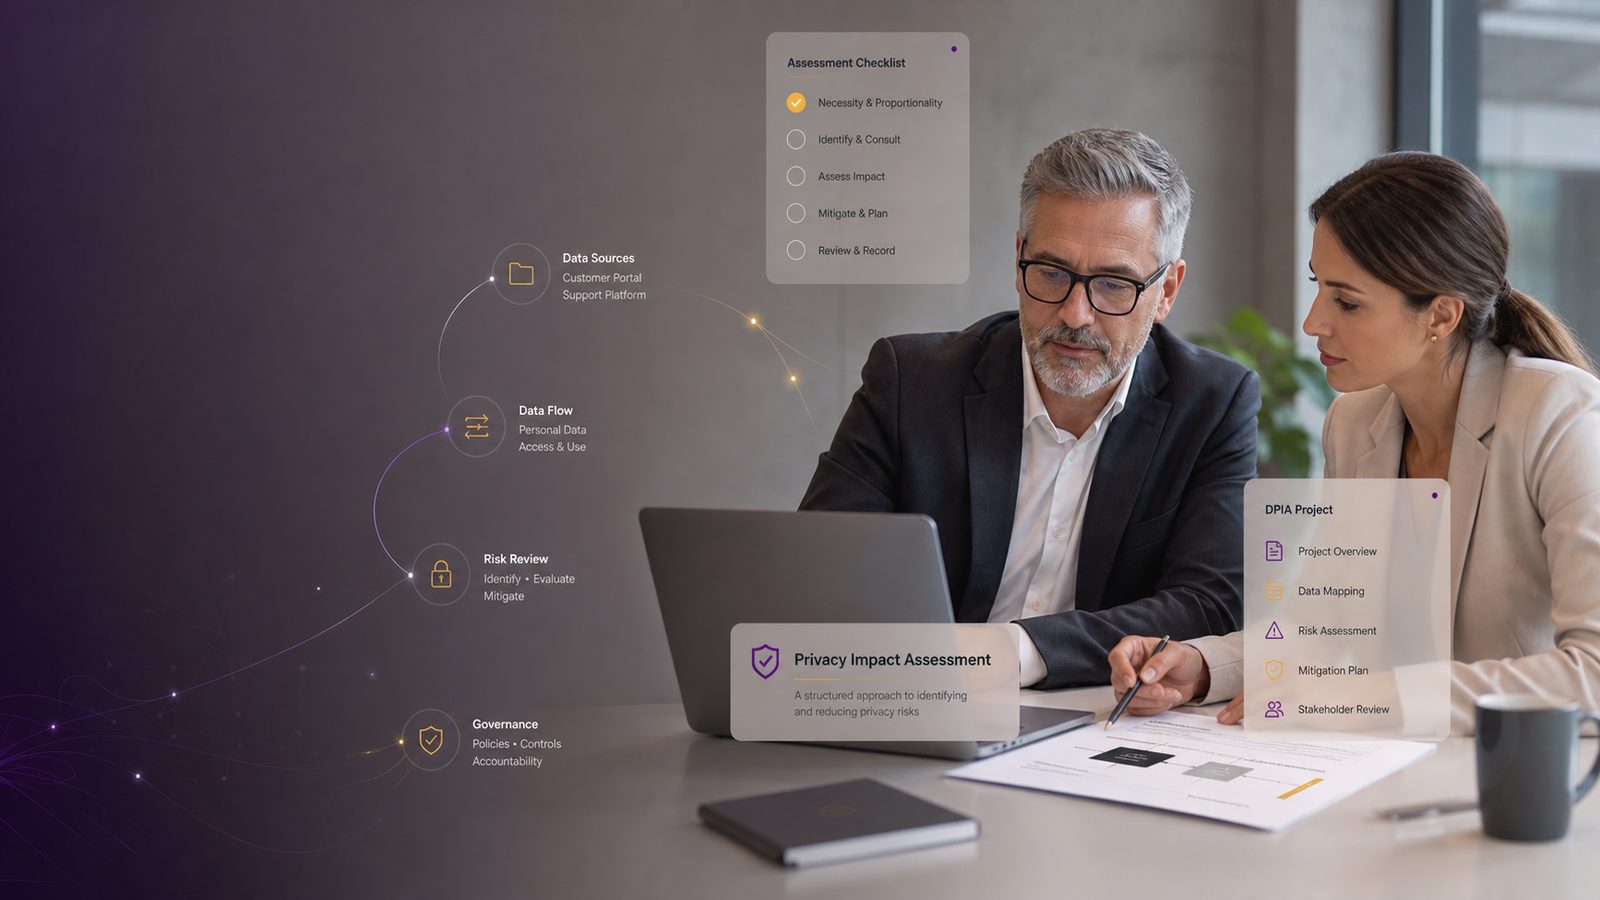
Data protection impact assessments explained for UK SMEs
What a data protection impact assessment is and why it matters A data protection impact assessment is[…]
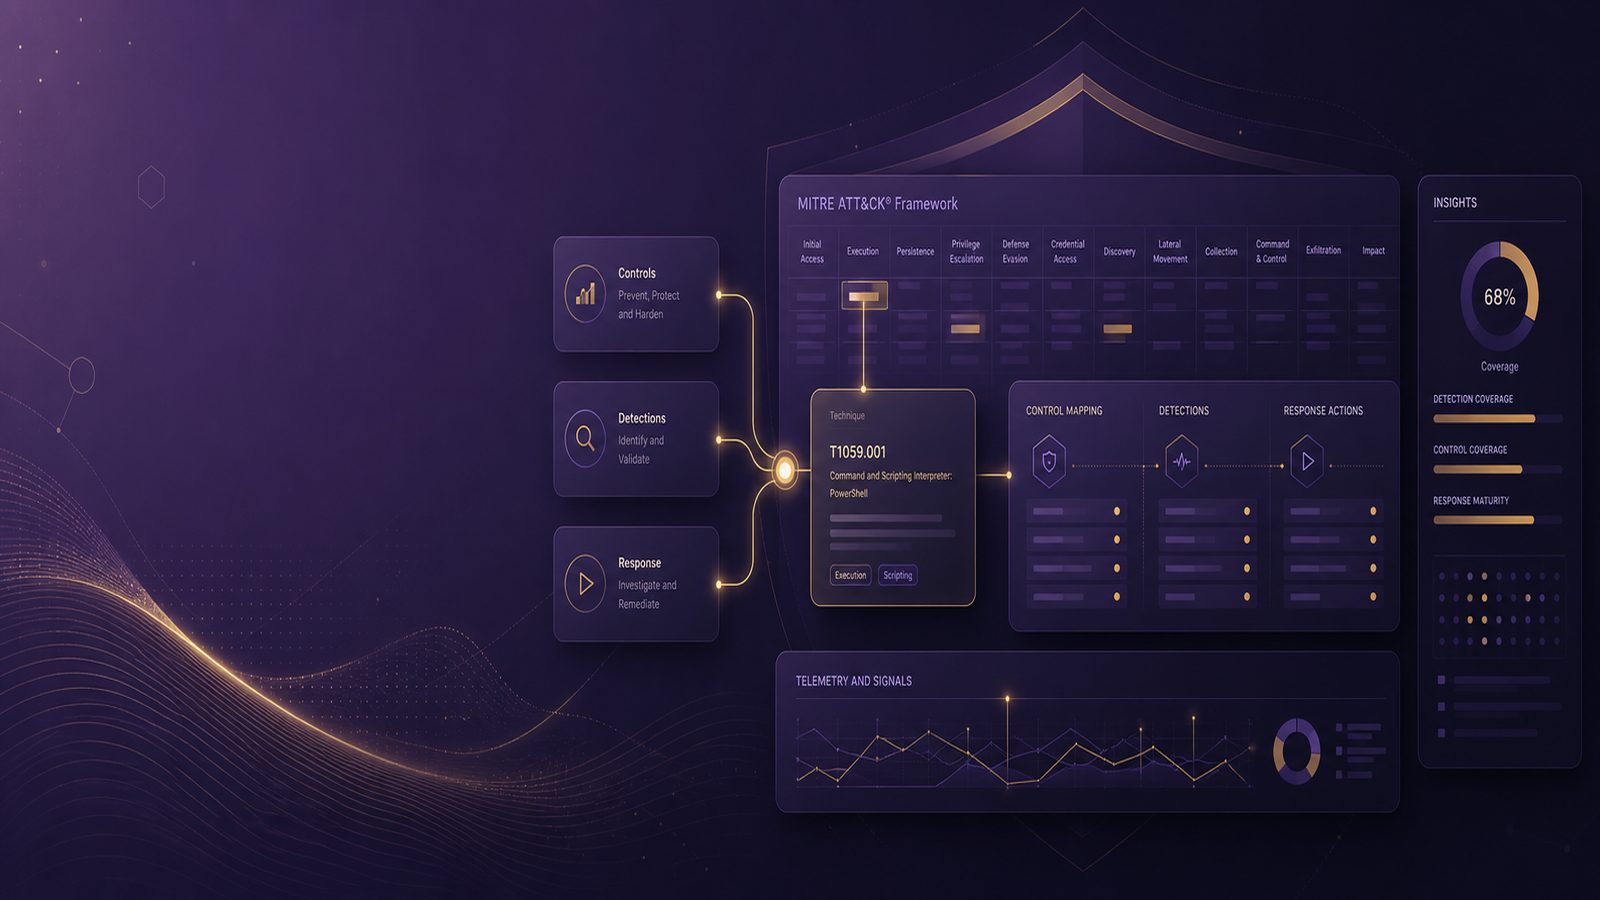
Mapping detections and controls to MITRE ATT&CK: a practical guide for technical teams
Mapping detections and controls to MITRE ATT&CK: a practical guide for technical teams MITRE ATT&CK is useful[…]