Clear Path Security
Vulnerability disclosure and patch management best practice for UK SMEs
Key takeaways Keep vulnerability disclosure and patch management in one joined-up process so reports are logged, assessed,[…]
Generating SBOMs using Syft and Grype
Generating SBOMs using Syft and Grype Syft and Grype are complementary open-source tools from Anchore: Syft produces[…]
Procuring AI systems securely as an organisation
Procuring AI systems securely as an organisation For many UK SMEs, AI now looks less like a[…]
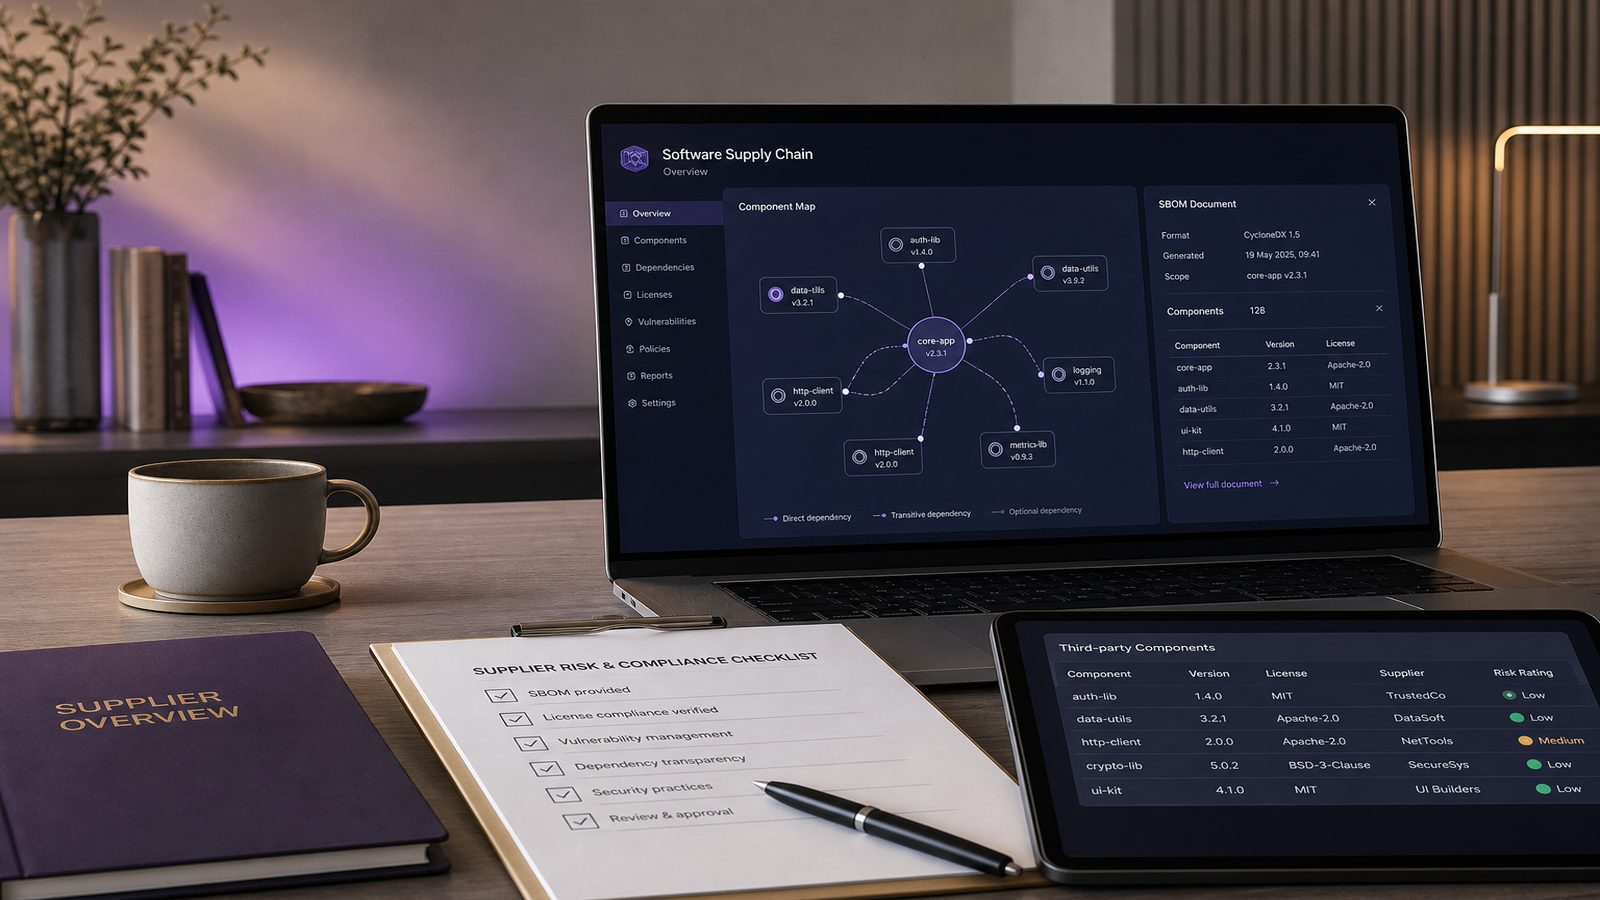
Why SBOMs matter for software buyers and regulators
Why SBOMs matter for software buyers and regulators For many UK SMEs, software is now a core[…]
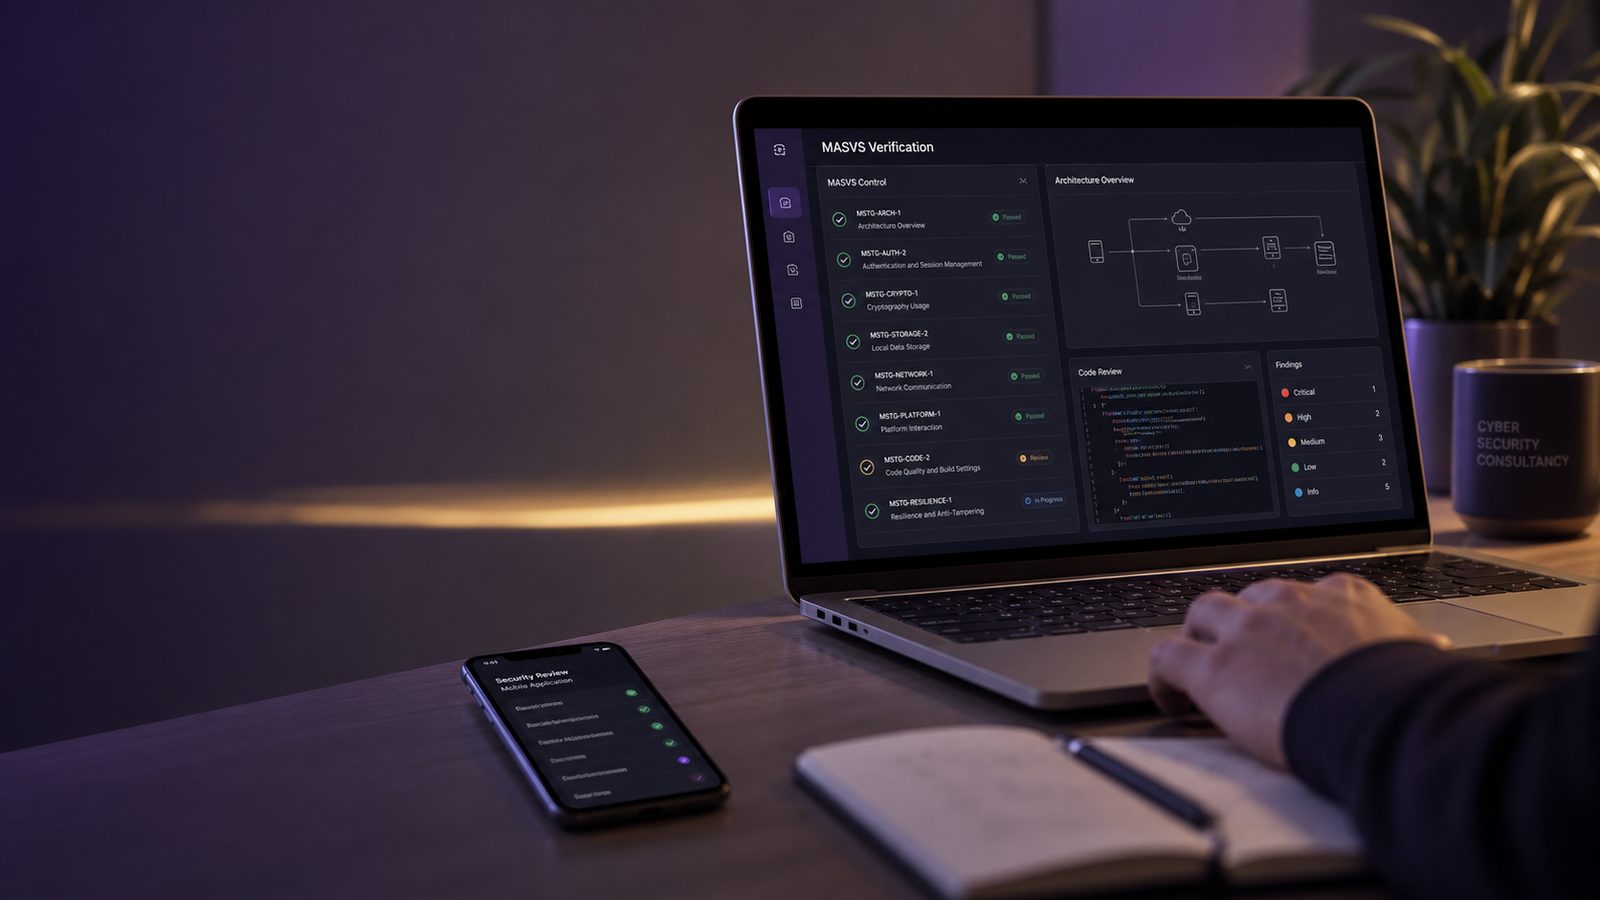
Applying OWASP MASVS for mobile application security
Applying OWASP MASVS for mobile application security OWASP MASVS (Mobile Application Security Verification Standard) is the baseline[…]
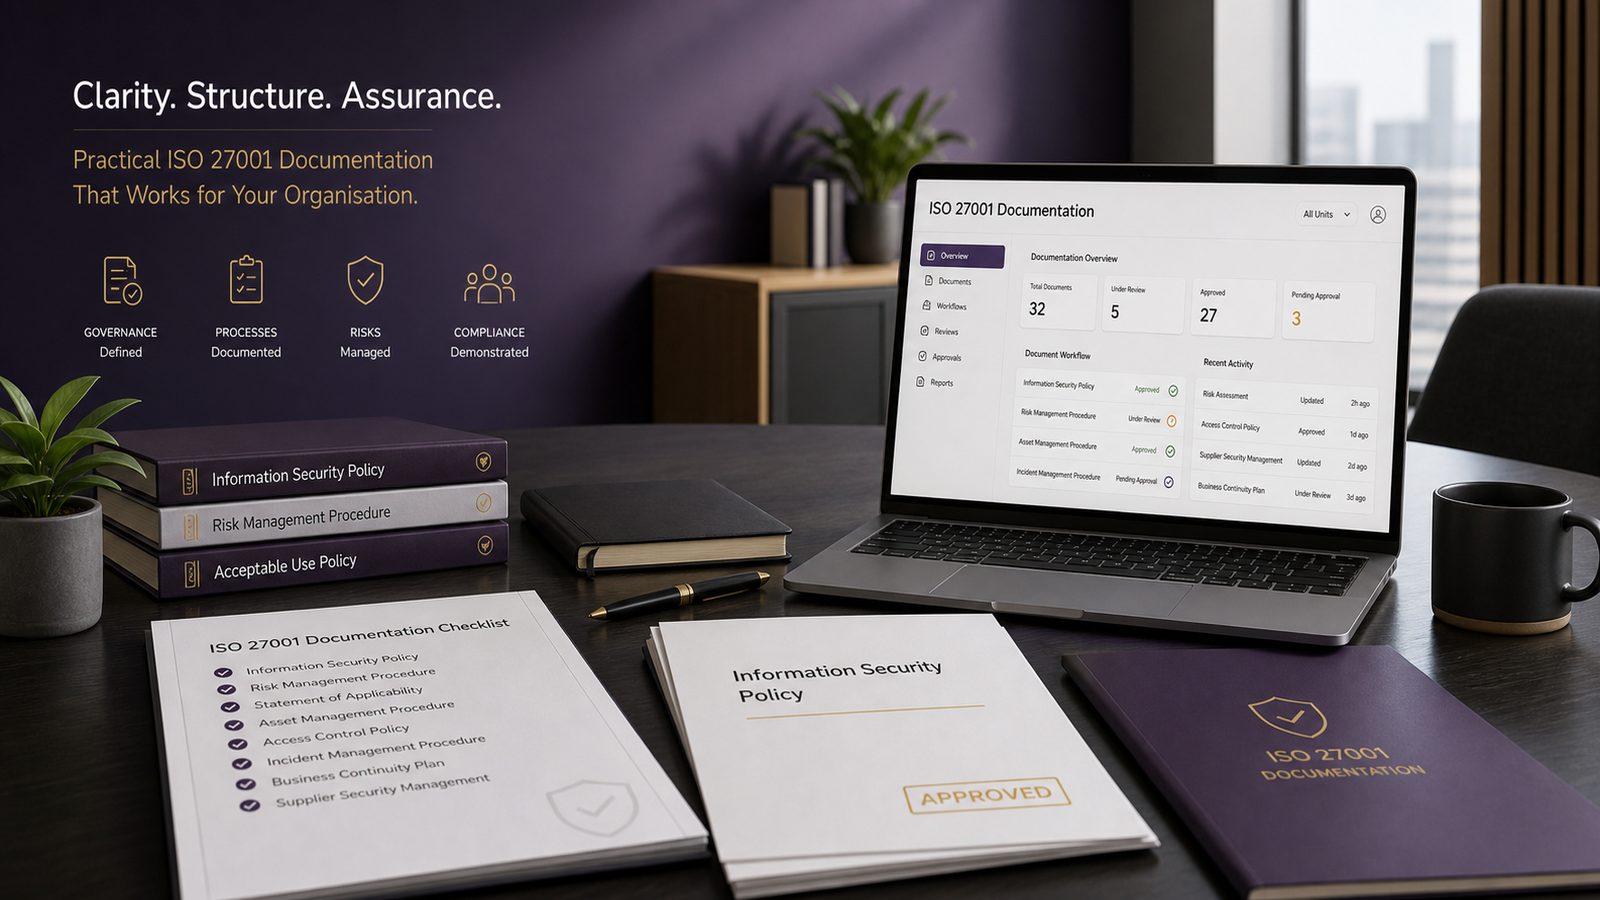
Policies and procedures required by ISO 27001: a practical guide for UK SMEs
Policies and procedures required by ISO 27001: a practical guide for UK SMEs If you are trying[…]
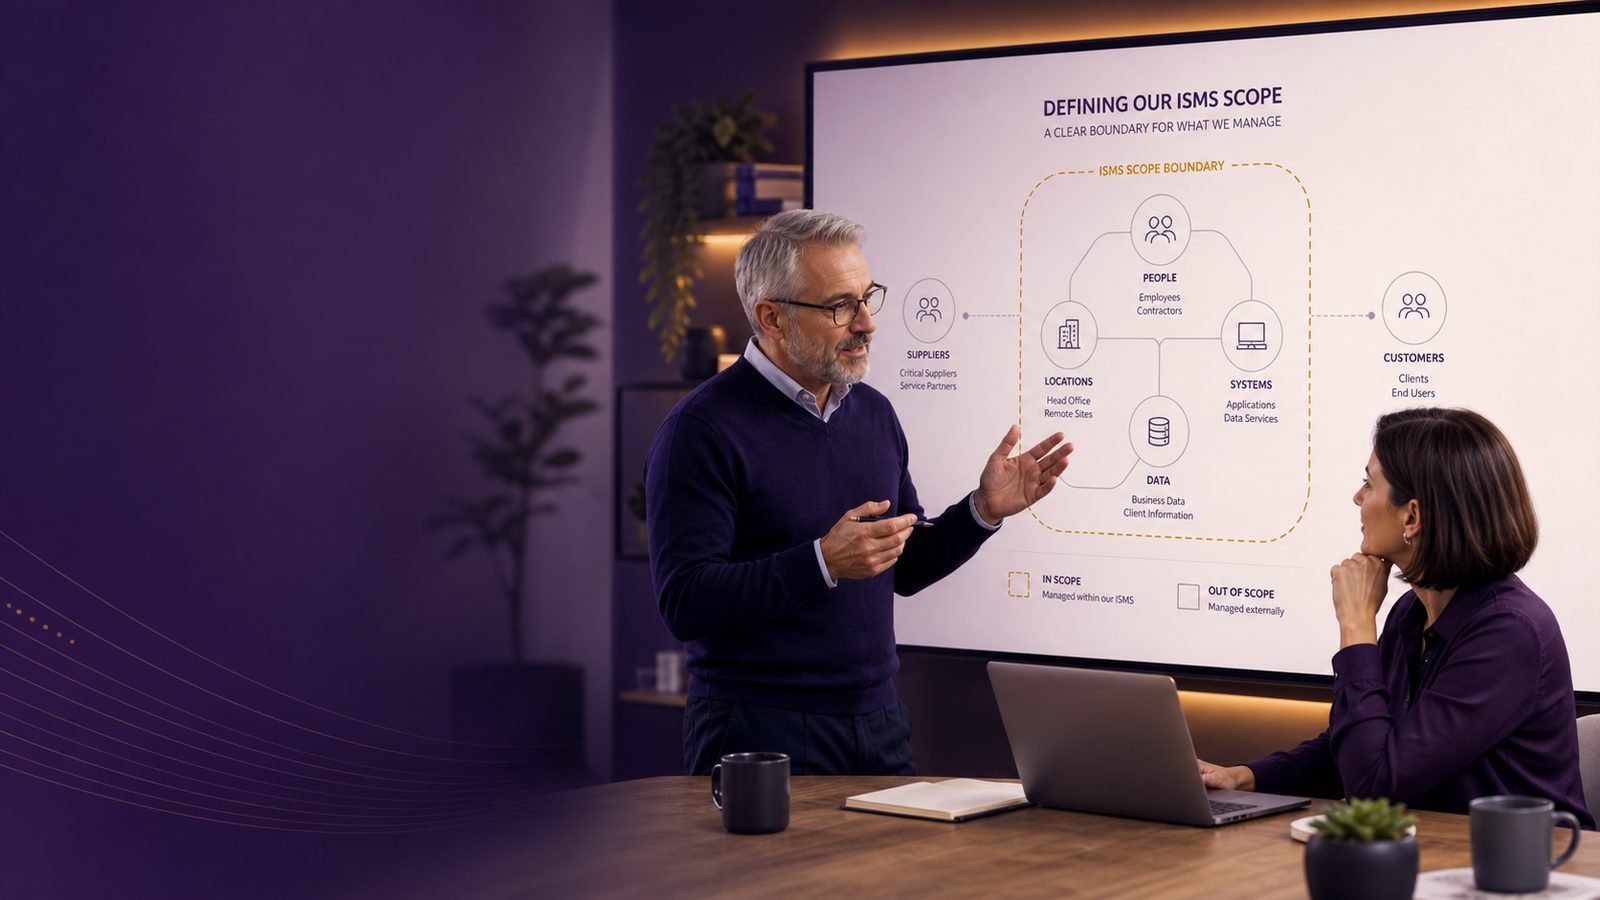
ISMS scope definition for small organisations
ISMS scope definition for small organisations ISMS scope is the written boundary of your information security management[…]
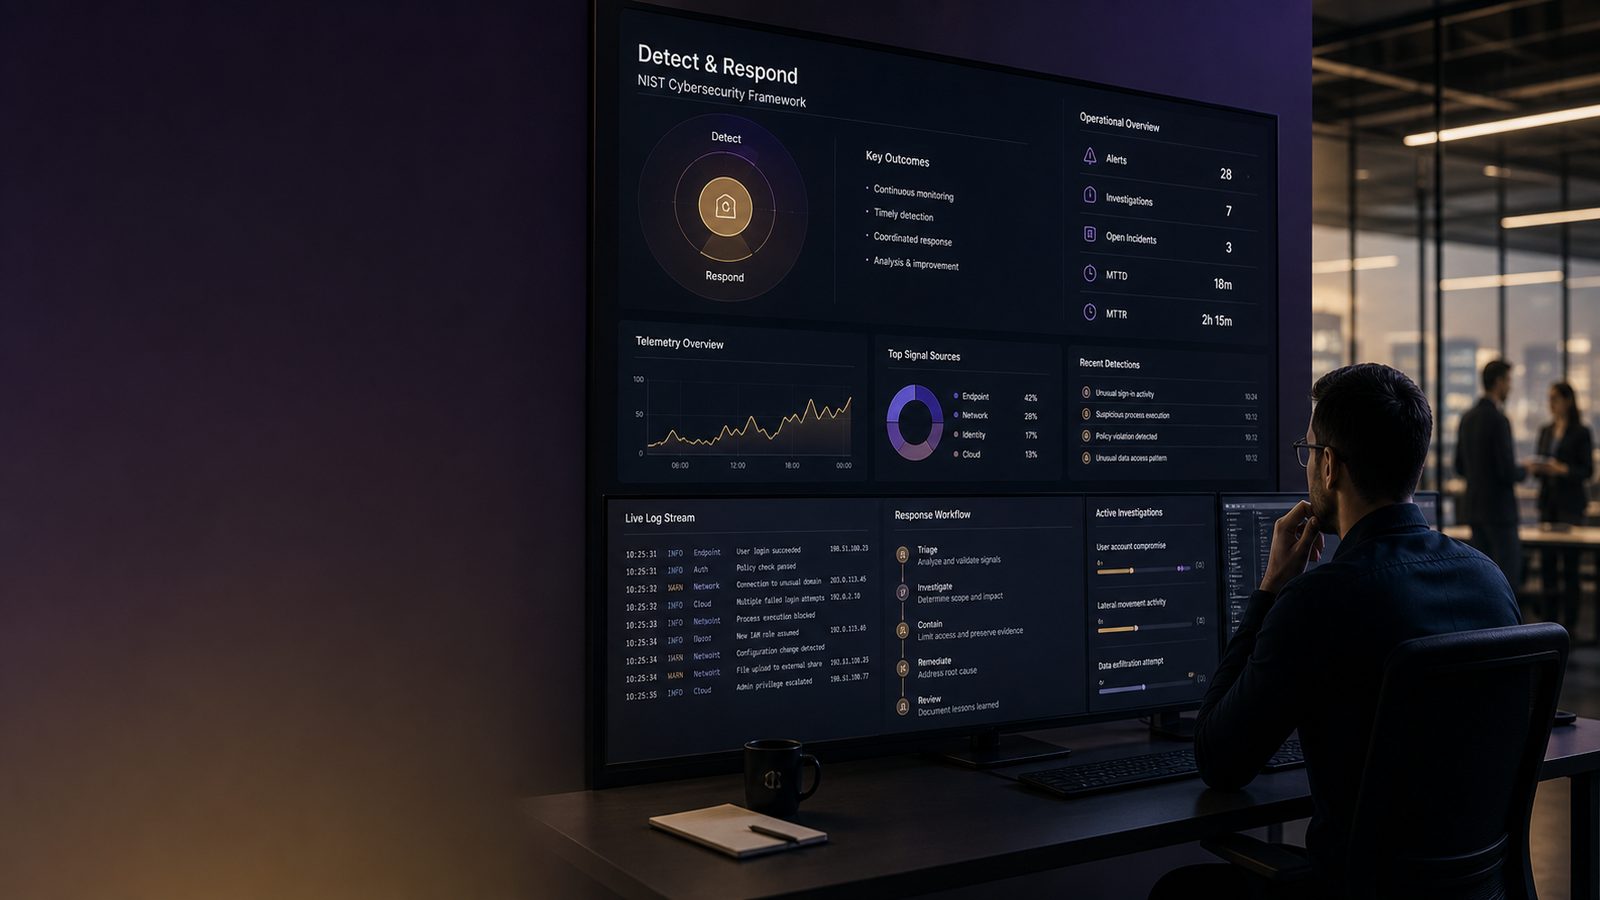
Implementing Detect and Respond functions in NIST CSF
Implementing Detect and Respond functions in NIST CSF In NIST CSF 2.0 the Detect function covers continuous[…]
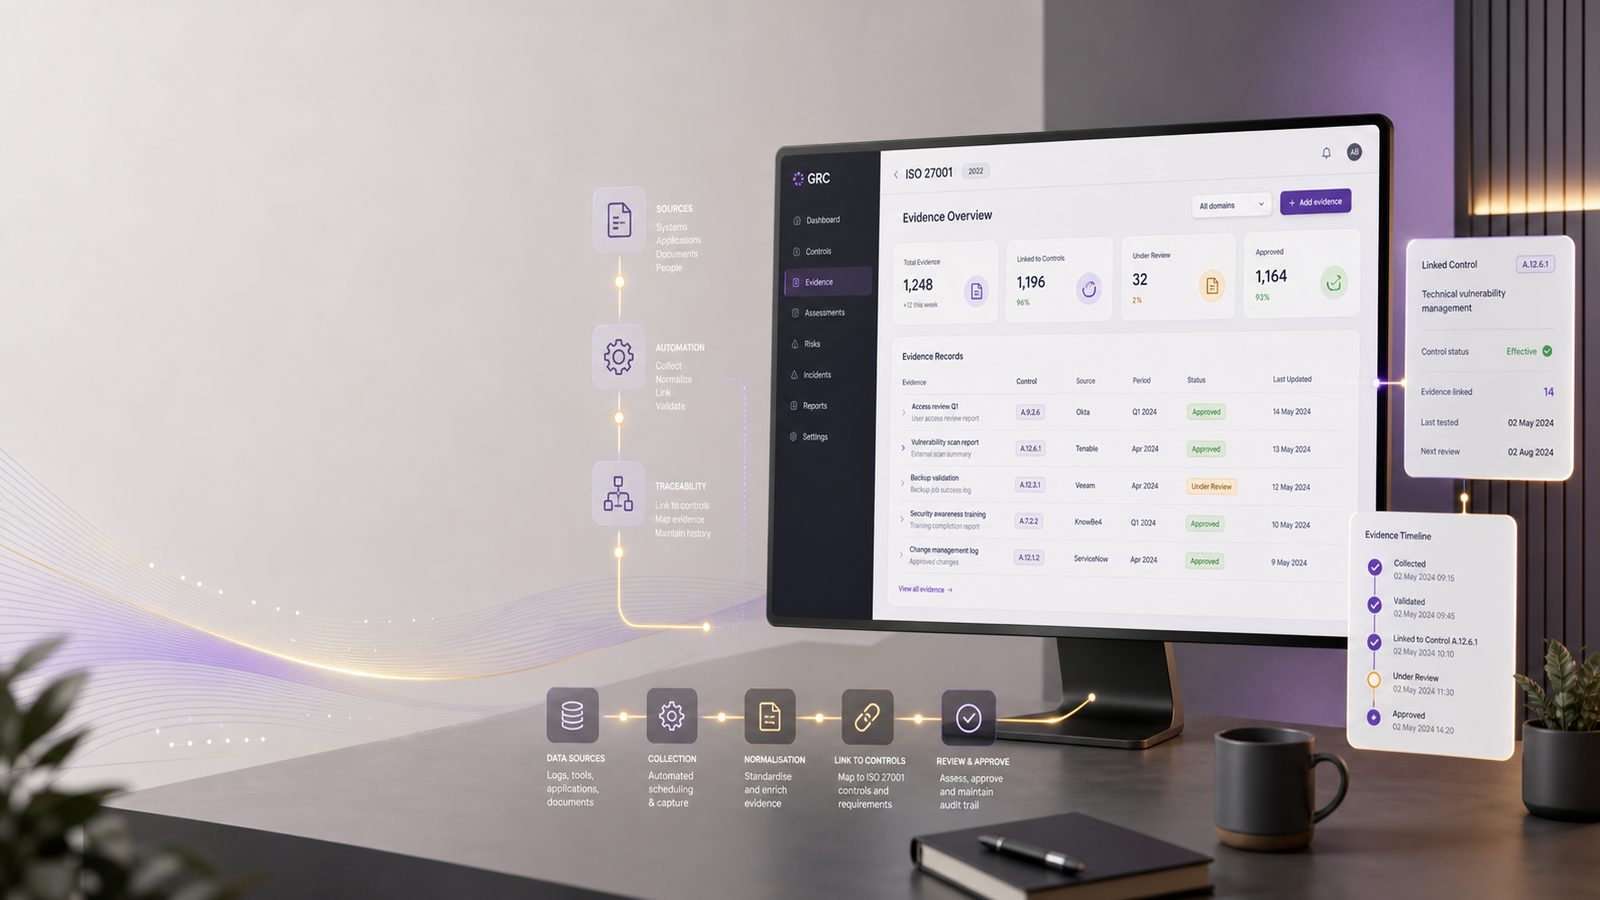
Automating ISO 27001 evidence collection using GRC tools
Automating ISO 27001 evidence collection using GRC tools For many UK SMEs, the hardest part of running[…]
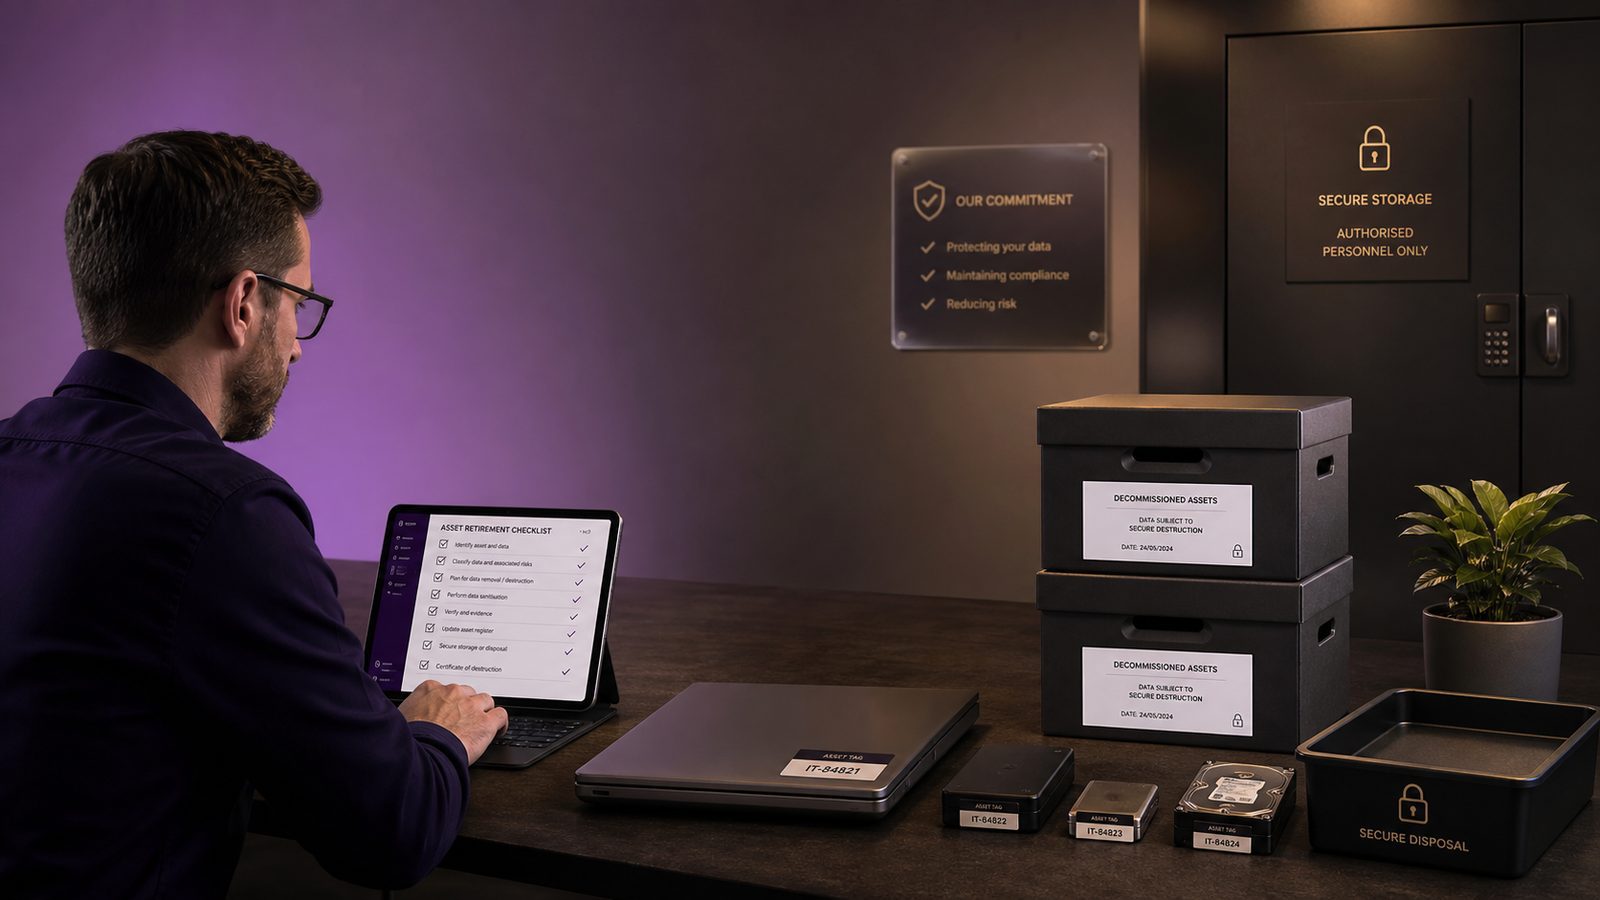
Secure decommissioning and data destruction practices for UK SMEs
Secure decommissioning and data destruction practices for UK SMEs Decommissioning is often treated as an IT tidy-up[…]