Clear Path Security
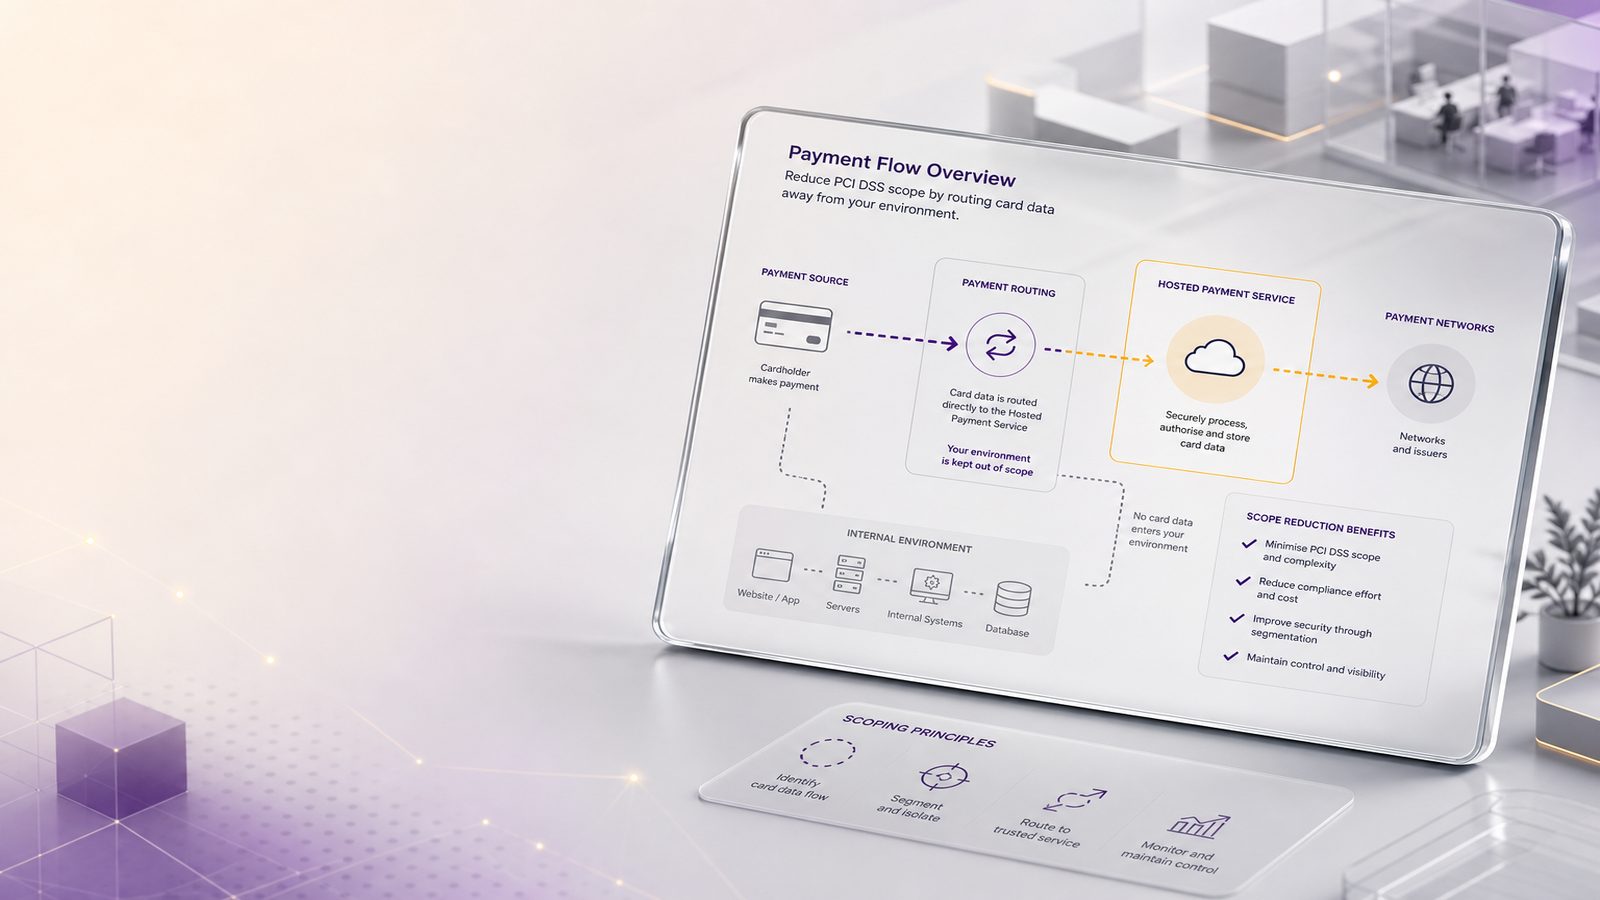
Reducing PCI DSS scope effectively: practical steps for UK SMEs
Reducing PCI DSS scope effectively: practical steps for UK SMEs If your business takes card payments, PCI[…]
Mapping NIST CSF to ISO 27001 in practice
Mapping NIST CSF to ISO 27001 in practice For many UK SMEs, NIST CSF and ISO 27001[…]
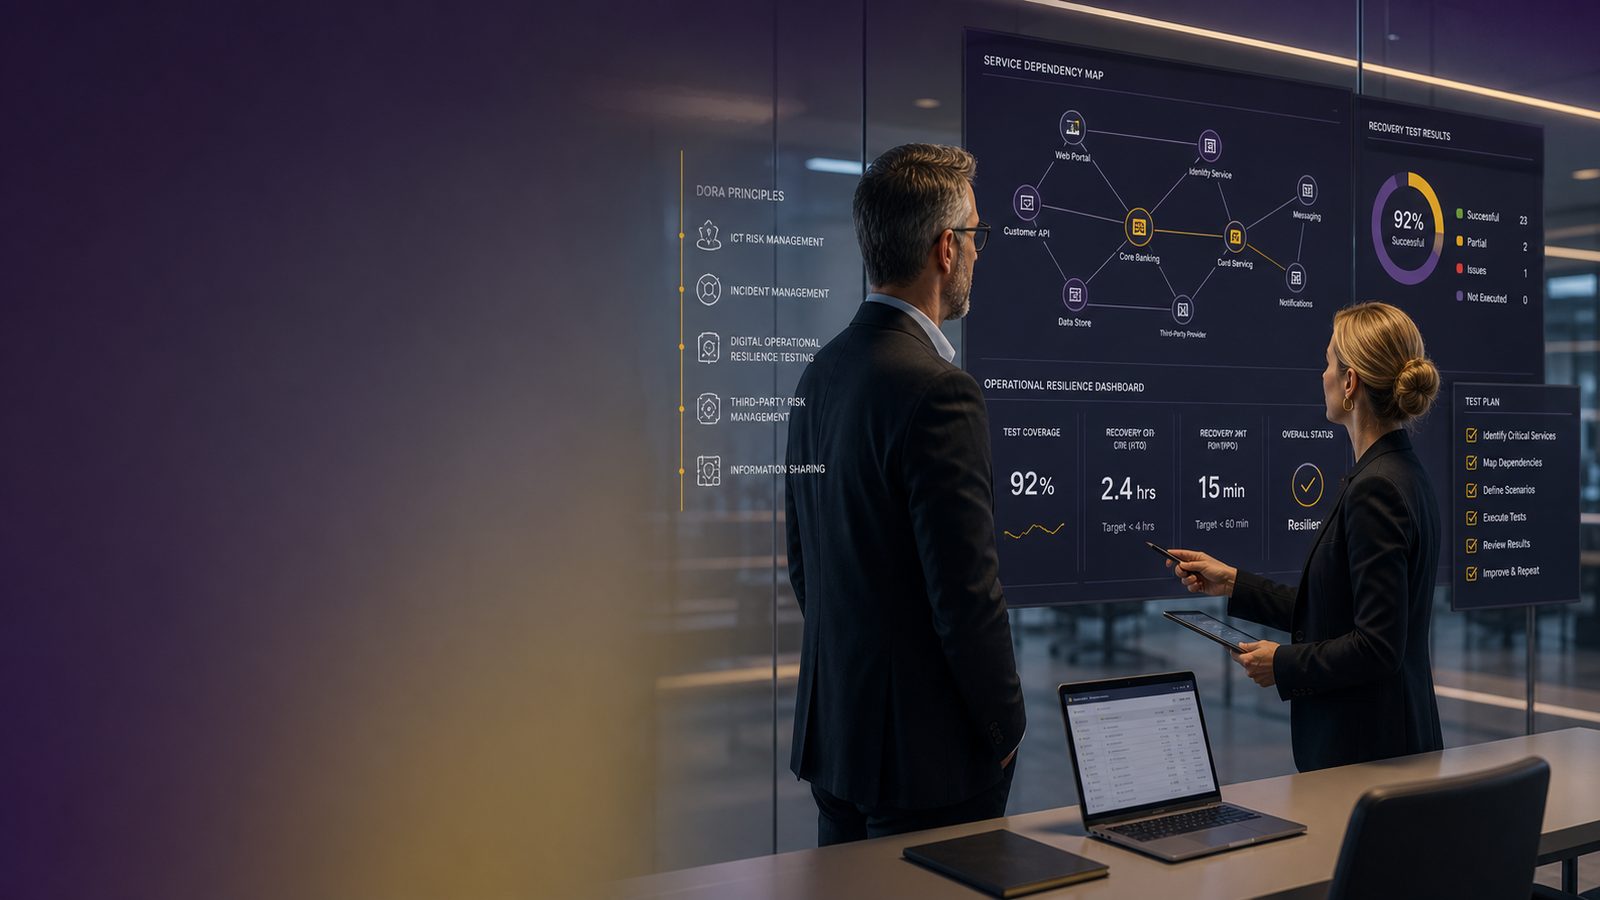
Operational resilience testing under DORA
Key takeaways Operational resilience testing under DORA should prove that critical services can continue or recover under[…]
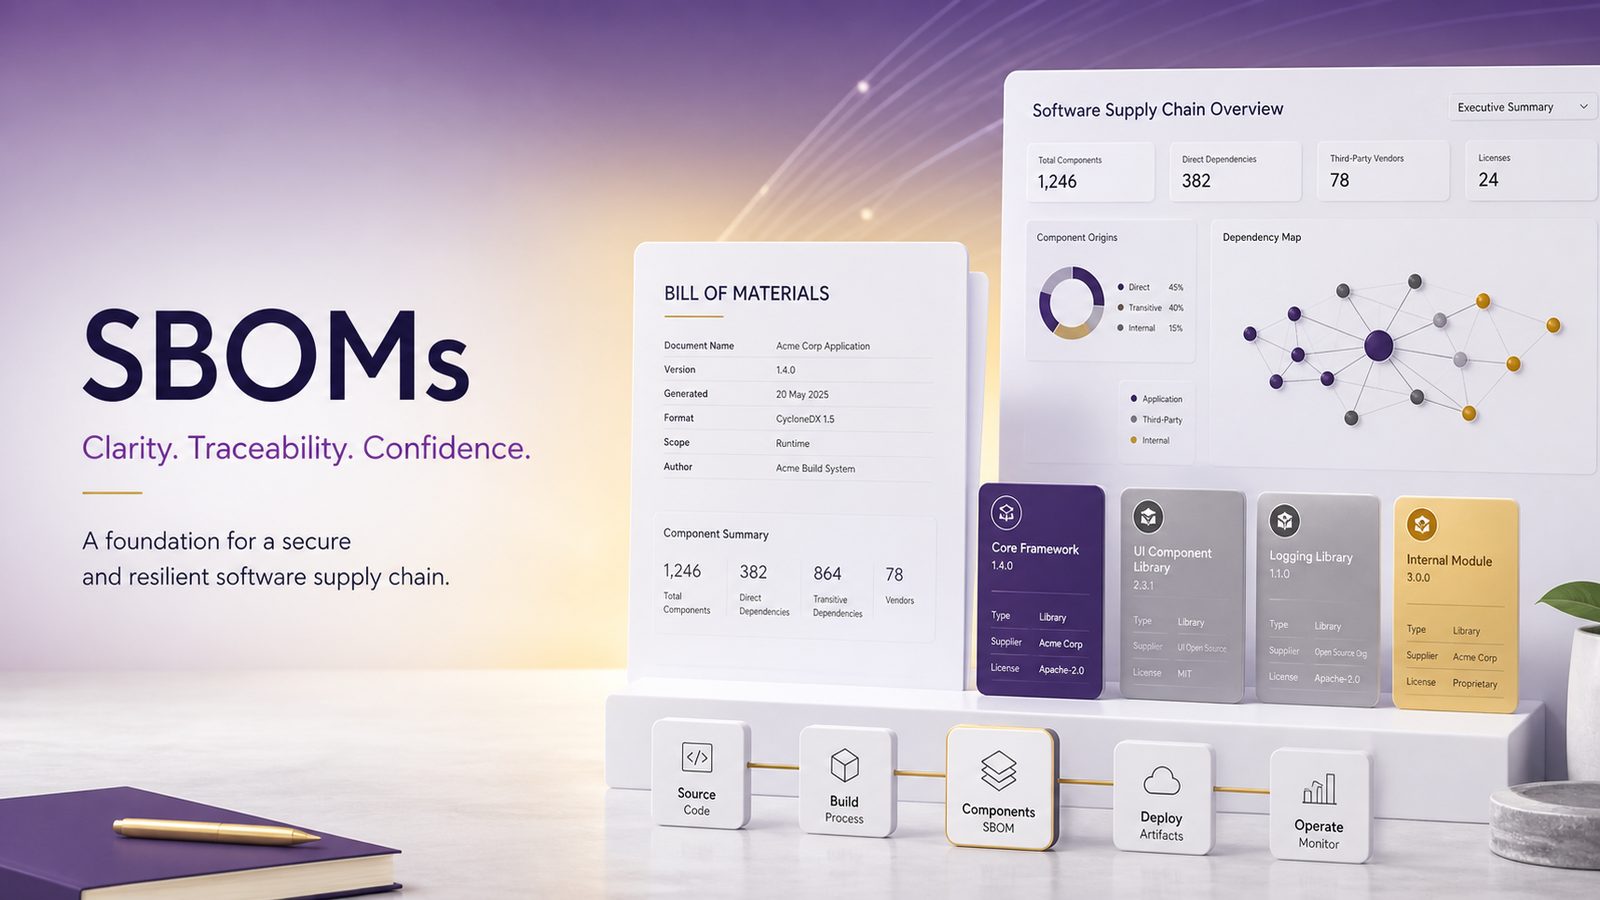
SBOMs explained for non-technical stakeholders
Key takeaways An SBOM is a clear list of what is inside a software product, including its[…]
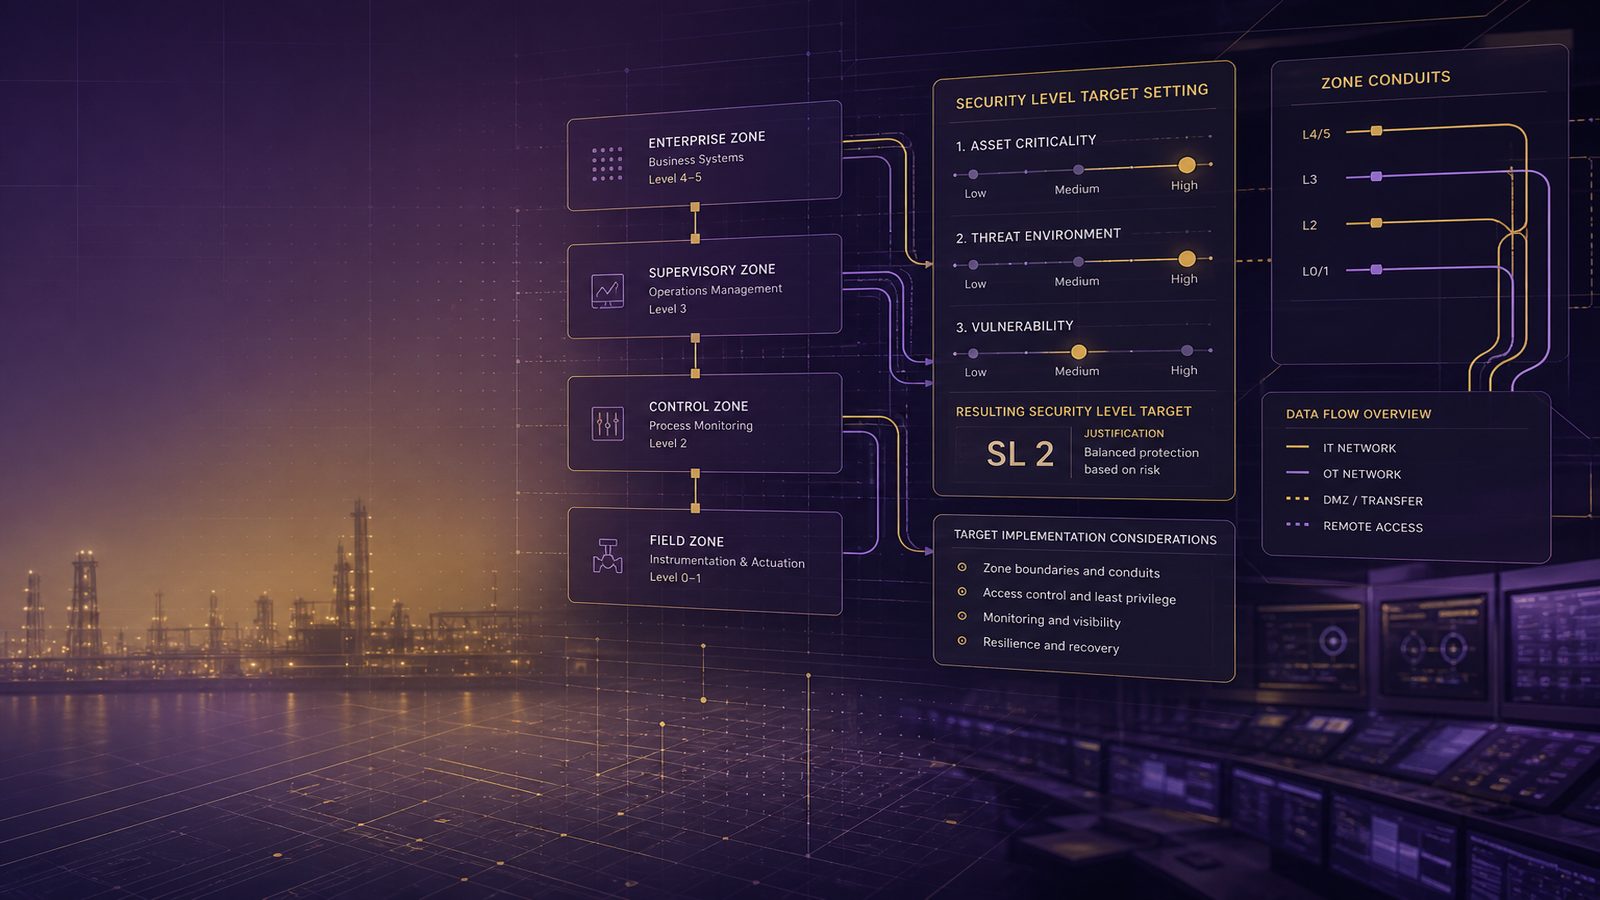
Setting security level targets under IEC 62443
Setting security level targets under IEC 62443 is one of the most important design decisions in an[…]
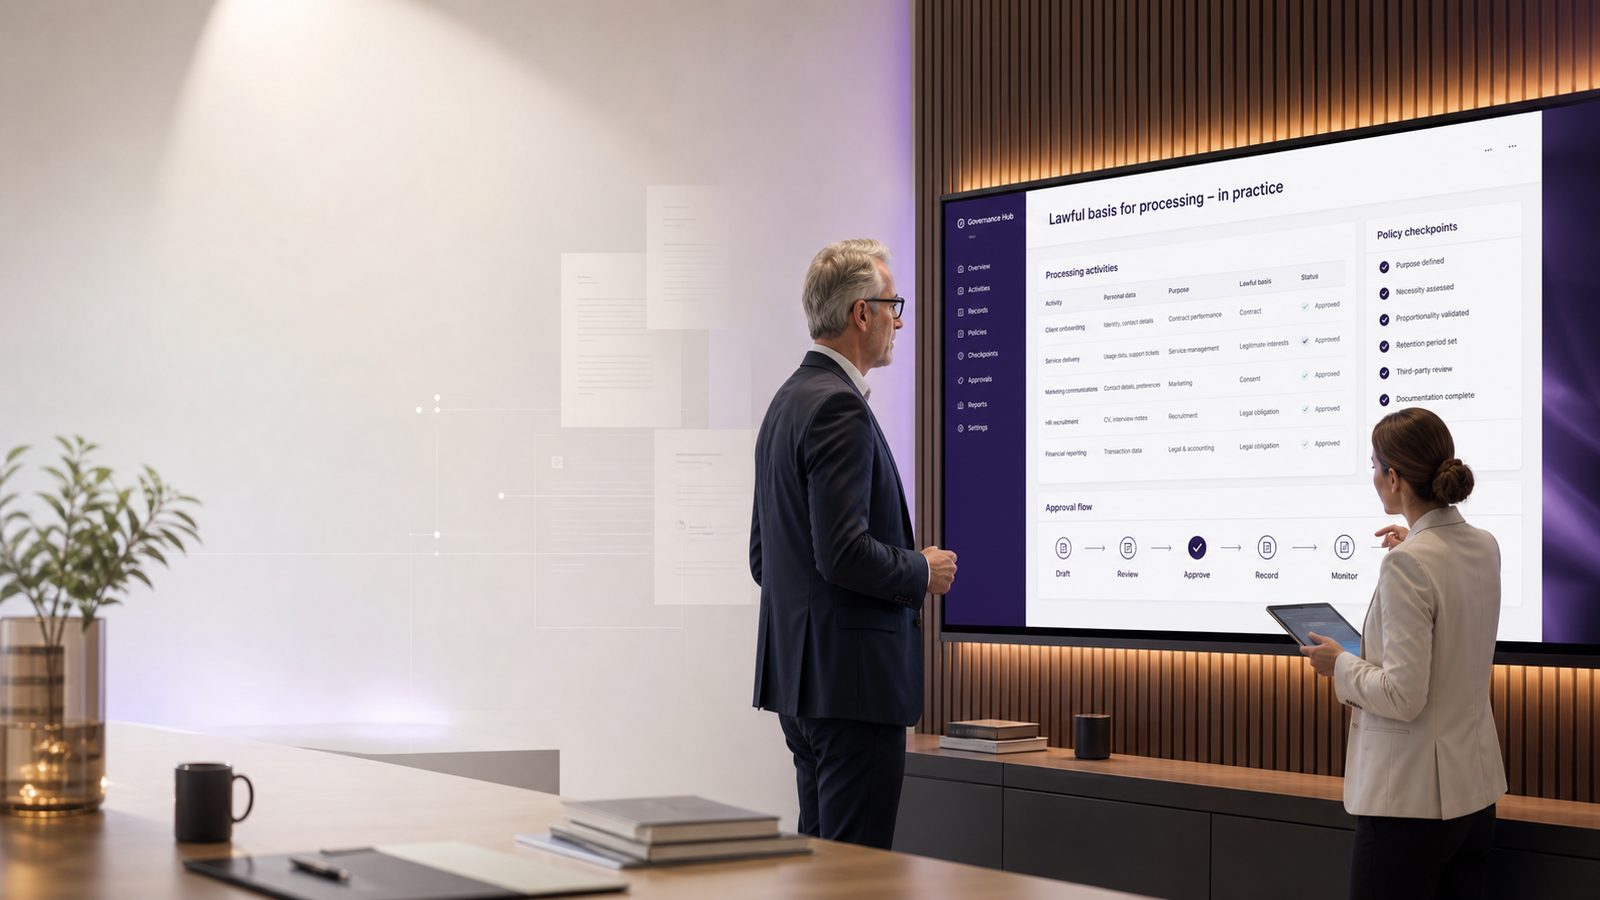
Lawful basis for processing personal data in practice
Key takeaways Start with the business purpose, then choose the lawful basis that genuinely fits that purpose.[…]
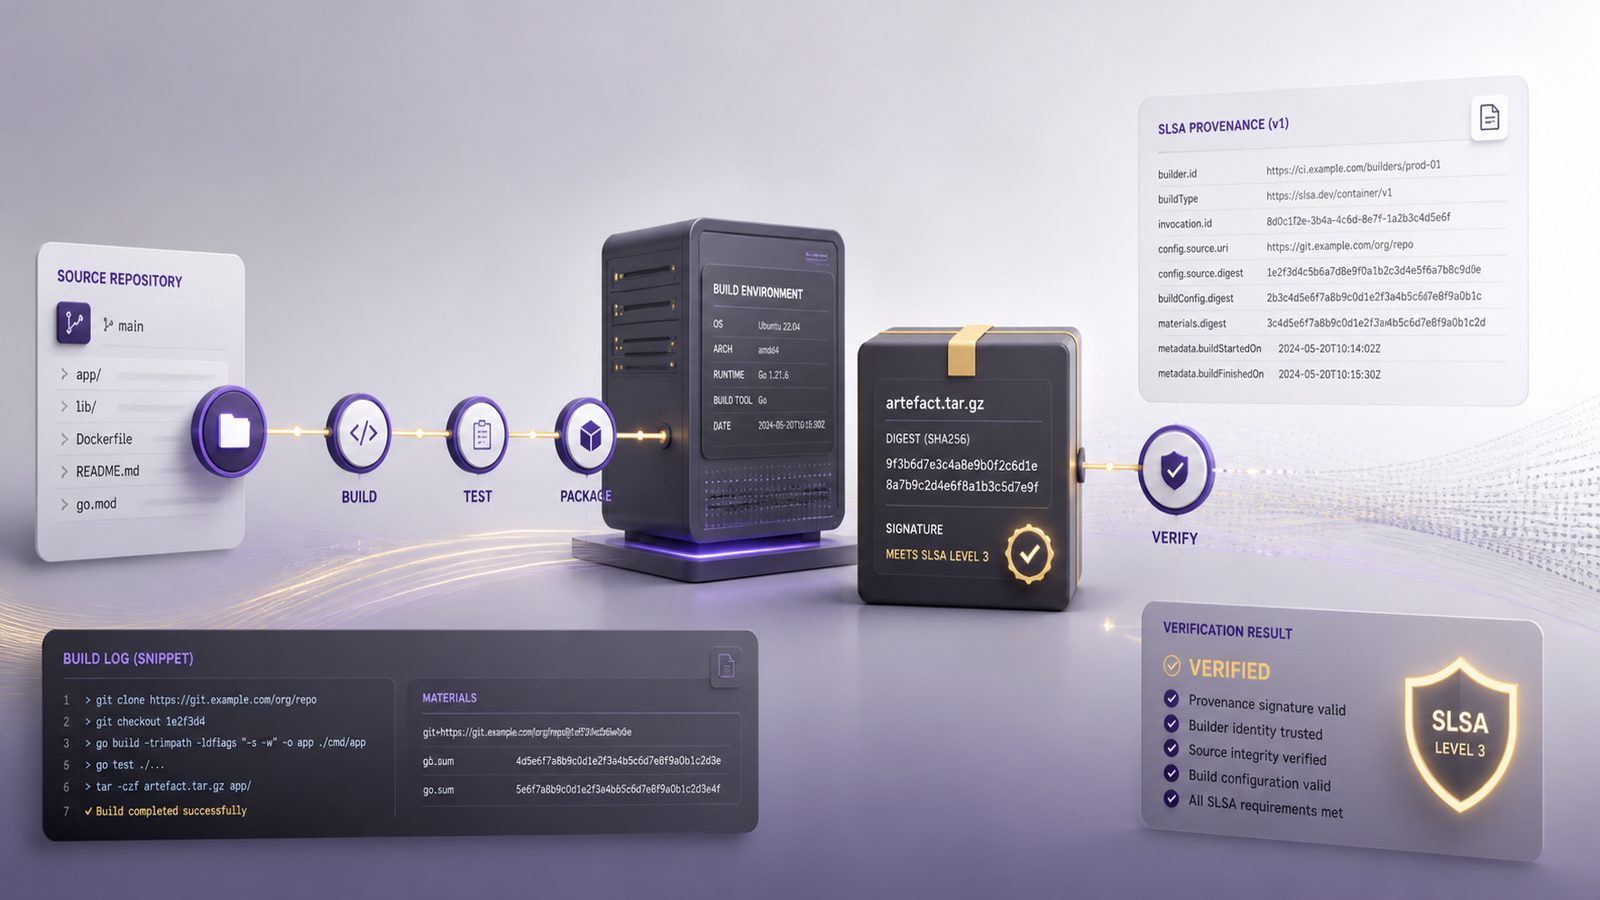
Generating and verifying SLSA build provenance for artifacts
SLSA build provenance is a signed record of how an artifact was built: the source, the builder,[…]
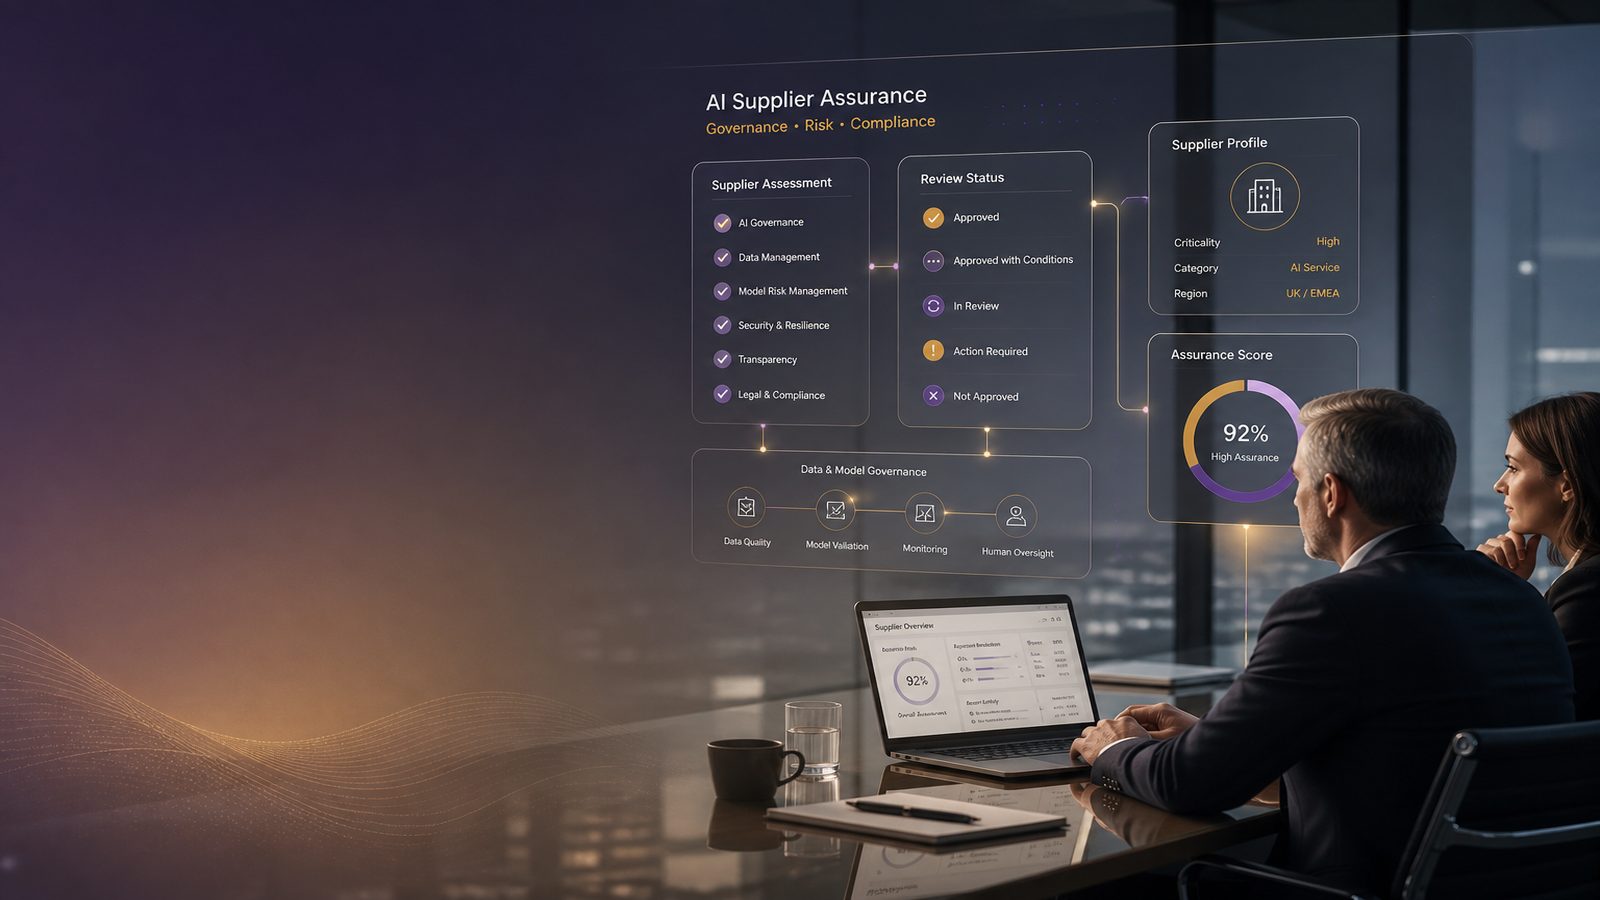
AI supplier assurance and governance expectations for UK SMEs
For many UK SMEs, the biggest risk with artificial intelligence is not whether the tool looks impressive[…]
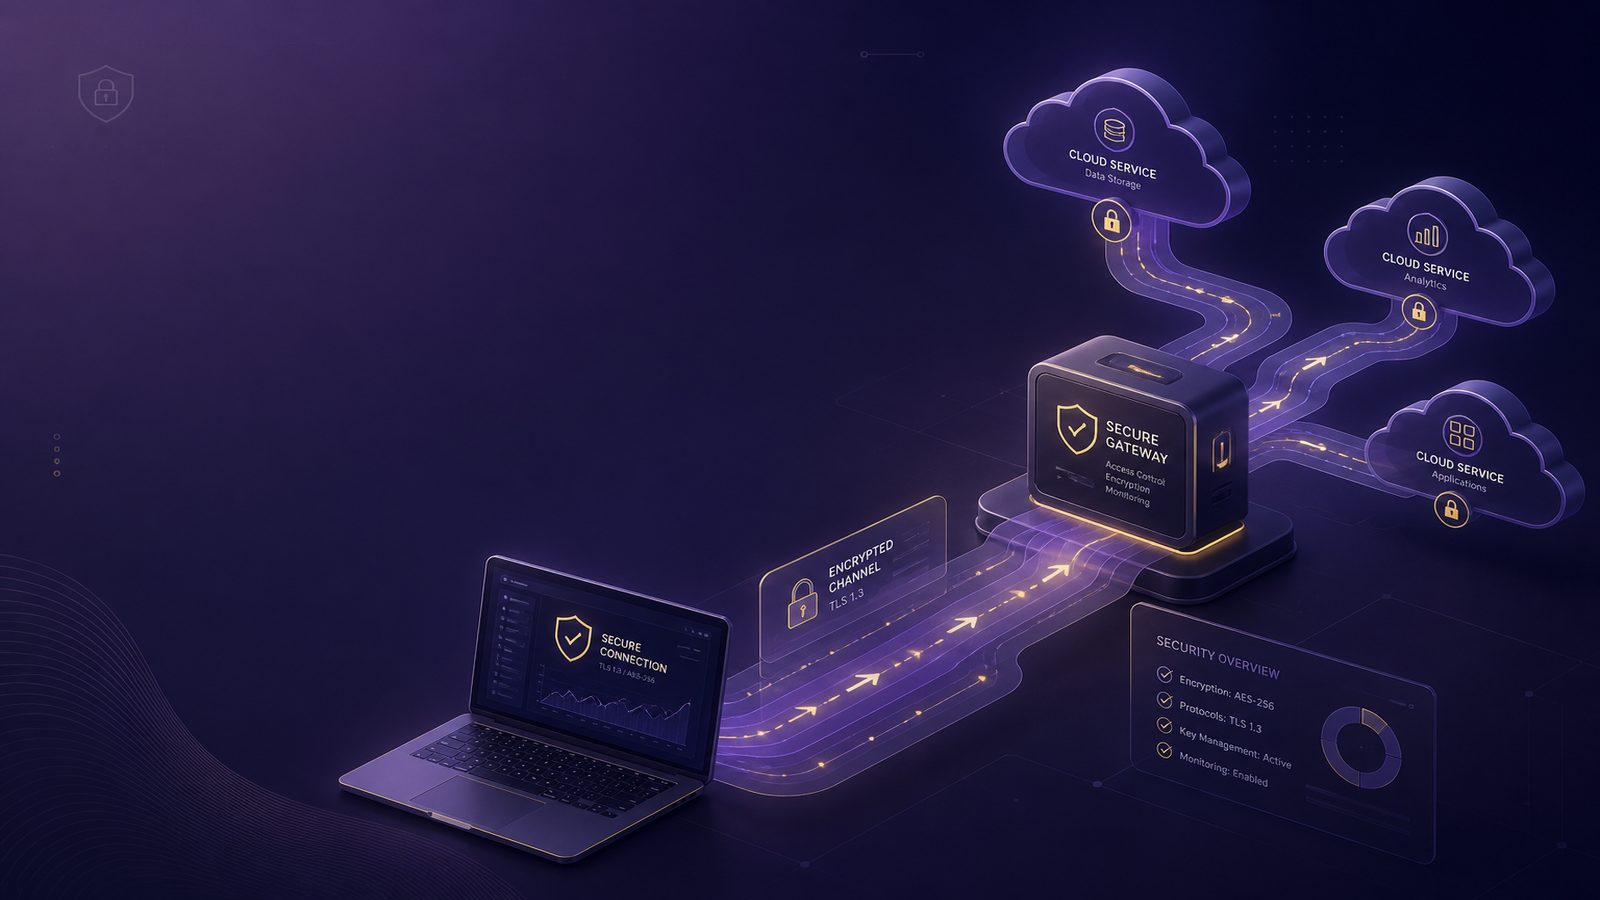
Data protection through encryption and secure channels for UK SMEs
Key takeaways Start with the data that would hurt most if exposed, then apply encryption where it[…]
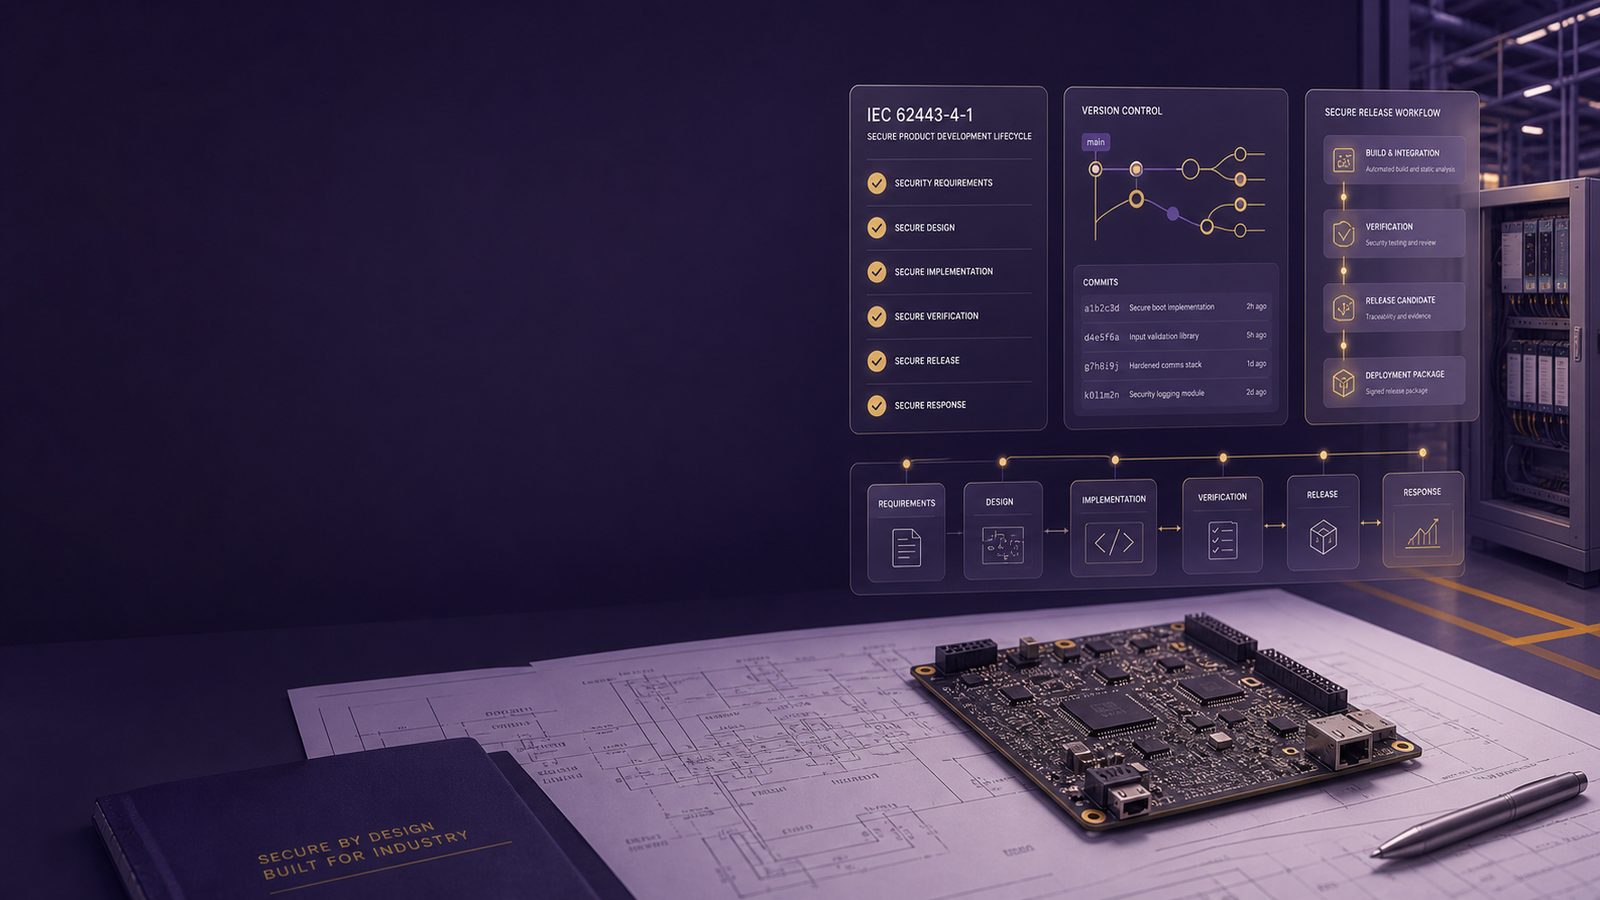
IEC 62443-4-1 secure product development lifecycle for OT vendors
For OT vendors, IEC 62443-4-1 is best understood as a secure product development lifecycle standard. It is[…]