If your business builds software, commissions it, or relies on a digital product to serve customers, security cannot be something you add at the end. Fixing problems late costs more, delays releases, and can damage trust with customers and partners.
The Microsoft Secure Development Lifecycle is a practical way to build security into software from the start. It is not about turning every team into specialists. It is about making sure the right questions are asked early, the most common mistakes are caught before release, and software is maintained with security in mind after it goes live.
For UK SMEs, that matters because the impact of a software issue is usually business-wide. A weak login process, a leaked secret, or a vulnerable third-party component can lead to support calls, lost sales, emergency work, and reputational damage. The good news is that you do not need a large budget or a dedicated security department to make meaningful progress.
Key takeaways
- Start with clear ownership, simple security requirements, and early design review rather than trying to build a perfect process.
- Use code review, testing, and vulnerability tracking to catch issues before release and reduce costly rework.
- Keep security lightweight by adding checks to existing delivery steps and automating repeatable tasks where possible.
- Treat maintenance as part of secure development, including patching, dependency review, and end-of-life planning.
What the Microsoft Secure Development Lifecycle is
In plain English, the Microsoft Secure Development Lifecycle is a set of practices that help teams design, build, test, release, and maintain software more safely. It gives structure to decisions that many small teams already make informally.
Think of it as a checklist for reducing avoidable mistakes. It encourages teams to understand what they are building, what could go wrong, and how to reduce the chance of a security issue reaching customers.
It is also useful to separate this idea from two related terms. Secure coding is about writing safer code. DevSecOps is about building security into the delivery process, so checks happen automatically where possible. The Microsoft Secure Development Lifecycle sits across both. It provides a broader approach that covers planning, design, testing, release, and maintenance.
That makes it especially useful for SMEs that want a simple, repeatable way to improve security without creating a heavy process. If you already use secure design reviews, code review, or automated testing, you are already part of the way there. Articles such as Secure SDLC principles explained for SaaS founders and Secure-by-design principles explained for SMEs cover some of the same ideas from a broader business angle.
Why it matters for UK SMEs
For a small business, the biggest benefit is not abstract security maturity. It is avoiding rework, reducing support burden, and protecting customer confidence.
Security problems found after release are expensive because they interrupt normal work. Developers have to stop planned delivery to investigate and fix the issue. Support teams may need to answer customer queries. Managers may need to explain delays. In some cases, you may need to notify customers, rotate credentials, or rebuild parts of the system.
That is why a lifecycle approach is valuable. It helps you catch issues when they are cheapest to fix, usually before release. It also helps you make better decisions about trade-offs. For example, you may decide that a feature should wait until authentication is designed properly, rather than rushing it out and dealing with the consequences later.
There is also a trust angle. Customers, investors, and larger business partners increasingly want reassurance that software is developed responsibly. You do not need to promise perfection. You do need to show that security is part of how you work. If you buy software from others as well as build it, the same thinking applies to suppliers. A useful companion read is Verifying supplier compliance with secure software requirements.
The main stages of the lifecycle
Planning and requirements
This is where you decide what the software must do and what security expectations apply. For example, if the system handles customer data, payment information, or internal business records, that should shape the design from day one.
Good requirements are specific. Instead of saying, “the system should be secure”, say what that means in practice. For example:
- Users must sign in with strong authentication.
- Only authorised staff can see sensitive records.
- Passwords must never be stored in plain text.
- External input must be checked before use.
- Security issues must be tracked and fixed before release.
This stage is also where you decide who owns security decisions. In a small team, that may be the product lead, engineering lead, or business owner. The key is that someone is responsible for making sure security is not forgotten.
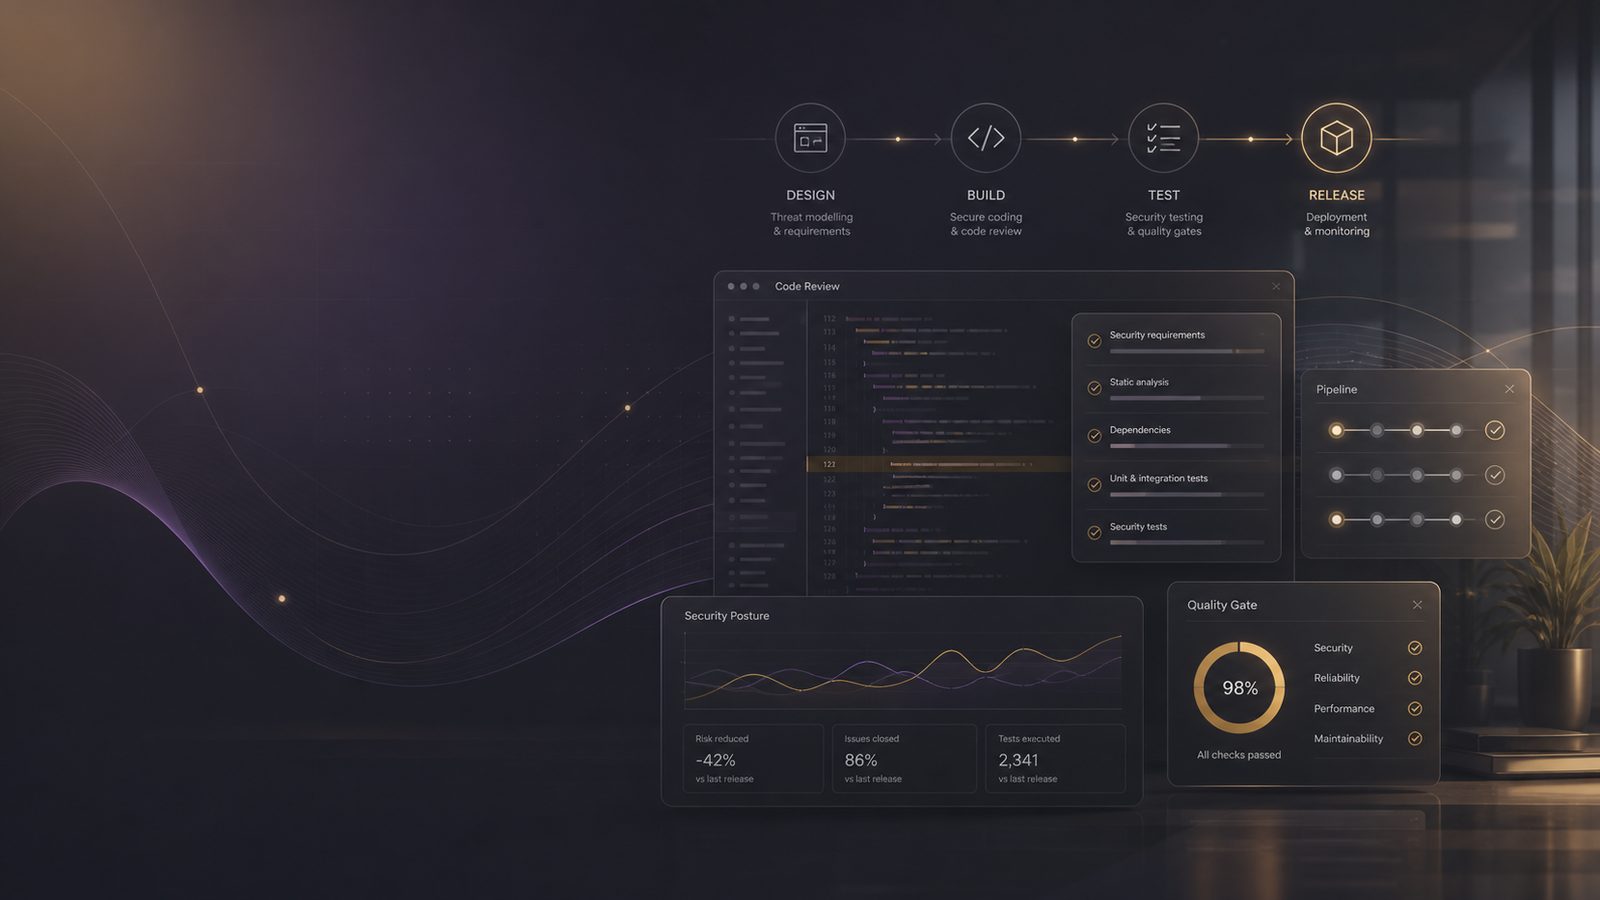
Design, build, test, and release
During design, the team should ask what could go wrong and how the system would behave if something fails. This is where a simple threat review helps. You do not need a formal workshop every time, but you do need a habit of thinking through likely misuse, weak access control, and data exposure.
During build, secure coding standards help developers avoid common errors. That includes checking user input, protecting secrets, using approved libraries, and handling errors safely. A practical reference point is Secure coding principles explained for product teams.
Testing should not be left to the end of the project. It should include checks for the most likely issues, such as broken access control, exposed credentials, and dependency weaknesses. For many SMEs, this means a mix of automated checks and targeted manual testing before release. If you want a more detailed view of the testing side, When and why to commission security testing is a useful companion article.
Operations, maintenance, and retirement
Security does not stop at launch. Once software is live, you need a way to handle vulnerabilities, patch dependencies, review logs, and retire old components safely.
This is where many small businesses lose control. A product may be launched with good intentions, then left to drift. Over time, libraries become outdated, staff change, and nobody is sure who owns patching. That creates avoidable risk.
A lifecycle approach keeps maintenance in scope. It means you know how to respond when a vulnerability is discovered, how quickly you expect fixes to be applied, and what happens when a product reaches end of life. If that is a current concern, see Managing end-of-life software risks for UK SMEs.
How the lifecycle fits into a small team
Many SMEs assume this kind of approach is only realistic for large software companies. In practice, small teams often benefit more because they can make changes quickly.
If you do not have a dedicated security team, start with ownership rather than structure. Decide who is responsible for each part of the process:
- Who approves security requirements?
- Who checks design risks before build starts?
- Who reviews code for security issues?
- Who decides whether a release can go live?
- Who tracks vulnerabilities after release?
Once those responsibilities are clear, keep the process lightweight. Use short checklists, not long documents. Add security checks to existing meetings and release steps rather than creating separate bureaucracy. The aim is to improve decision-making, not slow the business down.
For very small teams, even a simple weekly review of open security issues can make a difference. It helps ensure that vulnerabilities do not sit unnoticed while the team focuses on feature delivery.
Core practices to put in place first
Security requirements and threat modelling
Start by identifying what the software protects and what would matter most if something went wrong. That could be customer data, payment details, internal documents, or access to other systems.
Then ask a few basic questions:
- What happens if someone logs in as the wrong user?
- What happens if an attacker sends unexpected input?
- What happens if a supplier library contains a weakness?
- What happens if a secret key is exposed?
This is often called threat modelling, but you do not need to use the term. The important point is to think ahead before the code is written. If you want a structured starting point, Threat modelling concepts explained for SMEs is a helpful companion.
Secure coding standards and peer review
Every team should have a short set of coding rules that cover the most common risks. Keep them practical. For example, require developers to:
- validate input from users and other systems,
- avoid storing secrets in code,
- use approved authentication and access controls,
- handle errors without exposing sensitive information,
- review changes before they are merged.
Peer review is especially valuable because it catches mistakes that the original developer may miss. It also spreads knowledge across the team, which is useful when people are away or leave the business.
Security testing and vulnerability management
Testing should focus on the issues most likely to affect your business. For many SMEs, that means checking login flows, permissions, third-party components, and exposed configuration.
When issues are found, track them to closure. A vulnerability that is discovered but not fixed is still a business risk. Set a clear process for prioritising and retesting fixes so you know whether the problem has really gone away.
It is also worth having a simple rule for urgent issues. If a serious weakness affects customer data or access to systems, it should be escalated quickly rather than waiting for the next planned release.
How to build security into delivery without slowing teams down
The most common fear is that security will create delay. That can happen if the process is heavy or unclear. It does not have to.
Use checklists at the right points. For example, before a feature is approved, ask whether it changes data handling, access control, or external integrations. Before release, confirm that security tests have run and any high-risk findings are addressed.
Automate repeatable checks wherever possible. Build pipelines can check for common issues such as vulnerable dependencies, exposed secrets, and insecure configuration. Automation is useful because it reduces manual effort and gives the team faster feedback. It also makes security more consistent, which matters when several people are contributing to the same product.
The best approach is usually a blend of automation and human judgement. Automation handles the predictable checks. People handle the business context, such as whether a risk is acceptable for a particular release.
Common risks the lifecycle helps reduce
The Microsoft Secure Development Lifecycle is especially useful for reducing a few recurring problems that affect SMEs.
First, weak authentication and access control. If users can see or change data they should not, the business impact can be serious. That can mean customer complaints, data exposure, or loss of confidence.
Second, injection flaws and unsafe handling of input. If software trusts data it should not trust, attackers may be able to alter behaviour in unexpected ways. Good input handling and output handling reduce that risk. For a deeper explanation, see Input validation, encoding, and output sanitisation techniques for secure software development.
Third, exposed secrets. Passwords, tokens, and keys should not be hard-coded into code or stored in places where many people can access them. If a secret leaks, the impact can spread quickly across systems and services.
Fourth, insecure dependencies. Modern software relies on many third-party libraries and services. If one of those has a weakness, your product may inherit the risk. That is why dependency review and patching need to be part of the lifecycle, not an afterthought.
What good evidence looks like for management and suppliers
Business leaders do not need technical detail on every issue, but they do need evidence that the process is working. Good evidence is simple and practical.
Examples include:
- a short secure development policy,
- records of design or risk reviews,
- code review notes or merge approvals,
- test results from security checks,
- a list of known vulnerabilities and their status,
- patch or release records showing issues were fixed.
If you use suppliers or development partners, ask how they handle these same points. You are looking for signs of a repeatable process, not perfect paperwork. Useful questions include whether they review security early, how they test before release, how they manage vulnerabilities, and how they protect secrets and dependencies.
That kind of evidence is also helpful when you need to reassure customers or larger partners that software is being developed responsibly.
A simple starting checklist for SMEs
If you want to get started in the next 30 days, keep it small and realistic:
- Write down who owns security decisions for each product or system.
- Agree a short list of security requirements for new work.
- Add a basic design review step before development starts.
- Introduce peer review for code changes that affect login, data, or integrations.
- Make sure you have a clear process for fixing and retesting vulnerabilities.
After that, look for one or two automation opportunities. Common examples are dependency scanning, secret detection, and basic security checks in the build process. Do not try to automate everything at once. Start with the checks that save the most time and reduce the most risk.
From there, improve gradually. A lightweight, consistent process is usually more effective than a complex one that nobody follows.
Frequently asked questions
Microsoft Secure Development Lifecycle is not a product you buy or a certificate you apply for. It is a practical set of habits and controls that can be adapted to your business. That makes it suitable for SMEs, SaaS businesses, and product teams of different sizes.
The main value is that it helps you reduce avoidable mistakes, improve release confidence, and show that security is part of how you build software. For many businesses, that is enough to justify the effort on its own.
If you are deciding where to begin, focus on the basics first: clear ownership, simple security requirements, early design review, code review, and a repeatable way to test and fix issues before release. That gives you a solid foundation without creating unnecessary overhead.
If you would like help turning this into a practical process for your team, Speak to a consultant.
Comments are closed