For many UK SMEs, Zero Trust sounds sensible in principle. The business case is straightforward: reduce the chance that one stolen password, one unmanaged laptop, or one over-permissioned account can turn into a costly incident. In practice, though, adoption is often harder than it first appears.
The challenge is not usually the idea itself. It is the reality of small teams, older systems, mixed devices, and limited time. If you try to treat Zero Trust as a single product purchase, you can spend money without reducing risk in a meaningful way. If you treat it as a phased way of tightening access and improving visibility, it becomes much more manageable.
Key takeaways
- Zero Trust is a phased way to reduce business risk, not a single product or a promise of complete protection.
- For most SMEs, the biggest barriers are weak identity controls, limited visibility, older systems, and lack of time.
- Start with the highest-risk accounts and systems, then tighten access and sign-in checks before expanding further.
- Do not buy tools before you understand the problem you are trying to solve and the access rules you want to enforce.
What Zero Trust means for a small business
In plain English, Zero Trust means you do not assume that a person, device, or application should be trusted just because it is inside your network or already signed in. Access is granted only when there is enough confidence that the request is legitimate, and that confidence is checked again when circumstances change.
For an SME, that usually means asking a few simple questions before access is allowed:
- Is this the right person?
- Is this the right device?
- Is this the right level of access for this task?
- Does the request look unusual for this user, location, or time?
This matters because the business impact of weak access controls is often bigger than the technical issue itself. A compromised account can lead to lost sales, downtime, customer concern, recovery costs, and management time spent dealing with the aftermath. For a smaller business, even a short disruption can affect cash flow and reputation.
Zero Trust is best understood as a risk reduction model, not a promise that nothing will ever go wrong. It helps you limit the damage when something does go wrong, which is often the more realistic goal for an SME.
Why SMEs struggle to adopt Zero Trust
The most common adoption challenges are practical rather than theoretical. SMEs usually know they need stronger controls, but they have to work within real constraints.
Limited budget, time, and internal skills
Many smaller businesses do not have a dedicated security team. The same person may be responsible for user support, device management, supplier issues, and day-to-day firefighting. That makes it difficult to design, test, and roll out changes carefully.
Budget is another factor. Zero Trust often requires improvements in identity controls, device management, logging, and access policies. Those are worthwhile investments, but they compete with other priorities such as replacing ageing equipment, supporting growth, or keeping core systems running.
The result is often delay. Leaders know the current setup is not ideal, but they wait for a “better time” that never arrives. A better approach is to start with the highest-risk areas and make steady progress.
Older systems, mixed devices, and remote working
SMEs are rarely starting from a clean slate. They may have older business applications, shared folders, remote desktop access, personal devices, and cloud services all in the same environment. That mix makes it harder to apply consistent rules.
Older systems can be especially awkward. Some cannot support modern sign-in checks or device checks. Others rely on broad network access that was acceptable years ago but is now too generous. If you try to force every system into the same model, you may create disruption without improving security.
Remote and hybrid working adds another layer. Staff may work from home, customer sites, or while travelling. That means access decisions need to be based more on identity, device health, and context than on location alone.
The most common implementation blockers
When SMEs begin to put Zero Trust into practice, two issues tend to cause the most friction: identity and visibility.
Identity and access gaps
Identity is the foundation of Zero Trust. If you cannot reliably tell who is accessing what, you cannot make sensible access decisions.
Common gaps include:
- Shared user accounts
- Too many administrator accounts
- Weak password practices
- Accounts that remain active after staff leave
- Access rights that have grown over time and were never reviewed
These are not just technical housekeeping issues. They create business risk because they make misuse easier and investigations harder. If several people use the same account, you lose accountability. If former staff still have access, you increase the chance of unauthorised entry. If administrators have broad access everywhere, one mistake can have a much wider impact.
A practical Zero Trust approach starts by tightening identity controls before moving on to more advanced ideas. That usually means stronger sign-in checks, removing shared accounts, reviewing privileged access, and making sure leavers are removed promptly.
If you are already thinking about access design, it may help to review our article on designing least privilege access using IAM and RBAC, which explains how to reduce unnecessary access in a structured way.
Poor visibility across users, devices, and data
Zero Trust depends on knowing what is happening. If you cannot see which devices are managed, which accounts are privileged, or which systems hold sensitive data, it becomes difficult to prioritise controls.
Many SMEs have visibility in fragments. One tool shows sign-ins, another shows endpoint status, another shows firewall events, and a spreadsheet somewhere else lists critical systems. That makes it hard to answer simple questions such as:
- Which accounts can access our most important data?
- Which devices are missing updates?
- Which systems are exposed to the internet?
- What would happen if a key account were compromised?
Without that view, Zero Trust can turn into guesswork. You may add controls in the wrong place while leaving the real weak points untouched.
That is why central visibility is often a better first investment than more tools. If you want a broader view of this issue, our article on centralised security visibility explained for SMEs is a useful companion piece.
How to prioritise the first changes
The best way to start is to focus on the areas that would cause the most damage if they were misused. For most SMEs, that means privileged accounts, email, finance systems, customer data, and remote access.
Start with the highest-risk accounts and systems
Begin by identifying the accounts that matter most. These usually include administrators, finance staff, directors, and anyone with access to customer or employee data. Then look at the systems those accounts use every day.
Ask what would happen if one of those accounts were taken over. Could an attacker approve payments, change bank details, access confidential records, or send convincing internal emails? If the answer is yes, that area should be near the top of your list.
From there, apply the simplest controls first:
- Require stronger sign-in checks for important accounts
- Remove shared accounts where possible
- Limit administrator access to the tasks that genuinely need it
- Make sure devices used for sensitive work are managed and updated
- Review access for leavers and role changes promptly
These steps do not require a complete redesign. They reduce exposure quickly and create a better base for later improvements.
Focus on quick wins that reduce exposure
Quick wins are useful when they are chosen carefully. The aim is not to tick boxes. It is to reduce the chance of a serious business problem.
Good early wins often include:
- Turning on stronger sign-in checks for remote access and important accounts
- Blocking access from unmanaged devices to sensitive systems
- Separating administrator accounts from everyday user accounts
- Reviewing who can access finance, payroll, and customer records
- Removing old accounts and unused access rights
These changes are usually more valuable than buying a new security product before the basics are in place.
What a practical Zero Trust roadmap looks like
A workable roadmap for an SME should be phased, realistic, and tied to business priorities. It should also recognise that people and process matter as much as technology.
People, process, and technology in the right order
Start with business decisions. Decide which information, systems, and accounts matter most. Then define the rules for access. Only after that should you configure tools to enforce those rules.
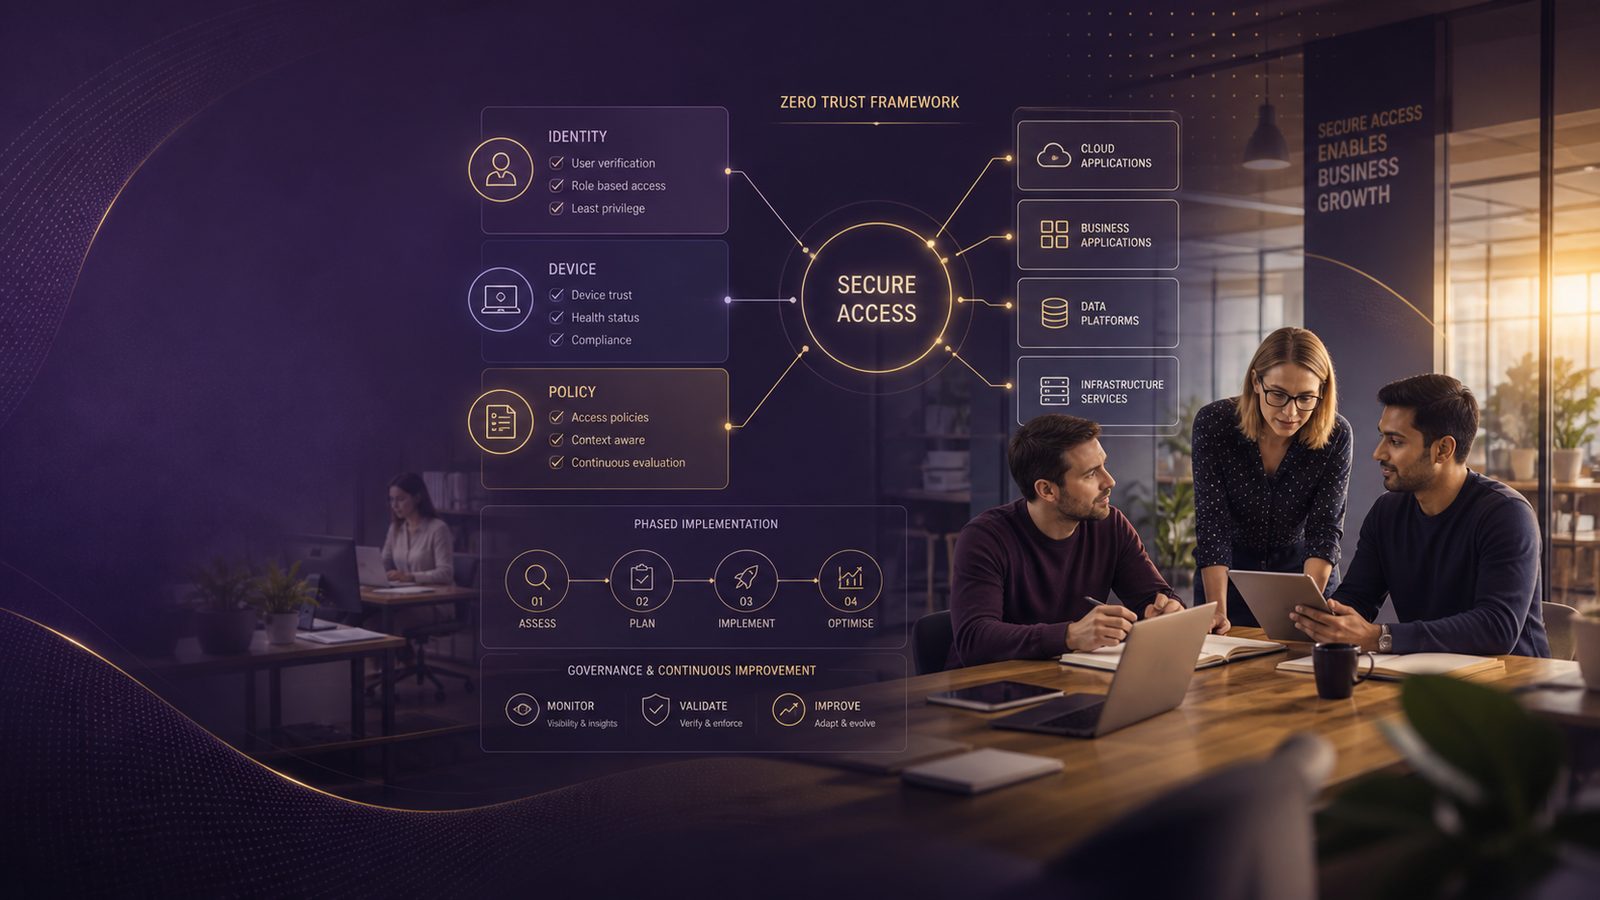
A sensible sequence is:
- Identify your most important systems and data
- List the accounts that can reach them
- Remove unnecessary access
- Strengthen sign-in checks for higher-risk access
- Make sure devices are known and managed
- Improve logging so you can spot unusual activity
- Test the changes with a small group before wider rollout
This order matters because tools cannot fix unclear ownership or poor access decisions. If nobody knows who should have access, automation will simply enforce confusion more quickly.
For organisations that want to align security work with wider design decisions, our article on aligning security architecture to business objectives for UK SMEs explains how to keep security changes tied to business outcomes.
How to phase work without disrupting the business
SMEs often worry that stronger controls will slow staff down. That risk is real if changes are rushed or poorly explained. The answer is to phase the work and communicate clearly.
Start with a pilot group, such as one department or one high-risk system. Check that the new controls work in practice. Look for friction points such as repeated sign-ins, blocked access to legitimate tools, or unclear approval steps. Then adjust before expanding.
It also helps to explain the reason for the change in business terms. Staff are more likely to accept a new sign-in step if they understand it protects payroll, customer records, or the company’s ability to keep trading.
How to avoid common mistakes
Two mistakes come up repeatedly.
Do not try to replace everything at once
Some businesses decide to “do Zero Trust” by changing every system, policy, and device at the same time. That usually creates confusion, support issues, and resistance from staff.
It is better to improve one area at a time. Focus on the highest-risk accounts and systems first, then expand once the new approach is stable. Small, well-managed steps are more likely to stick than a large programme that never finishes.
Do not treat tools as a strategy
Buying a product is not the same as improving security. A tool can help enforce decisions, but it cannot decide what matters most or what level of risk the business is willing to accept.
Before buying anything new, ask what problem you are trying to solve. Is it weak sign-in controls, poor device management, lack of visibility, or excessive access rights? If you cannot name the problem clearly, you are not ready to choose the tool.
This is where a simple architecture review can save money. If you want a structured way to spot weak points, our article on identifying bottlenecks and single points of failure in security architecture is a useful reference.
How Zero Trust supports wider security goals
Zero Trust is not a separate project sitting on top of everything else. It supports broader goals such as reducing account misuse, limiting the spread of an incident, and making recovery easier.
If an attacker gets hold of one account, stronger access controls can stop them moving freely through the business. If a device is compromised, device checks can limit what it can reach. If a user behaves unusually, better logging can help you spot it sooner.
That makes incident response more effective. Instead of trying to understand everything at once, you can focus on a smaller area of impact. It also helps with recovery because fewer systems should be affected if access is properly limited.
For businesses thinking about the wider operating model, our article on operational security architecture for long-term sustainability explores how to make security manageable over time rather than as a one-off project.
A simple checklist for SME leaders
If you are speaking to your IT provider or security adviser, these are sensible questions to ask:
- Which accounts have the most power in our environment?
- Do we know which devices are managed and which are not?
- Are there any shared accounts we should remove?
- Can we restrict access to sensitive systems from unmanaged devices?
- Do we have enough logging to investigate unusual access?
- Which changes would reduce risk fastest without disrupting the business?
You are ready for the next step when you can answer those questions clearly and you have a short list of priority systems, accounts, and devices. At that point, Zero Trust becomes a practical programme rather than a vague ambition.
If you want help turning that into a realistic plan, we can support with risk-based security architecture advice and implementation guidance tailored to UK SMEs. A short conversation is often enough to identify the first few changes that will make the biggest difference.
Frequently asked questions
Is Zero Trust realistic for a small business?
Yes, provided it is treated as a phased approach rather than a big-bang transformation. Most SMEs can make meaningful progress by tightening access to key accounts, improving device control, and increasing visibility before moving on to more advanced changes.
What should an SME do first when adopting Zero Trust?
Start with your most important accounts and systems. In practice, that usually means administrators, finance access, email, and customer data. Remove unnecessary access, strengthen sign-in checks, and make sure you can see what is happening before expanding further.
Will Zero Trust stop all cyber incidents?
No. It reduces the chance that a single compromise becomes a major business problem. It is one part of a wider security approach that should also include backups, monitoring, staff awareness, and incident response planning.
Do we need new tools to begin?
Not always. Many SMEs can make useful progress by improving how existing tools are configured and by removing unnecessary access. New tools may help later, but they should support a clear plan rather than replace one.
How do we avoid disrupting staff?
Roll changes out in stages, starting with a pilot group or a high-risk system. Explain why the change matters in business terms, test it carefully, and adjust before wider rollout.
Comments are closed