Clear Path Security
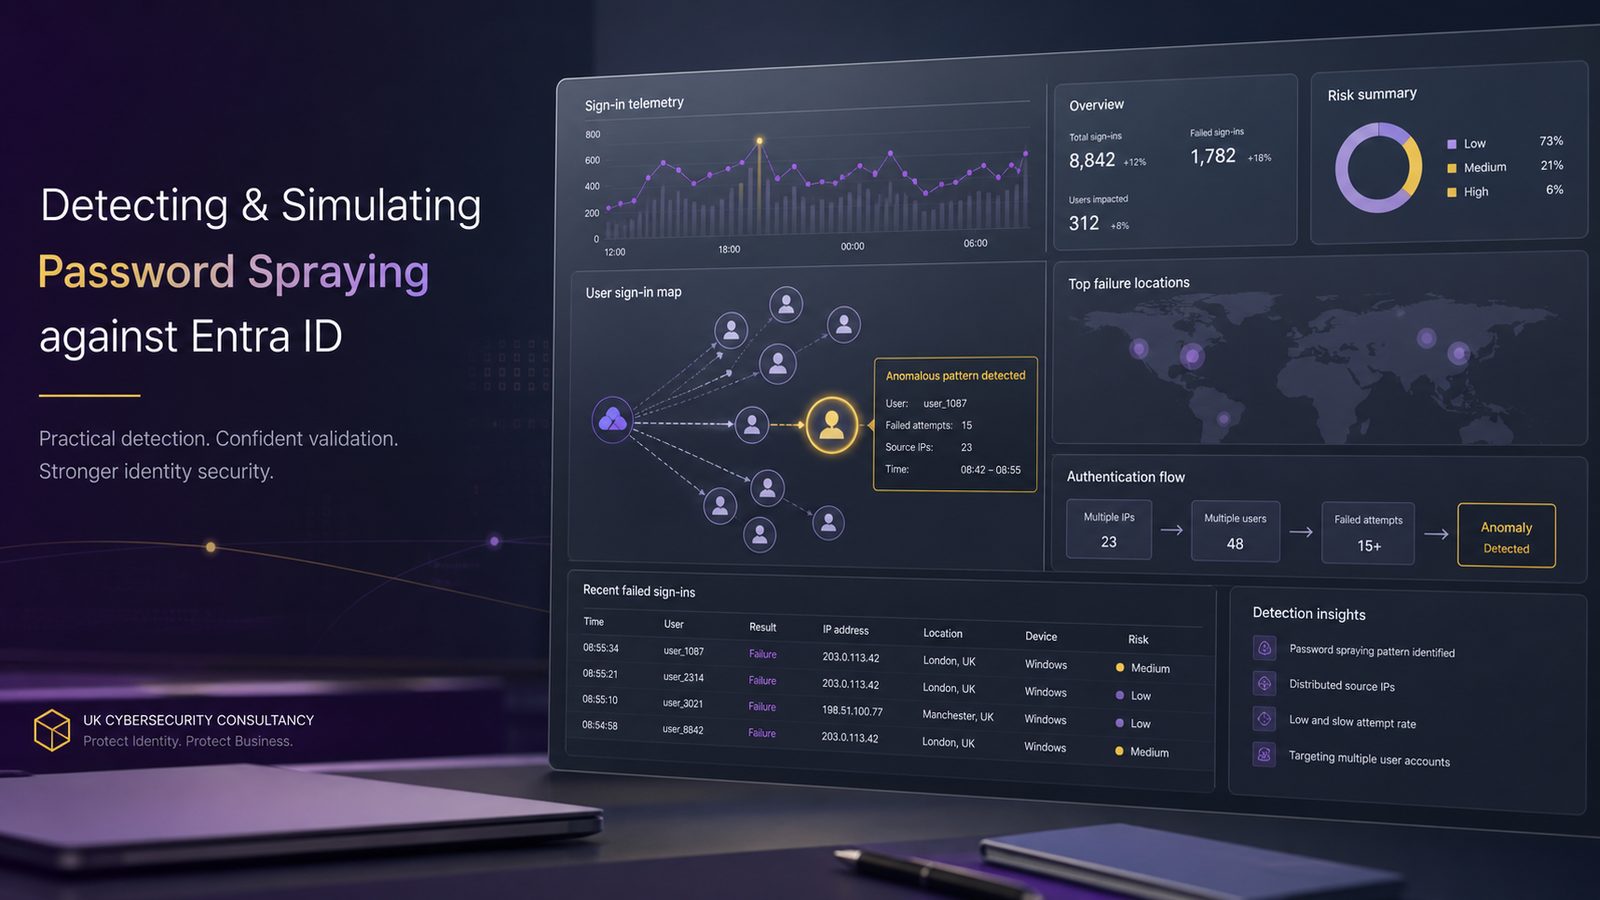
Detecting and simulating password spraying against Entra ID
Password spraying against Entra ID remains one of the more practical identity attack patterns to defend against[…]
Detecting living-off-the-land binaries with Sysmon process events
Living-off-the-land binaries, often shortened to LOLBins, are legitimate Windows executables that attackers abuse to carry out malicious[…]
Secure AI development explained for business leaders
Secure AI development explained for business leaders AI can save time, improve service, and help small businesses[…]
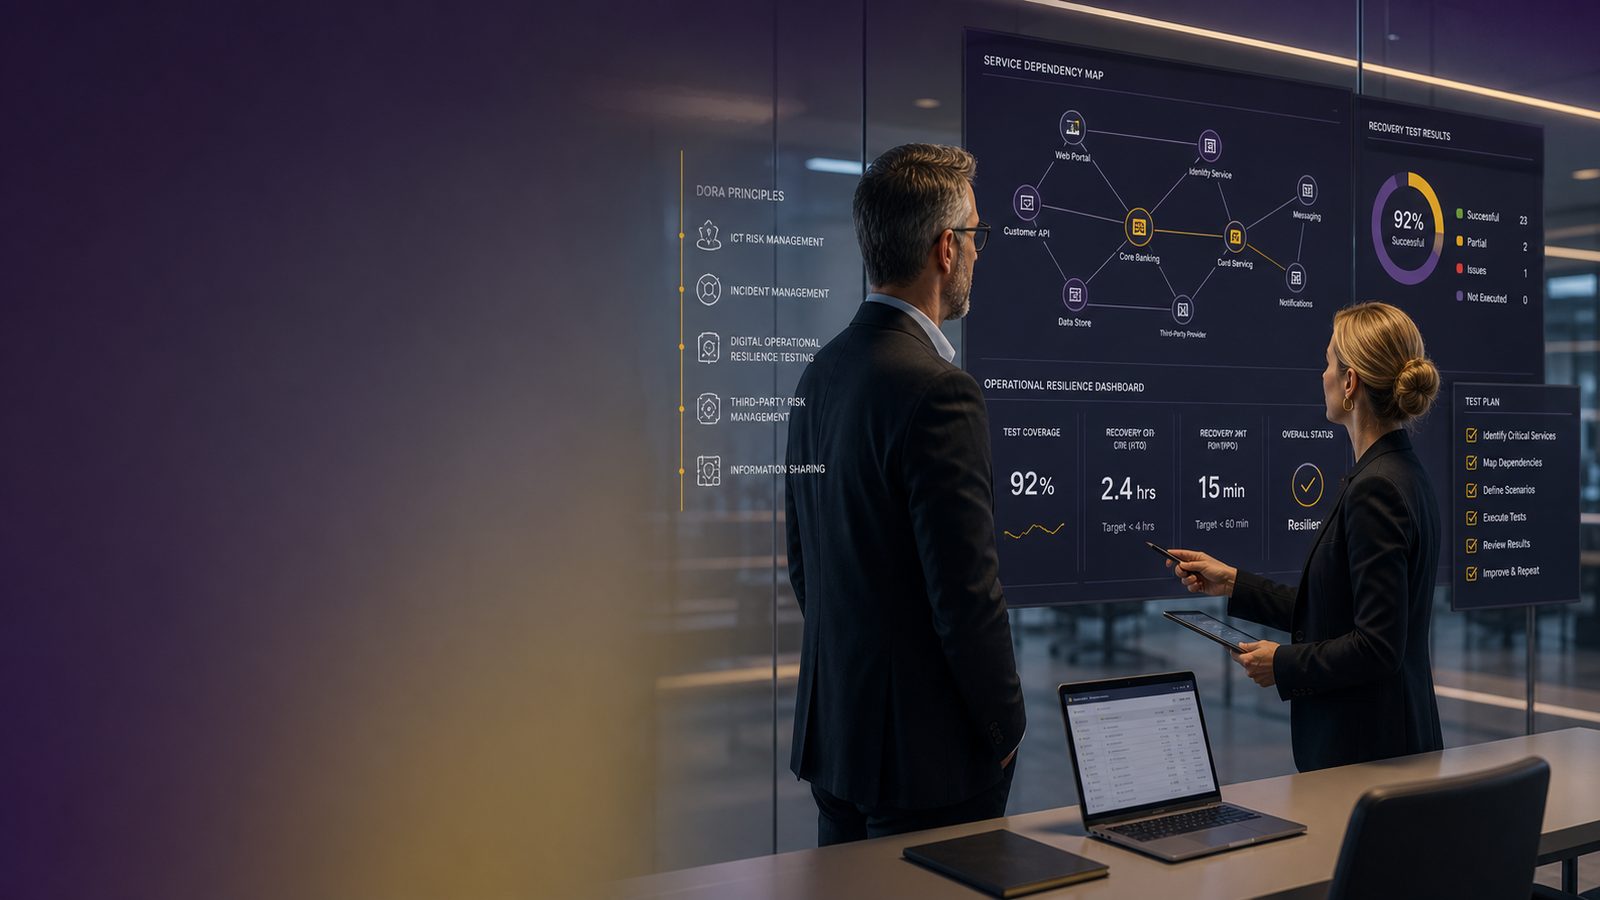
Operational resilience testing under DORA
Key takeaways Operational resilience testing under DORA should prove that critical services can continue or recover under[…]
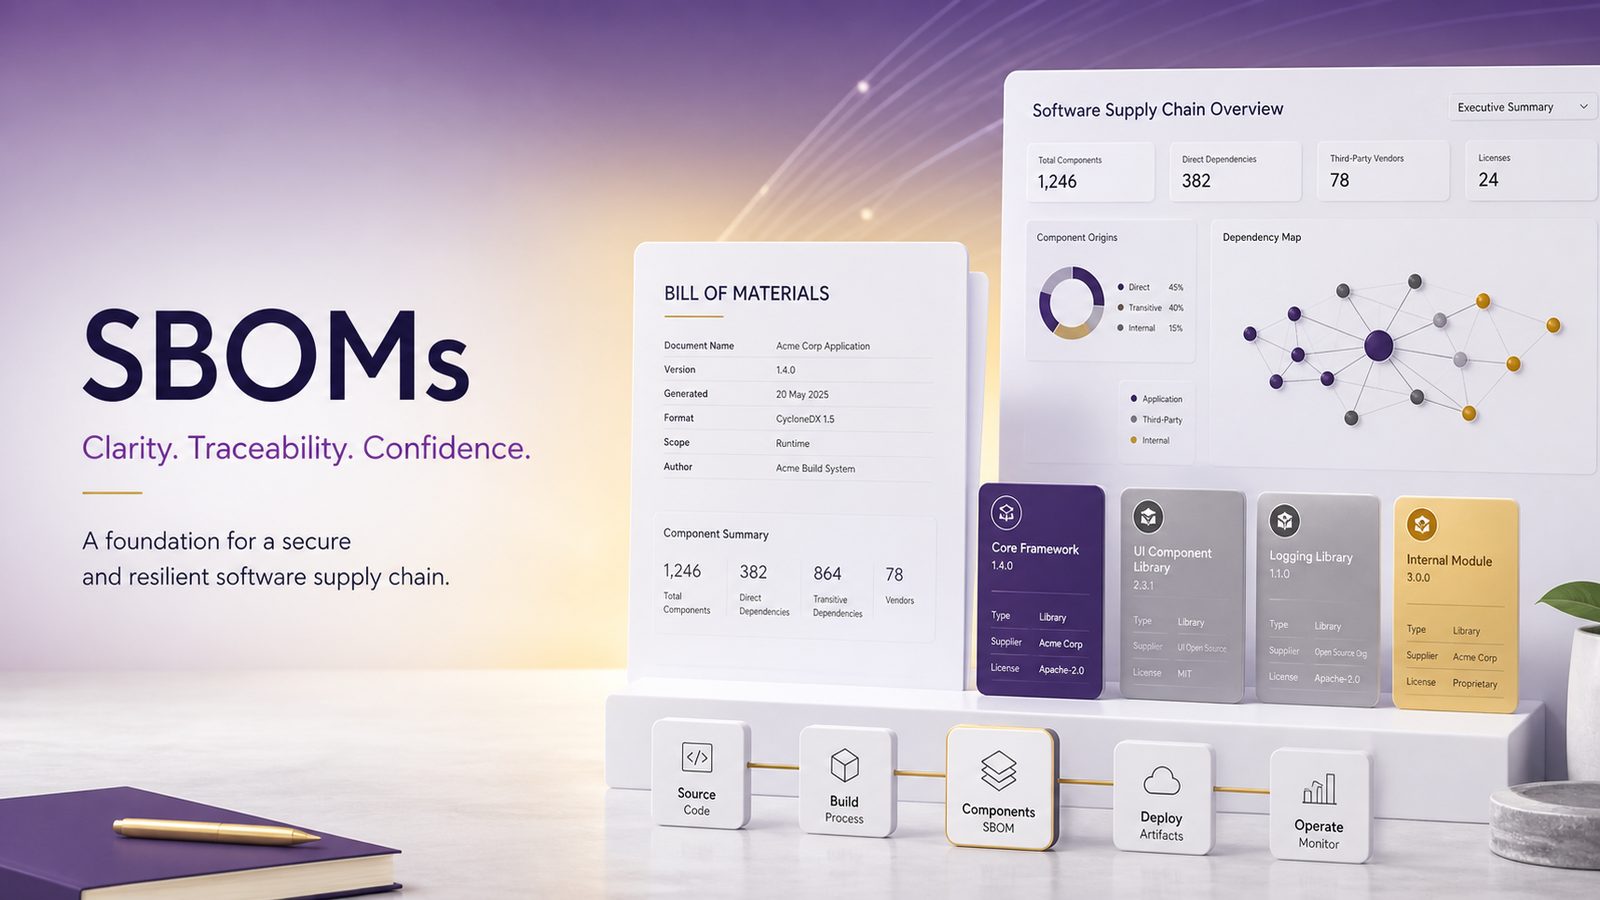
SBOMs explained for non-technical stakeholders
Key takeaways An SBOM is a clear list of what is inside a software product, including its[…]

Testing systems for high load and denial-of-service conditions
Testing systems for high load and denial-of-service conditions is one of the most practical ways to understand[…]
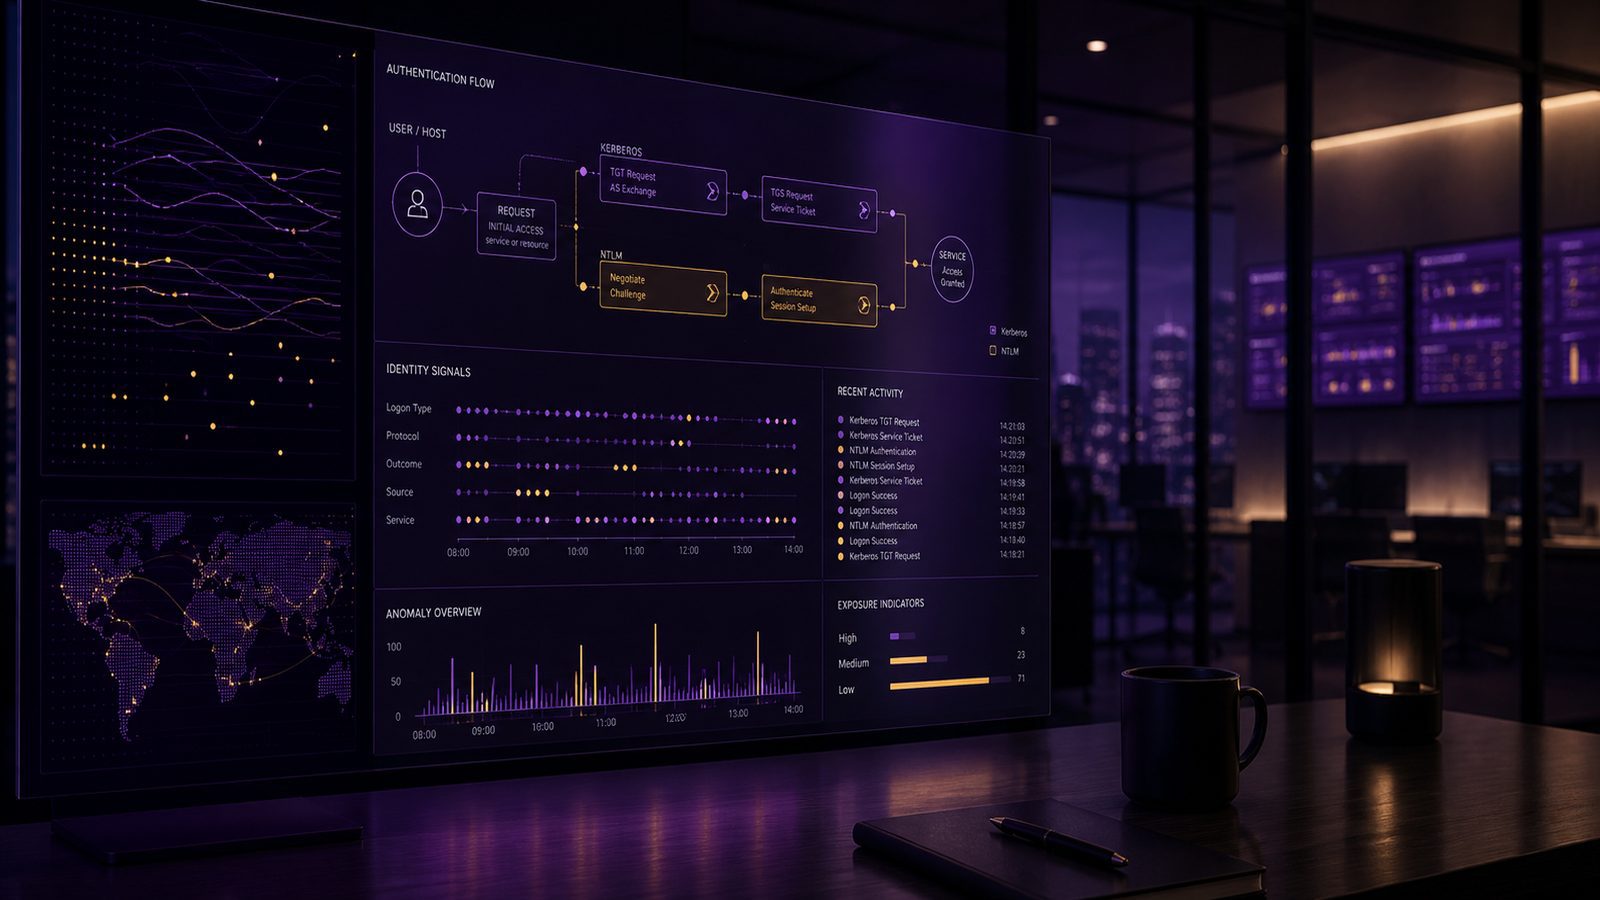
Detecting Kerberos and NTLM abuse in enterprise environments
Kerberos and NTLM are still central to identity security in many enterprise environments, especially where Active Directory[…]
Business risks of denial-of-service attacks explained
A denial-of-service attack is a deliberate attempt to make an online service unavailable. For a small or[…]
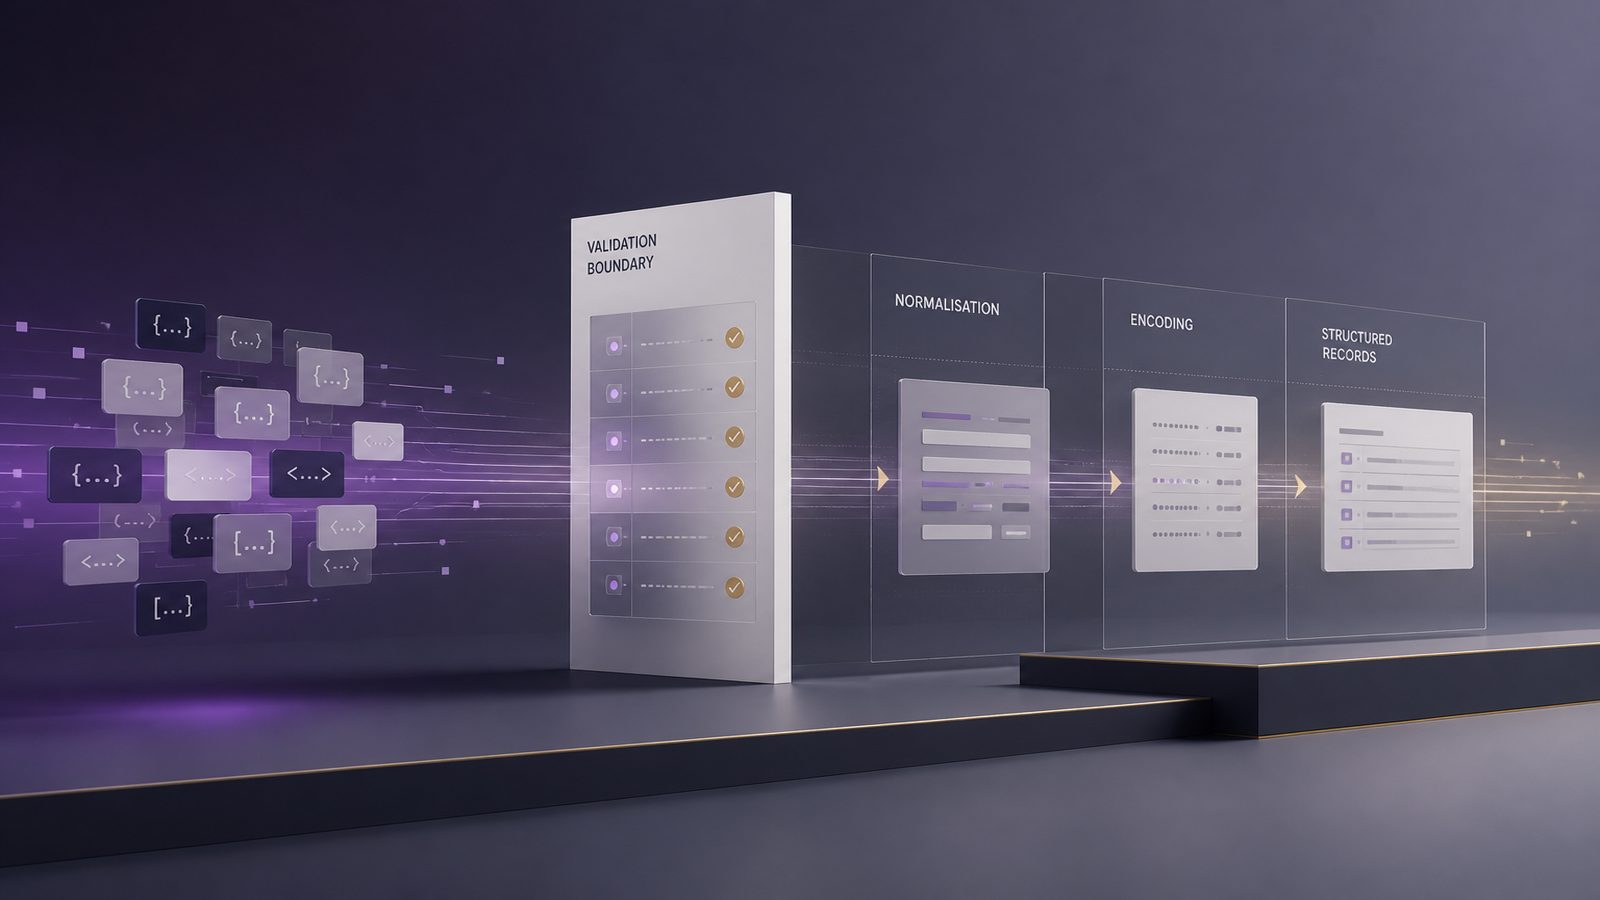
External input cannot be trusted: input validation and encoding strategies
External data should be treated as hostile until it has been checked, constrained, and transformed for the[…]
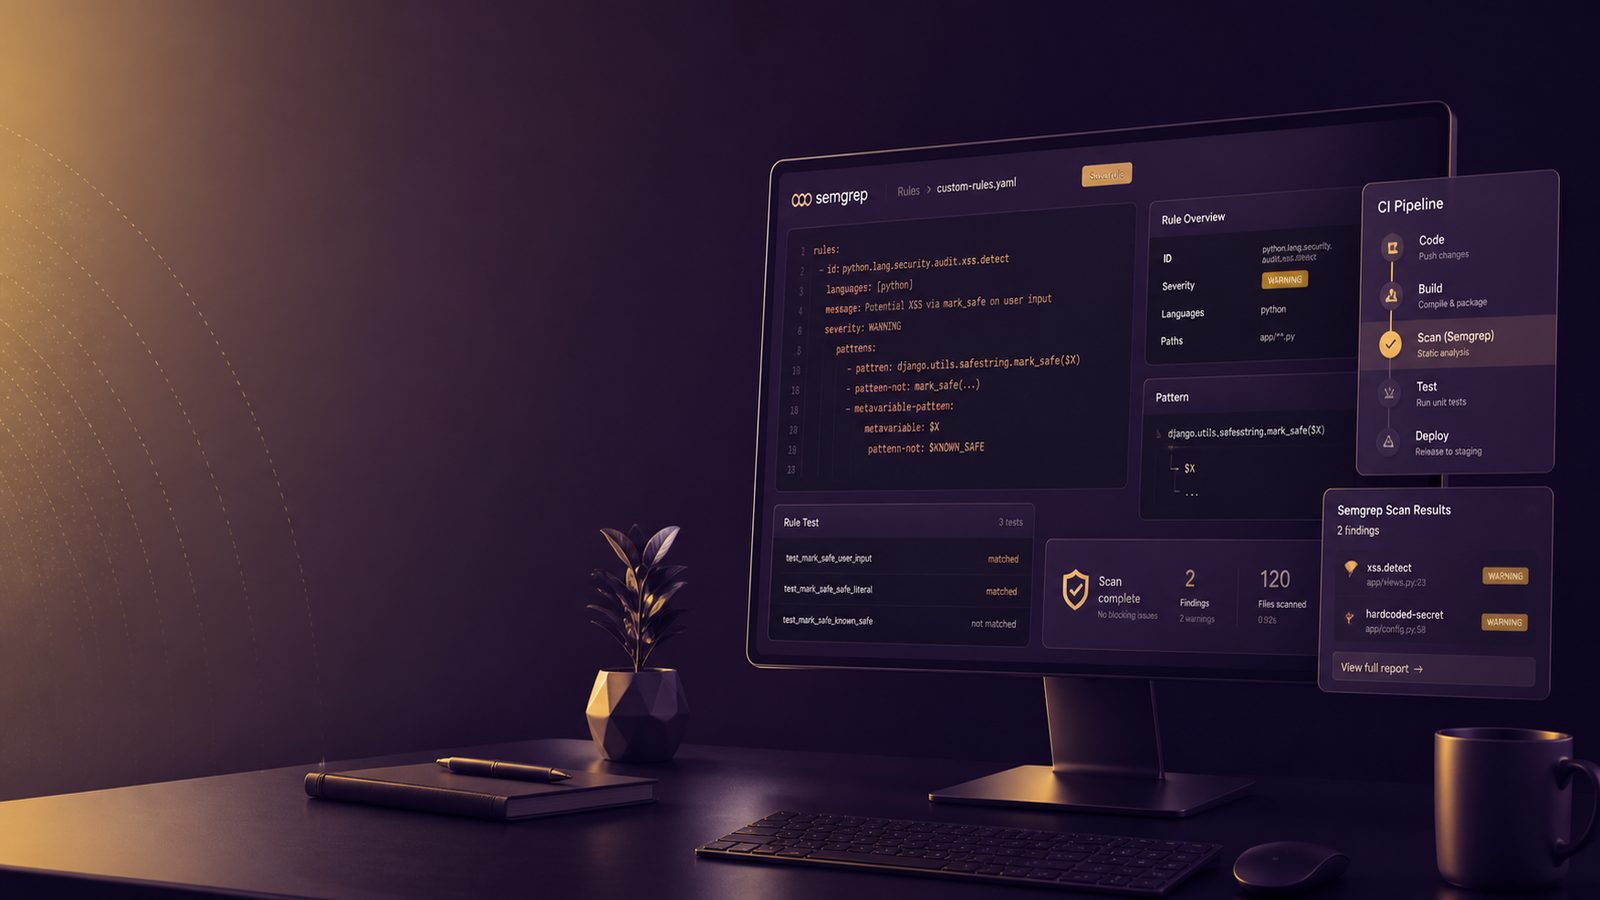
Writing custom SAST rules with Semgrep
Static application security testing, or SAST, is most useful when it is close to the way your[…]