Key takeaways
- Keep the scope narrow and tied to the real SaaS service, not every possible system in the business.
- Collect evidence from everyday work, such as access reviews, change approvals and incident records.
- Start with the controls that affect customer trust most directly, including access, backups, suppliers and secure development.
- Use existing tools and routines so the management system stays practical for a small team.
What ISO 27001 means for a SaaS start-up
For a SaaS start-up, ISO 27001 is less about paperwork and more about proving that you manage information security in a sensible, repeatable way. In business terms, it helps you reduce the chance of avoidable incidents, protect customer trust and make sales conversations easier when prospects ask how you handle security.
It is also a useful way to show that security is not an afterthought. Many growing software businesses reach a point where larger customers, investors or procurement teams want reassurance before they sign a contract. ISO 27001 can help you answer those questions with structure rather than ad hoc promises.
That said, it is important to be clear about what it can and cannot do. It does not make a business secure by itself, and it does not guarantee certification or compliance. What it does is give you a framework for deciding what matters, recording the risks, putting controls in place and showing that those controls are being used.
If you are already thinking about how to keep the work manageable, it can help to start with a clear boundary around the business service you are trying to protect. A narrow, well-justified approach is usually better than trying to cover every tool, team and experiment on day one. Our guide on ISMS scope definition for small organisations covers the wider scoping principles in more detail.
Why customers ask for it
Customers ask for ISO 27001 because they want confidence that your business can handle their data responsibly and keep services available. For a SaaS company, that often translates into questions about access control, backups, incident response, supplier management and how you build and release software.
From a commercial point of view, the standard can reduce friction in procurement. It may not close a deal on its own, but it can remove a common objection and shorten the time spent answering repeated security questionnaires. For a small team, that can save real sales and operations effort.
It can also help you grow more cleanly. Start-ups often build quickly, then discover that security practices are scattered across people and tools. A structured management system gives you a way to keep pace with growth without relying on memory or heroics.
What it can and cannot do for your business
ISO 27001 can help you organise security work, assign responsibility and keep evidence in one place. It can make it easier to spot gaps, prioritise fixes and explain your approach to customers, partners and investors.
It cannot replace good judgement. If your product handles sensitive customer data, you still need to make practical decisions about access, logging, development practices and supplier risk. The standard supports those decisions, but it does not make them for you.
It also should not be treated as a one-off project. The value comes from using it as part of normal business operations, so that security decisions are reviewed, recorded and improved over time.
How to define a sensible scope
Scope is one of the most important decisions a SaaS start-up will make. If the scope is too broad, the work becomes slow and expensive. If it is too narrow or artificial, it may not reflect how the business actually operates and can create problems later when customers ask awkward questions.
The best scope is usually the smallest practical part of the business that still covers the real service you sell. That means the people, systems, cloud services and processes that directly support the SaaS product, plus any supporting functions that can affect its security.
What to include in scope for a small SaaS business
For most start-ups, scope should include the product itself, the cloud environment it runs in, the source code repositories, the systems used to build and deploy the software, and the people who administer or support those systems. If customer data is processed, the environment that stores or transmits that data should also be included.
You should also include the key business processes that affect security, such as onboarding staff, granting access, handling incidents, approving changes and managing suppliers. These are often overlooked because they do not feel like “technical” systems, but they are central to how the business is actually run.
Think about the service from the customer’s point of view. If a customer buys your SaaS platform, what parts of your organisation must work properly for that service to be safe and reliable? Those parts are usually the right starting point for scope.
What to leave out at first so the project stays manageable
It is often sensible to leave out areas that are not yet part of the core service, such as experimental products, unrelated internal tools or office systems that do not affect the SaaS platform. You can add them later if the business grows or if there is a clear reason to expand.
Do not include every possible future service “just in case”. That creates unnecessary work and makes evidence collection harder. A focused scope is easier to explain, easier to maintain and more likely to stay accurate as the business changes.
Be careful not to draw the boundary so tightly that it ignores shared services. For example, if the same team manages production and development access, or if the same cloud account supports multiple parts of the service, those dependencies need to be understood and documented.
The core evidence you will need
Evidence is where many start-ups underestimate the effort. The goal is not to create a folder full of documents. The goal is to show that your security controls exist, are understood and are being used in day-to-day work.
Good evidence is usually a mix of written records and operational proof. Written records explain what you intend to do. Operational proof shows that the business is actually doing it.
Policies, risk records and asset lists
At a minimum, you will need clear policies that explain how the business handles security, access, incidents, suppliers and change. These do not need to be long, but they do need to be current, approved and used by the team.
You will also need a risk record that shows the main information security risks to the business, what you decided to do about them and who owns each action. For a SaaS start-up, this should reflect the real service, not a generic template copied from somewhere else.
An asset list is another basic building block. This should cover the systems, services and information that matter most, such as production environments, code repositories, admin accounts, customer data stores and backup locations. If you do not know what you have, it is difficult to protect it properly.
Where useful, link these records together. For example, a risk about unauthorised access should connect to the systems and accounts that could be affected, and to the controls you use to reduce that risk. That makes the evidence easier to understand and easier to maintain.
Operational evidence from everyday SaaS work
The strongest evidence usually comes from normal business activity. Meeting notes, change approvals, access reviews, incident tickets, onboarding checklists and backup checks all help show that the system is working in practice.
For example, if you say that access is reviewed regularly, keep the review record. If you say that changes are approved before release, keep the approval trail. If you say that incidents are logged and investigated, keep the incident record and the follow-up actions.
This is where many small teams can save time by using the records they already create. A ticketing system, a shared document register or a project tool can often hold much of the evidence you need, provided the process is consistent and the records are easy to find.
If you want to reduce manual effort, it is worth looking at automating ISO 27001 evidence collection using GRC tools. Even simple automation can reduce the risk of missing evidence at the wrong time.
Evidence SaaS teams often overlook
Some of the most useful evidence is also the easiest to forget. That is because it sits in everyday operational work rather than in a formal policy document.
Access control, supplier management and change records
Access control evidence should show who has access, why they have it and when it was last reviewed. For a SaaS company, this is especially important for administrator accounts, cloud consoles, source code repositories and customer support tools.
Supplier management is another common gap. If your business relies on cloud hosting, payment services, monitoring tools or outsourced development, you should keep a record of those suppliers and the checks you have made on them. You do not need to overcomplicate this, but you do need to show that supplier risk is being considered.
Change records matter because start-ups move quickly. If releases are frequent, you need a simple way to show what changed, who approved it and whether anything went wrong. A lightweight release log can be enough if it is used consistently.
Backups, incident handling and secure development evidence
Backups are only useful if you can show they are being checked and, where appropriate, tested. Evidence might include backup job reports, restore test results and notes from any issues found.
Incident handling evidence should show that staff know how to report a problem, that incidents are logged, and that lessons are captured afterwards. This does not need to be elaborate. A short incident record with actions and owners is often enough to demonstrate control.
Secure development evidence is particularly important for SaaS businesses. That can include code review records, vulnerability scanning results, release approvals and notes from security checks before deployment. If your team wants a practical starting point, our article on secure development principles for SaaS founders is a useful companion.
A realistic timeline for a start-up team
Timelines vary depending on the size of the team, the maturity of existing controls and how much evidence already exists. A small SaaS business with some structure in place can move faster than a team starting from scratch, but it is still wise to plan in stages.
The main mistake is assuming the work is only about writing documents. In practice, the time is often spent clarifying ownership, cleaning up access, improving records and making sure the evidence reflects reality.
What can be done in the first 30, 60 and 90 days
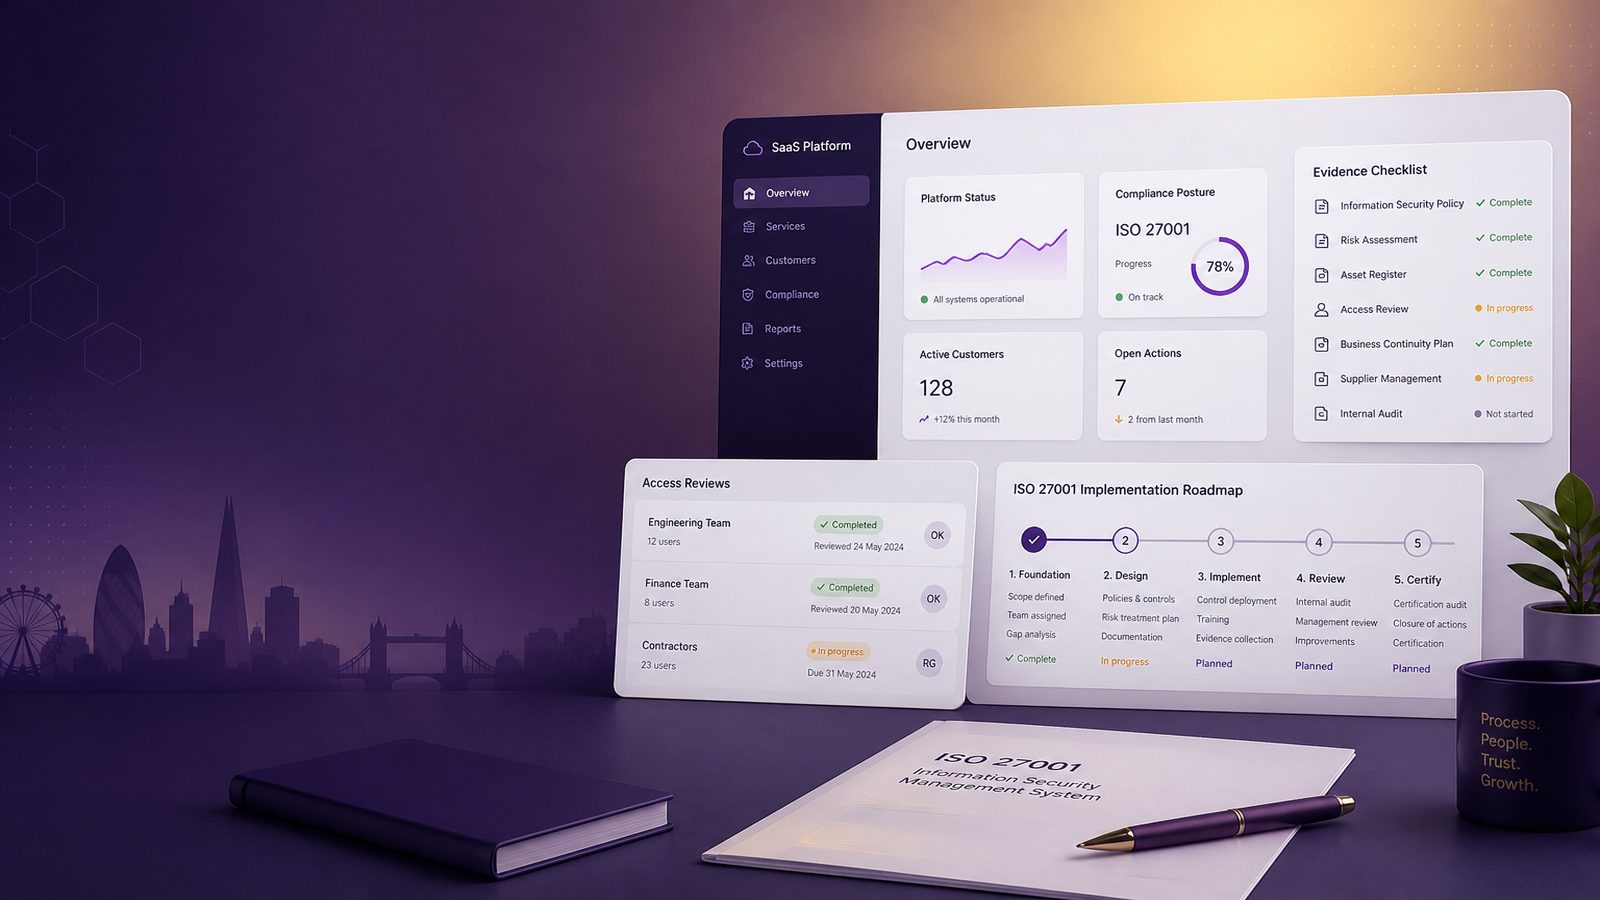
In the first 30 days, focus on scope, ownership and a basic gap review. Decide what is in scope, identify the main risks, list the key assets and agree who is responsible for each area. This gives the project shape and stops it drifting.
By 60 days, you should have the core policies in place, a first version of the risk record, and a simple evidence structure. At this stage, you should also begin collecting operational proof from normal work, rather than waiting until the end.
By 90 days, many start-ups can have a workable management system in place if they stay disciplined. That does not mean everything is perfect. It means the main controls are defined, used and evidenced, and the remaining gaps are understood.
What usually takes longer than founders expect
Three areas often take longer than expected. First, getting consistent ownership across a busy team can be difficult. Second, cleaning up access and supplier records can take time if the business has grown quickly. Third, building a reliable evidence habit usually takes longer than writing the first draft of a policy.
Another common delay is change management. Start-ups often release frequently, which is good for product delivery but can make evidence messy if there is no simple approval trail. A lightweight process is usually better than no process at all.
If you are already struggling to keep the work practical, a short external review can help you avoid rework. The aim is not to add bureaucracy, but to make sure the scope, evidence and timeline all fit the way the business actually operates.
Common scope and evidence mistakes
Most problems fall into a small number of patterns. The good news is that they are avoidable if you know what to look for early.
Trying to cover too much too soon
The first mistake is trying to include every system, team and future idea in the initial scope. That usually creates delay and frustration. Start with the service you actually sell, then expand only when there is a clear business reason.
The second mistake is treating the project as a separate security exercise rather than part of the business. If the work sits outside normal operations, it becomes hard to maintain. The more you can embed it into existing routines, the better.
Collecting documents without proving they are used
The other common mistake is building a neat set of documents that nobody follows. A policy that is never used does not help much. A process that is used but never recorded can also cause problems.
You need both sides: a clear description of what should happen and evidence that it actually does happen. That is why meeting notes, tickets, approvals and review records are so valuable. They show the management system is alive, not just written down.
If you are unsure whether your evidence is strong enough, compare it against the way the business really works. If the record does not match reality, fix the process or the document before you go any further.
How to keep the work practical for a small team
For a start-up, the best approach is usually simple, consistent and low overhead. You do not need a large compliance function to make progress. You need clear ownership, sensible routines and a way to keep records organised.
Using existing tools and routines
Use the tools your team already relies on. A ticketing system can hold change and incident records. A shared drive or document tool can store policies and risk records. A spreadsheet may be enough for an initial asset list and evidence tracker.
The key is consistency. Pick one place for each type of record and make sure everyone knows where it is. If evidence is scattered across inboxes and chat messages, it will be difficult to maintain and even harder to find later.
Where possible, build evidence into routine work. For example, if a release needs approval, make that approval part of the release process. If access is reviewed monthly, schedule the review and keep the result in the same place each time.
Assigning ownership without creating bureaucracy
Ownership should be clear, but it does not need to be heavy. One person can own the risk record, another can own access reviews, and another can own supplier checks. The important thing is that each area has a named owner and a review cycle.
Keep meetings short and focused. A monthly security review can be enough for a small team if it covers the main actions, open risks and evidence gaps. The point is to keep the system moving, not to create a standing committee for its own sake.
For businesses that want a broader view of how to balance effort and value, our article on ISO 27001:2022 versus Cyber Essentials Plus can help frame the trade-offs.
When to ask for outside help
Outside help is worth considering when the work starts slowing product delivery, when the team is unsure how to scope the system, or when evidence is being collected in a way that will be hard to defend later. A short advisory engagement can often save time by helping you focus on the right things first.
It can also help where the business has grown quickly and the current controls are uneven. In that situation, an experienced consultant can help you turn existing practice into a clearer, more manageable system without forcing a one-size-fits-all model onto the company.
Advisory support is most useful when it is practical and risk-based. The aim should be to help you build something that fits the business, not to create unnecessary process for its own sake.
If you would like a sense check on scope, evidence or timeline planning, Speak to a consultant.
Frequently asked questions
How long does ISO 27001 usually take for a SaaS start-up?
It depends on how much structure you already have, but a small SaaS team can often build a workable system over 60 to 90 days if scope is kept tight and evidence is collected as part of normal work.
What evidence should a small SaaS company start collecting first?
Start with the basics: scope, risk records, asset lists, access reviews, change approvals, incident records, backup checks and supplier information. These give you the strongest foundation for the rest of the work.
Comments are closed