
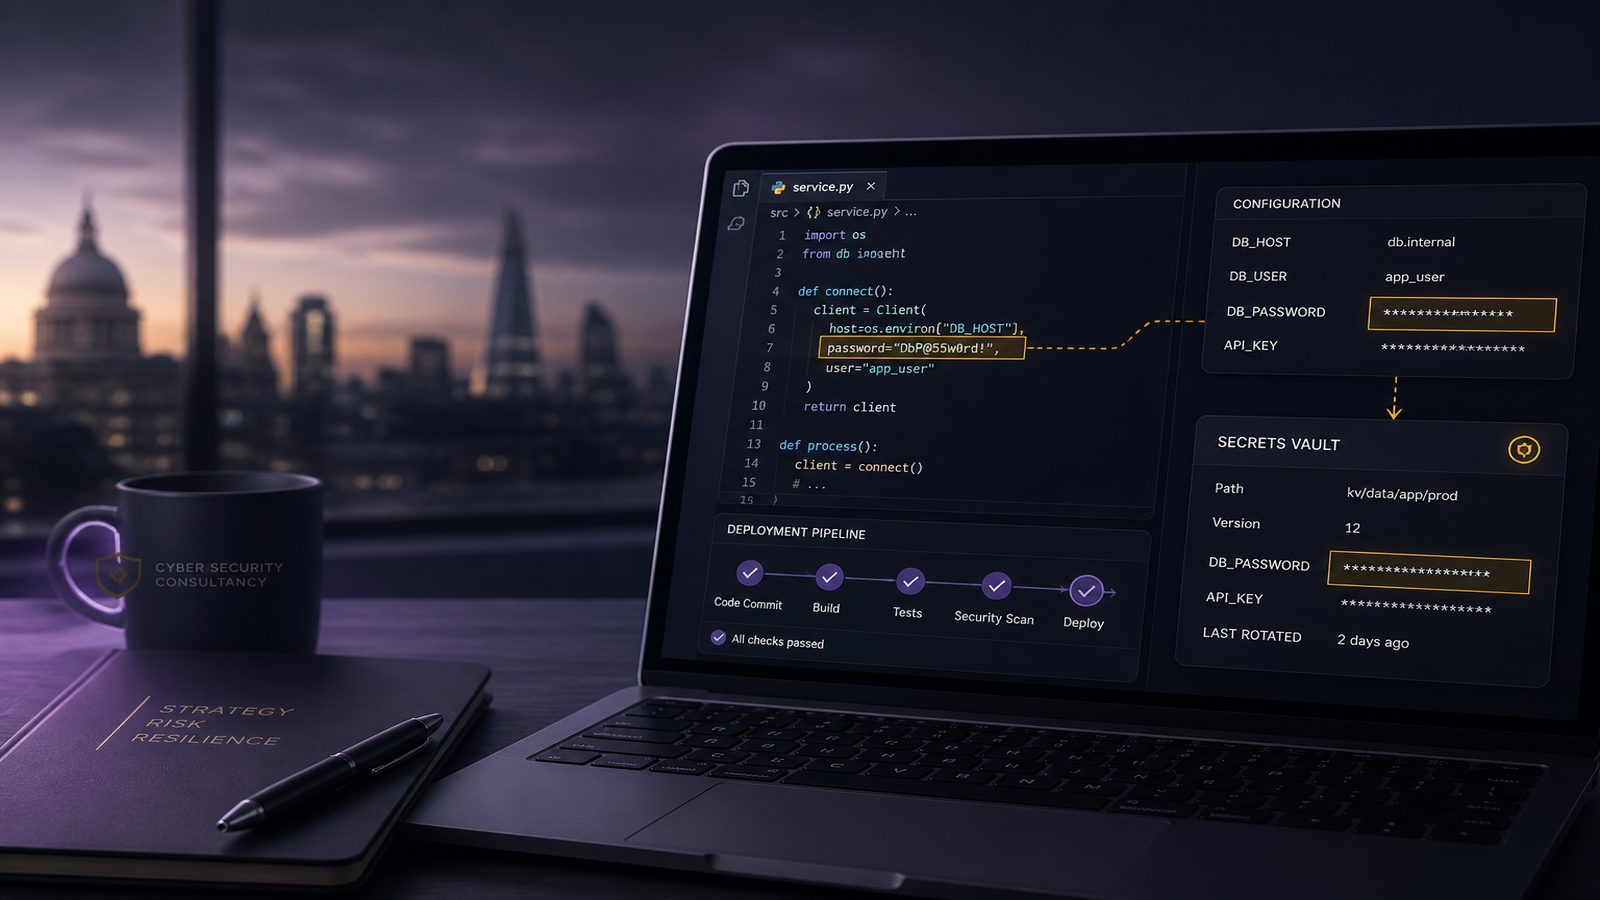
Risks of hard-coded secrets in software
For many UK SMEs, software is now part of day-to-day business operations, whether it supports sales, customer service, finance, or operations. That makes the way software is built and maintained a business issue, not just a technical one. One of the most common and avoidable mistakes is putting secrets directly into code or related files.
A secret is any value that should stay private because it gives access to something valuable. That might be a password, an application token, an API key, or a connection string. If that information is written into software and later exposed, the impact can spread well beyond the original mistake. It can affect customers, suppliers, revenue, and reputation.
This article explains the risks of hard-coded secrets in software in plain English, where they usually appear, how they get exposed, and what SMEs can do to reduce the risk without slowing delivery.
Key takeaways
- Hard-coded secrets can expose multiple systems at once, turning a small coding mistake into a wider business incident.
- The main risks are downtime, fraud, data loss, and reputational damage if a secret is copied or exposed.
- Keep secrets out of code, store them in a dedicated secrets manager, and limit who can access them.
- Rotate any secret that may have been exposed and remove credentials that are no longer needed.
What hard-coded secrets are and why they matter
Simple definition in plain English
Hard-coded secrets are private values written directly into source code, scripts, or configuration files instead of being stored securely elsewhere. In practice, that means the secret is fixed in the software itself rather than being supplied safely when the software runs.
This is risky because code is often copied, shared, reviewed, backed up, and deployed in many places. Once a secret is embedded in that flow, it becomes much harder to control. Even if the code is later changed, older copies may still exist in repositories, backups, test systems, or developer machines.
Common examples in business software
In an SME environment, hard-coded secrets often include:
- Passwords for databases or admin accounts
- Application keys used to connect to cloud services
- Tokens for payment, messaging, or customer support tools
- Certificates or private keys used to prove identity between systems
- Test credentials left in scripts or sample files
These values are often added for convenience during development, then forgotten. The problem is not only that they are visible in code. It is that they are easy to copy into other places and difficult to track once they have spread.
Why hard-coded secrets create business risk
How one exposed secret can affect multiple systems
A single exposed secret can open the door to more than one system. For example, one application token might allow access to a cloud platform, a database, and a third-party service. If that token is reused across environments, the same mistake can affect development, testing, and live systems at the same time.
That is why hard-coded secrets are not just a coding issue. They can become a route into core business services. If an attacker or unauthorised user finds one secret, they may be able to use it to reach other connected systems that trust it.
Likely business impacts: downtime, fraud, data loss, and reputation damage
The business impact depends on what the secret protects, but common outcomes include:
- Service disruption if systems have to be shut down or rebuilt
- Fraud or misuse if a payment or account token is abused
- Data loss or unauthorised access if a database credential is exposed
- Customer concern if sensitive information is accessed or leaked
- Reputational damage if the issue becomes public or affects a client
For an SME, even a short interruption can be costly. Staff may lose time investigating the issue, customers may be unable to use a service, and the business may need urgent support from developers or external specialists. If the secret is tied to a supplier or customer integration, the problem can also affect relationships and contract confidence.
Hard-coded secrets can also create a false sense of security. A team may believe a system is protected because access is limited in one place, while the same secret is sitting in plain text elsewhere. That is why secure development needs to be treated as part of business risk management. If you are building or buying software, it is worth considering the wider secure development approach described in Secure Software Development – Why It Matters.
Where hard-coded secrets usually appear
Source code and configuration files
The most obvious place is source code. Developers may place a password, token, or key directly in a file so the software works quickly during testing. Configuration files are another common location, especially where teams want to keep settings separate from the main code but still store them in the same project.
This is especially common in small teams where people wear multiple hats and deadlines are tight. The issue is understandable, but it should not become normal practice. If secrets are in code or configuration files, they are more likely to be copied, committed to version control, or shared with others who do not need them.
Scripts, build pipelines, and test environments
Secrets also appear in scripts used to deploy software, run tests, or connect systems together. Build pipelines can be another weak point if credentials are added directly into automated steps. Test environments are particularly risky because people often treat them as temporary and less sensitive, even though they may still contain real data or access to real services.
It is also common for teams to use the same secret in more than one place because it is easier to manage in the short term. That convenience can create a bigger problem later, because one exposed value may affect several environments at once.
How secrets get exposed in real-world operations
Shared code repositories and copied files
Secrets are often exposed through everyday working habits rather than a dramatic attack. A file may be copied into a shared folder, checked into a code repository, or sent to a colleague for troubleshooting. Once that happens, the secret may be visible to more people than intended.
Version control systems can make this worse because they keep a history of changes. Even if a secret is removed from the latest version, it may still exist in earlier commits or branches. That means the problem can remain long after the team thinks it has been fixed.
Backups, logs, and developer workstations
Backups can preserve secrets that were supposed to be temporary. Logs may also capture values that were never meant to be recorded, especially if an application prints configuration details during startup or error handling. Developer workstations are another common exposure point because they often contain local copies of code, test files, and credentials.
For SMEs, this matters because the same small set of people often manage development, deployment, and support. That makes it easier for secrets to spread across laptops, shared drives, and cloud tools without anyone noticing. Good control is less about blame and more about reducing the number of places where a secret can live.
What attackers or unauthorised users can do with exposed secrets
Access cloud services, databases, or third-party tools
If a secret is exposed, it may allow access to cloud services, databases, messaging platforms, payment systems, or customer support tools. The exact impact depends on the permissions attached to the secret. Even a limited account can still be useful if it provides a starting point into a wider environment.
Unauthorised access is not always obvious at first. A stolen token may be used quietly, or a password may be tested later. That delay can make the issue harder to spot and investigate.
Move through connected systems or misuse trusted integrations
Many business systems are connected through trusted integrations. That is useful for efficiency, but it also means one exposed secret can be used to move between systems that trust each other. An attacker may not need to break in through the front door if a trusted connection is already available.
This is one reason why hard-coded secrets are so important to address early. They can turn a small mistake into a wider incident because they sit at the point where systems, suppliers, and business processes meet. If your organisation relies heavily on third-party tools, it is also worth reviewing the broader supply chain angle in How third-party software introduces cyber risk for UK SMEs.
How to reduce the risk without slowing delivery
Use a dedicated secrets manager instead of storing values in code
The safest approach is to keep secrets out of code and store them in a dedicated secrets manager. This is a secure place designed to hold private values and provide them to applications when needed. The software then reads the secret at run time rather than carrying it around in the codebase.
For SMEs, the important point is not the brand of tool. It is the principle. Keep secrets in one controlled place, limit who can view them, and make sure applications only receive the access they need. If you are building this capability, our guide to secrets management using key vaults and HSMs explains the practical options in more detail.
Limit access, rotate secrets, and remove unused credentials
Access should be restricted to the smallest practical group of people and systems. Not every developer, tester, or contractor needs access to every secret. If a secret is no longer needed, remove it. If it may have been exposed, change it quickly. This is often called rotation, which simply means replacing the old value with a new one.
It is also sensible to review whether some secrets are still in use at all. SMEs often keep old credentials around because nobody wants to break a live integration. A regular review helps remove forgotten accounts and reduces the number of places an attacker could try.
Practical checks for SMEs
Review code, repositories, and deployment scripts
A practical first step is to look for secrets in the places where they are most likely to hide. Check source code, configuration files, deployment scripts, and any shared repository used by the team. Pay attention to old branches, sample files, and test data as well as the main application code.
It is worth making this a routine check rather than a one-off clean-up. Secrets can slip back in when teams are under pressure, especially during urgent fixes or new releases.
Check who can access secrets and how often they are changed
Ask three simple questions:
- Who can see each secret?
- Where is it stored?
- When was it last changed?
If the answer is unclear, that is a sign the process needs tightening. You do not need a large security programme to improve this. Many SMEs can make meaningful progress by tightening access, documenting where secrets live, and setting a regular review cycle.
If your team is still building secure development habits, it may help to revisit the basics in Secure coding principles explained for product teams and then add simple checks into everyday delivery.
A simple action plan for teams
Find and replace hard-coded secrets
Start by identifying where secrets are currently stored. Replace hard-coded values with secure references to a secrets manager or another controlled storage method. Remove old copies from code, scripts, and test files where possible.
Then rotate any secret that may already have been exposed. If a value has been in code, in a shared file, or in a public repository, assume it should be treated as compromised until proven otherwise. That is a cautious but sensible position for business protection.
Set rules for secure storage and handling going forward
Once the immediate clean-up is done, set a simple rule: secrets must not be stored in code. Back that up with a practical process for storing, approving, and changing them. Make sure developers, contractors, and anyone who deploys software understands the rule and knows where to put secrets instead.
It also helps to add a basic check before release, so secrets are spotted before software goes live. For growing teams, that kind of control is often more effective than relying on memory or good intentions.
When to get outside help
If secrets are spread across multiple systems
If you suspect secrets are already spread across code, repositories, backups, and cloud tools, it may be difficult to clean up safely without help. The main challenge is not just finding the secrets. It is understanding which ones are still active, which systems depend on them, and what needs to be changed first.
Outside support can help you reduce the risk in a structured way and avoid accidental disruption to live services. That is often useful when the business depends on a small number of people who already have full workloads.
If you need help improving secure development practices
If hard-coded secrets are only one part of a wider development issue, it may be time to improve the overall secure development process. That can include clearer rules for code review, safer release steps, better access control, and more consistent handling of sensitive information.
For SMEs that want a practical, risk-based approach, external advice can help turn a one-off fix into a repeatable way of working. If that would be useful, you can speak to a consultant for support tailored to your environment.
Conclusion
Hard-coded secrets are easy to overlook because they often start as a convenience. The business risk appears later, when those secrets are copied, exposed, or reused in more places than intended. At that point, a small coding shortcut can become a wider incident involving downtime, fraud, data loss, or reputational harm.
For UK SMEs, the most practical response is straightforward. Keep secrets out of code, store them in a dedicated secrets manager, limit access, rotate them when needed, and build simple checks into everyday development and release work. Those steps do not need to be complicated to be effective.
If you want help reviewing your current approach or improving secure development practices across your team, a short conversation with an experienced adviser can be a sensible place to start.
Frequently asked questions
What is the meaning of risk?
Risk is the chance that something bad will happen and the impact it would have if it does. In software, that usually means asking how likely a problem is and how much it could cost the business.
What are examples of risk in software?
Examples include exposed passwords, insecure data handling, service outages, unauthorised access, and software defects that affect customers or operations. Hard-coded secrets are a good example because they can create several of these problems at once.
Comments are closed