IEC 62443-3-3 is where many OT security programmes move from theory into engineering detail. It takes the high-level idea of securing an industrial system and breaks it into system security requirements that can be designed, implemented, tested and evidenced. For UK SMEs running manufacturing lines, utilities assets or other operational technology environments, the standard is most useful when it is translated into concrete controls that fit the plant, the process and the maintenance model.
This article focuses on applying IEC 62443-3-3 system security requirements in practice. It does not try to restate the standard. Instead, it shows how to turn requirements into an implementation plan, how to handle common OT constraints, and how to keep the result maintainable. If you are still shaping the broader architecture, it can help to start with IEC 62443 explained for manufacturing organisations and zone and conduit modelling under IEC 62443, because the system requirements only make sense once the trust boundaries are clear.
Key takeaways
- IEC 62443-3-3 becomes useful when you translate each requirement into a specific control, owner and evidence source.
- In OT environments, segmentation, controlled remote access and hardened engineering workstations usually deliver the biggest risk reduction first.
- Monitoring should focus on meaningful changes to authentication, configuration, programming activity and network flows, not raw log volume.
- Legacy devices rarely support every requirement directly, so compensating controls and documented exceptions are often necessary.
- Backups, restoration testing and review cadence are part of the control set, not separate housekeeping tasks.
What IEC 62443-3-3 covers and where it fits in an OT security programme
IEC 62443-3-3 sits at the system level. That means it is concerned with the security properties of the industrial system as a whole, not just a single device or a single software component. In practice, that system may include PLCs, HMIs, engineering workstations, historians, remote access paths, industrial switches, jump hosts and the supporting Windows or Linux infrastructure around them.
The standard is best used after you have defined zones, conduits and security level targets. Zones group assets with similar risk and trust assumptions. Conduits are the controlled communication paths between those zones. Security level targets then tell you how much resistance the system needs against different attacker capabilities. If you have not yet set those targets, it is worth aligning them first using setting security level targets under IEC 62443.
System requirements differ from component and product requirements in an important way. A product may support a feature such as account lockout, secure boot or certificate-based authentication, but the system requirement is about whether the overall deployed design actually uses those features in a way that reduces risk. A technically capable device does not create a secure system by itself. The system design, configuration, operational process and monitoring model all have to work together.
How to turn system security requirements into an implementation plan
The most practical way to approach IEC 62443-3-3 is to treat it as a control design exercise. Start with the asset, process and trust boundary context. Identify what the system does, what would happen if it failed, and which parts of the environment are safety-critical, production-critical or merely supporting. In OT, availability and safety often matter as much as confidentiality, so the design has to reflect operational reality rather than generic IT assumptions.
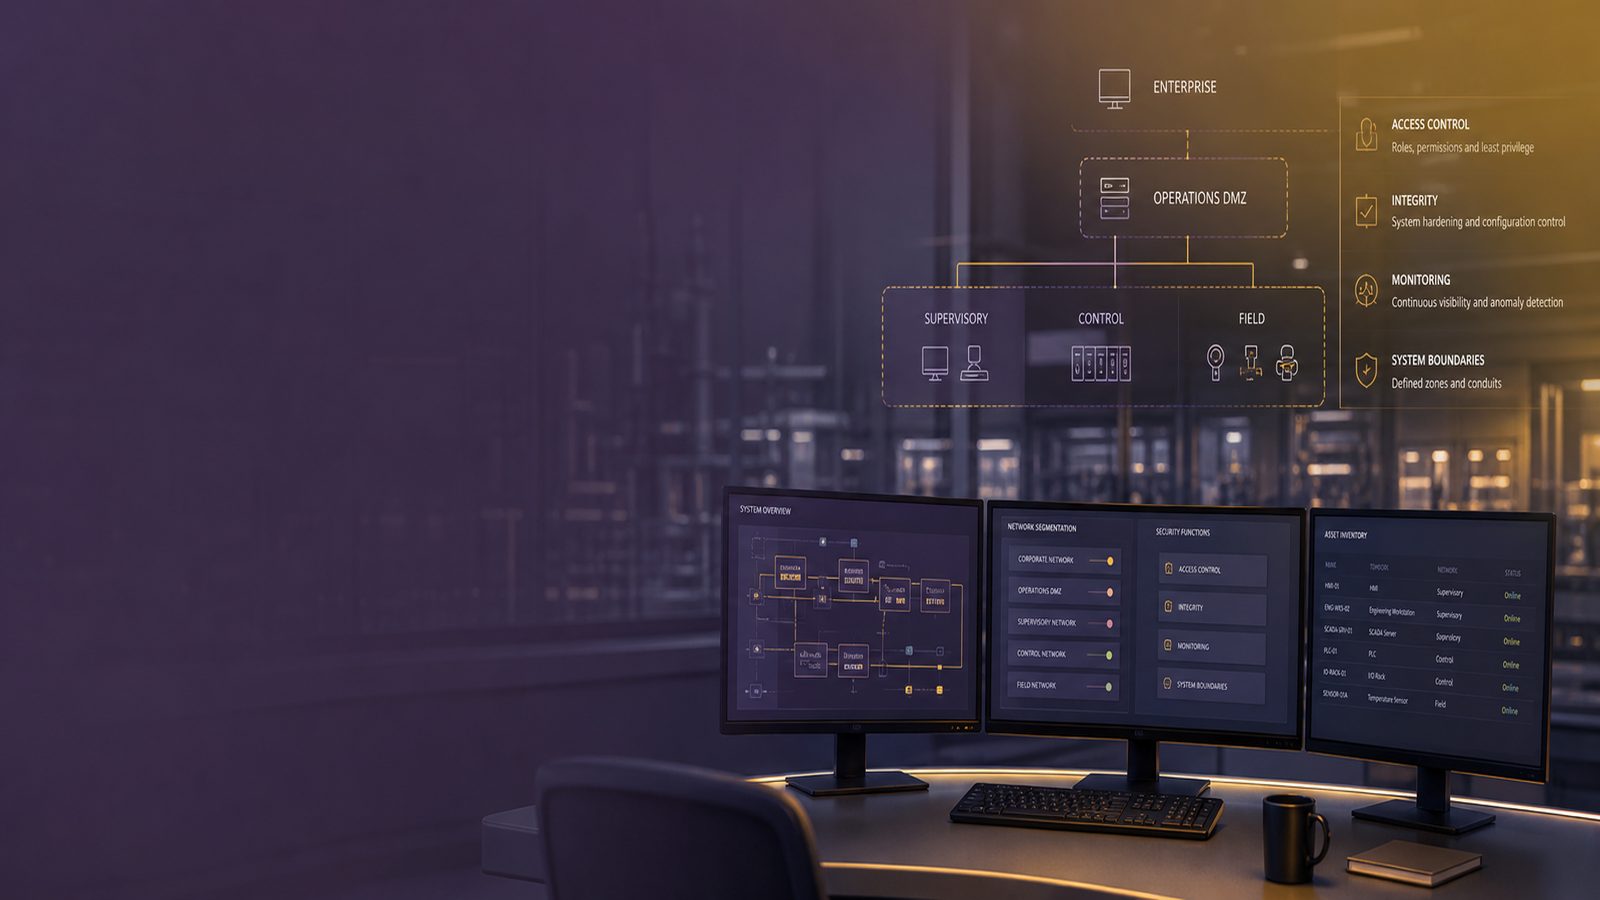
A useful starting point is a simple system map that shows: the assets in scope, the users and service accounts that interact with them, the communication flows between zones, the remote access routes, and the dependencies on identity services, patching, backups and logging. A data-flow view is often enough to expose where the real control points are. If you need a structured way to build that picture, applying data-flow diagrams to security threat modelling is a good companion approach.
Once the context is clear, translate each relevant requirement family into three things: a control, an owner and an evidence source. For example, if a requirement implies strong authentication, the control might be certificate-based remote access through a jump host, the owner might be OT infrastructure, and the evidence might be configuration exports, access logs and periodic review records. This is where many programmes become manageable. Requirements stop being abstract and become a list of engineering tasks with testable outcomes.
It also helps to record whether a requirement is implemented directly, inherited from another layer, or met through a compensating control. In OT, you will often inherit controls from network design, physical security or a managed remote support platform. That is acceptable if the dependency is explicit and the residual risk is understood.
Applying the core requirement families in practice
Identification and authentication, account handling and access control
Strong identity is usually the first place to start. Shared accounts, vendor default credentials and unmanaged local administrator access are still common in industrial environments. The goal is not to force every legacy device into a modern identity stack, but to make sure that human and machine access is attributable, limited and reviewable.
For operator and engineering access, use named accounts wherever the platform supports them. Where a device only supports local accounts, reduce the number of privileged users, document the reason, and rotate credentials through a controlled process. For remote support, prefer a jump host or bastion in a dedicated management zone, with MFA on the entry point and session logging on the way through. If the device cannot do MFA itself, enforce it at the access gateway.
Role-based access control should reflect operational duties, not organisational hierarchy. Operators, maintenance engineers, control engineers and third-party integrators should not share the same privilege set. In many plants, the most effective control is a small number of tightly scoped roles combined with time-bound elevation for maintenance windows. If you are already using least privilege patterns in your broader environment, the same logic applies here, although the implementation will usually be more constrained than in office IT.
For service accounts, avoid interactive logon where possible, disable unnecessary privileges, and store credentials in a managed secrets platform or equivalent secure vault. Where a device or application requires a fixed credential, make the dependency explicit, limit network reachability, and monitor for use outside expected change windows.
System integrity, data confidentiality and restricted data flow
System integrity in OT is about preventing unauthorised change to logic, configuration and firmware, while still allowing legitimate engineering work. A practical pattern is to separate normal operations from maintenance activities. Engineering workstations should not be used for general browsing or email. They should be hardened, application allowlisted where feasible, and connected only to the systems they need to manage.
For PLCs, HMIs and control servers, focus on reducing the chance of unauthorised modification. That can include signed firmware where supported, change approval for logic downloads, restricted write access to configuration repositories, and network controls that only allow programming traffic from approved engineering stations. If you need a broader hardening baseline for Windows and Linux hosts in the OT estate, reducing attack surface using system hardening techniques is relevant, although OT systems often require more careful exception handling than standard office endpoints.
Data confidentiality is often less about secrecy in the classic IT sense and more about protecting recipes, setpoints, production data and operational telemetry from tampering or exposure. Use TLS where supported for management and data transfer, especially between historians, application servers and remote support tooling. Where mutual authentication is available, use it for machine-to-machine links. For older protocols that do not support encryption, compensate with segmentation, strict conduit rules and monitoring of who can talk to whom.
Restricted data flow is one of the most valuable system-level controls in IEC 62443. In practice, this means that traffic between zones should be explicit, minimal and justified. Do not allow flat routing between business IT and control networks. Use firewall rules based on source, destination, port and protocol, and review them against actual process needs. If you are designing the network layer in more detail, segmenting OT networks with the Purdue model and IEC 62443 zones is a useful reference point.
Timely response to events, resource availability and backup recovery
OT security is not just about prevention. The system also needs to respond to events and remain available. That means logging, alerting, resilience and recovery planning are part of the requirement set, not optional extras.
For event response, define what constitutes a security-relevant event in the OT context. Examples include failed logons to engineering stations, unexpected logic downloads, changes to firewall rules, new remote sessions, configuration changes outside maintenance windows, and loss of communication between key assets. The response does not have to be fully automated. In many plants, the first step is a clear escalation path to operations, engineering and security so that the right people can decide whether to isolate, investigate or continue running.
Resource availability is often the hardest requirement family to implement because industrial systems are sensitive to latency, downtime and vendor support constraints. Avoid controls that create unnecessary fragility. For example, deep packet inspection can be useful, but only if it is deployed in a way that does not interrupt control traffic. Similarly, endpoint protection on HMIs and servers should be tested in a representative environment before broad rollout. A control that causes process instability is not a good control, even if it looks strong on paper.
Backup and recovery need special attention in OT because restoring a system is not the same as restoring a laptop. You need backups of controller logic, HMI configurations, historian data, engineering project files and relevant operating system images. Test restoration under realistic conditions, including the time it takes to validate that the recovered system is safe to reconnect. If you have not already done this, testing backup restoration under incident conditions is worth reading alongside this article.
Design patterns that work in industrial environments
Segmentation, jump hosts and remote access control
One of the most reliable patterns for implementing IEC 62443-3-3 is to place a controlled access layer between users and the production system. A jump host in a management zone can provide a single, monitored path for administration, vendor support and engineering access. That host should be hardened, patched, logged and protected with MFA. It should also be the only system allowed to reach certain control assets for administrative purposes.
For third-party access, use time-bound approvals and session recording where practical. Remote support should be disabled by default and enabled only when needed. If a vendor insists on always-on access, challenge that design and look for alternatives such as outbound-only support tunnels, brokered sessions or scheduled maintenance windows. The aim is to reduce standing access and make every privileged session visible.
Network devices matter too. Industrial switches, firewalls and routers should have management interfaces isolated from production traffic. SNMP, SSH, HTTPS and syslog should be restricted to management sources only. Default credentials and shared admin accounts on network gear are a common weak point, especially in smaller sites where operational convenience has historically outweighed control discipline.
Hardening engineering workstations, HMIs and control servers
Engineering workstations are often the highest-value target in an OT environment because they can change logic, download configurations and reach many assets. Treat them as privileged systems. Remove unnecessary software, block internet access where possible, disable unneeded services, and control removable media. If USB use is unavoidable, apply scanning and approval rules rather than leaving the port open by default.
HMIs and control servers should be built from standard images where possible, with a documented baseline and a controlled change process. Local admin rights should be tightly limited. Application allowlisting can be effective, but only if the operational overhead is understood. In some environments, a simpler combination of restricted user rights, patch discipline and network segmentation is more sustainable.
Where the vendor stack is old or brittle, the design goal is not perfection. It is to reduce exposure without breaking the process. That may mean compensating controls such as physical access restriction, one-way data transfer, dedicated maintenance laptops, or stricter conduit filtering. The key is to document why the exception exists and what makes the residual risk acceptable for the business.
Monitoring and detection considerations for OT teams
Monitoring in OT should be selective and operationally safe. The objective is to detect misuse, unauthorised change and abnormal communication without overwhelming the team or disturbing the process. Start with the assets that matter most: controllers, historians, engineering stations, remote access gateways and network devices.
Useful telemetry includes authentication events, configuration changes, firmware downloads, project upload and download actions, remote session starts and ends, firewall denies, and changes to device state that should only happen during maintenance. Where the platform supports it, forward logs to a SIEM or central log platform. If the system cannot emit rich logs, collect what it can and supplement with network telemetry.
For OT protocols, focus on deviations from normal behaviour rather than trying to decode every packet. A sudden increase in write commands, unexpected programming traffic, or a new source talking to a controller can be more important than the payload itself. This is where network detection and response tools can help, provided they are tuned for industrial traffic patterns. If you want a more protocol-specific view, monitoring OT protocols such as Modbus and DNP3 for anomalies goes into more detail.
Detection logic should be built around operational baselines. A maintenance window, a firmware update and a production shift change can all look unusual if you do not model them properly. Work with engineering teams to define what normal looks like, then alert on meaningful deviations. False positives are expensive in OT because they can distract staff from real issues and reduce trust in the monitoring stack.
Common implementation gaps and trade-offs
The most common gap is assuming that a feature exists because the vendor brochure says so. In reality, the feature may be limited, licensed separately or unavailable on older hardware. Always verify what is actually supported on the deployed version, not just the current product line.
Legacy devices are another frequent constraint. Some controllers cannot support modern authentication, encryption or logging. In those cases, compensate with network isolation, physical security, strict access paths and monitoring. Do not let the absence of one control prevent you from implementing the others.
There is also a trade-off between availability and security. In a live plant, the wrong control can create more risk than it removes. The answer is not to avoid security controls, but to stage them carefully, test them in a representative environment and involve operations early. A control that is technically sound but operationally unworkable will not survive contact with production.
How to evidence progress and keep the programme maintainable
Evidence in an OT security programme should be practical and repeatable. Keep a control map that links each system requirement to the implemented control, the owner, the test method and the evidence source. This can be a spreadsheet, a GRC tool or a simple document set, as long as it is maintained.
Review cadence matters. Revisit the control set after major changes, such as a new line, a vendor upgrade, a network redesign or a significant incident. Also review exceptions regularly. A compensating control that made sense six months ago may no longer be adequate if the system has changed.
Where a requirement cannot be met, record the risk acceptance decision, the reason, the compensating controls and the review date. That is not about creating bureaucracy. It is about making sure the organisation understands what it is relying on and why. For teams that already manage broader governance and assurance work, the same discipline used in mapping NIST CSF to ISO 27001 in practice can be adapted to OT, even though the control details are different.
Practical checklist for first-pass adoption
If you are starting from a small OT environment, a sensible first pass is to focus on the controls that give the most value with the least disruption:
- Define the system boundary, zones, conduits and trust assumptions before selecting controls.
- Remove shared administrative access where possible and put remote access behind a jump host with MFA.
- Restrict write paths to controllers, HMIs and engineering assets so that only approved systems can make changes.
- Harden engineering workstations and separate them from general-purpose office use.
- Collect logs from the assets that can provide them, then baseline normal activity before writing alerts.
- Test backups and restoration for controller logic, project files and supporting servers.
- Document exceptions, compensating controls and review dates so the design remains maintainable.
For the next 90 days, prioritise visibility, access control and recovery. Those three areas usually deliver the most immediate reduction in risk. Once they are stable, you can refine integrity controls, protocol monitoring and more advanced response workflows.
IEC 62443-3-3 is most effective when it is treated as an engineering framework rather than a compliance exercise. The standard gives you a structured way to think about identity, access, integrity, confidentiality, availability and response in an industrial setting. The practical challenge is to implement those ideas without disrupting the process. That is achievable if you start with the system context, design for the real constraints of the plant, and keep the control set simple enough to operate consistently.
If you would like help turning IEC 62443-3-3 into a workable OT control plan for your environment, speak to a consultant.
Frequently asked questions
What is the difference between IEC 62443 and ISO 27001?
IEC 62443 is focused on industrial automation and operational technology, with requirements that reflect plant, process and control-system realities. ISO 27001 is a broader information security management standard that applies across many types of organisation and information assets. In practice, many organisations use ISO 27001 for governance and IEC 62443 for OT-specific control design.
What are the three fundamental elements of an effective security program for information systems?
A practical answer is people, process and technology. People define and operate the controls, process makes them repeatable and reviewable, and technology enforces or supports them. In OT, those three elements also need to be aligned with safety and availability requirements.
Comments are closed